Black Friday Early Access - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save75geek

NSE7_SOC_AR-7.6 Fortinet NSE 7 - Security Operations 7.6 Architect Questions and Answers

Questions 4

Refer to this partial incident output:

Condition: if this pattern occurs within any 1800-second time window.

Host Interface Name: Red Hat VirtIO Ethernet Adapter

Recv Packet Errors: 0

Sent Packet Errors: 0

Recv Packet Discards: 37

Sent Packet Discards: 0

Recv Packet Error Pct: 0.00

Sent Packet Error Pct: 0.00

Recv Packet Discard Pct: 7.17

Sent Packet Discard Pct: 0.00

Avg Recv Interface Error: 0.00

Avg Sent Interface Error: 0.00

Avg Recv Interface Discard: 16.45

Avg Sent Interface Discard: 0.00

Which conclusion can you make about this incident? Choose one answer.

Options:

A.

It was triggered by a baseline profile incident rule.

B.

It was triggered from a FortiAI machine learning rule.

C.

It was triggered by a correlation rule.

D.

It was triggered by a lookup table.

Buy Now
Questions 5

Refer to the exhibits.

The DOS attack playbook is configured to create an incident when an event handler generates a denial-of-ser/ice (DoS) attack event.

Why did the DOS attack playbook fail to execute?

Options:

A.

The Create SMTP Enumeration incident task is expecting an integer value but is receiving the incorrect data type

B.

The Get Events task is configured to execute in the incorrect order.

C.

The Attach_Data_To_lncident task failed.

D.

The Attach_Data_To_lncident task is expecting an integer value but is receiving the incorrect data type.

Buy Now
Questions 6

Refer to the exhibit.

You notice that the custom event handler you configured to detect SMTP reconnaissance activities is creating a large number of events. This is overwhelming your notification system.

How can you fix this?

Options:

A.

Increase the trigger count so that it identifies and reduces the count triggered by a particular group.

B.

Disable the custom event handler because it is not working as expected.

C.

Decrease the time range that the custom event handler covers during the attack.

D.

Increase the log field value so that it looks for more unique field values when it creates the event.

Buy Now
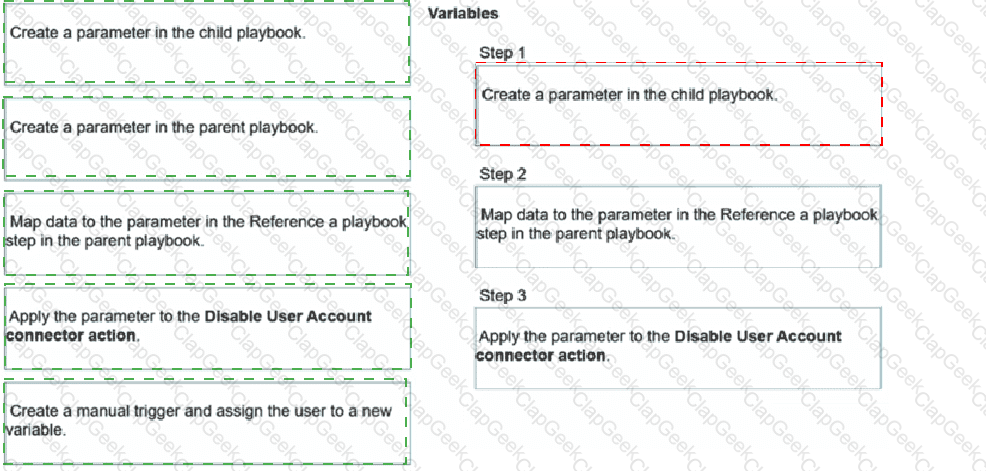
Questions 7

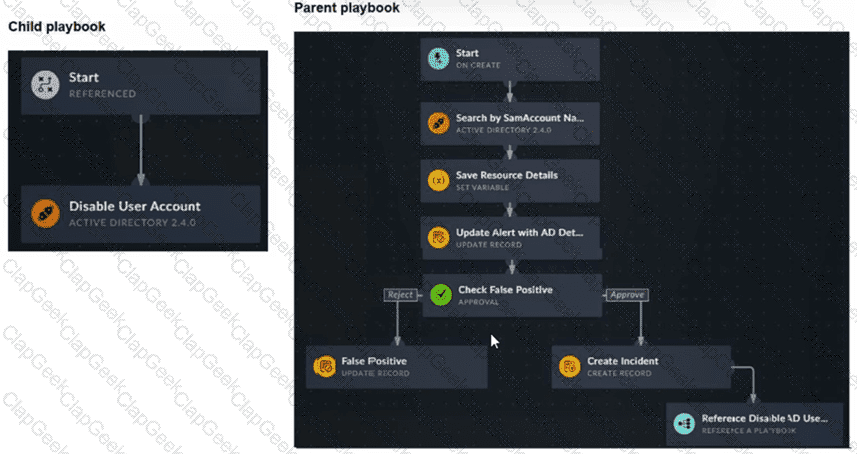
Refer to the exhibits.

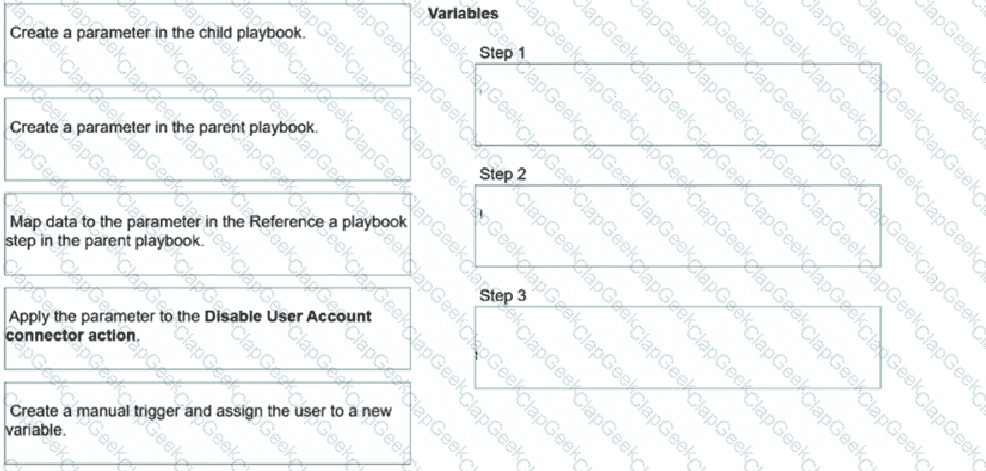
You have a playbook that, depending on whether an analyst deems the alert to be a true positive, could reference a child playbook. You need to pass variables from the parent playbook to the child playbook.

Place the steps needed to accomplish this in the correct order.
Options:

Buy Now
Questions 8

Exhibit:

Which observation about this FortiAnalyzer Fabric deployment architecture is true?

Options:

A.

The AMER HQ SOC team cannot run automation playbooks from the Fabric supervisor.

B.

The AMER HQ SOC team must configure high availability (HA) for the supervisor node.

C.

The EMEA SOC team has access to historical logs only.

D.

The APAC SOC team has access to FortiView and other reporting functions.

Buy Now
Questions 9

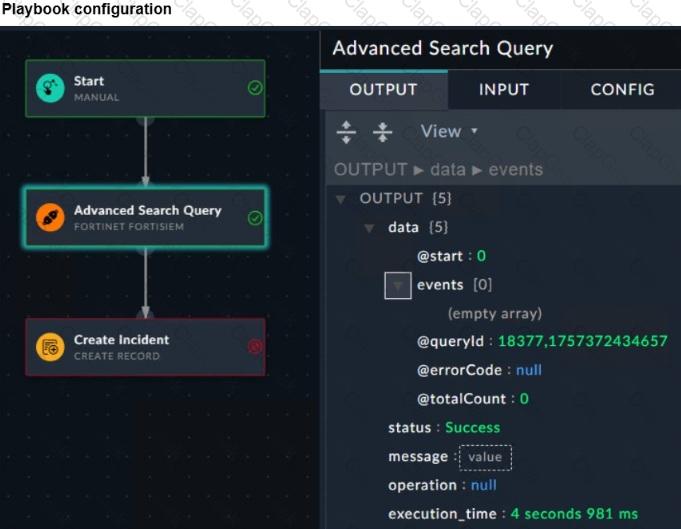
Refer to the exhibit.

You created a threat hunting playbook to perform a search query using the FortiSIEM connector. However, when you run the playbook, you do not see any output. Which step must you take first in your troubleshooting process?

Options:

A.

Confirm that the event logs matching your criteria exist on FortiSIEM.

B.

Configure a Set Variable step to save the output.

C.

Confirm that the FortiSIEM connector is up.

D.

Check the documentation for the input and output for the action.

Buy Now
Questions 10

You are trying to create a playbook that uses source data from ingestion to populate the description field of a task. You successfully saved the source data to a variable called ingestion_data. Now, you must parse the results and extract a list of indicators. Which Jinja expression can accomplish this task? Choose one answer.

Options:

A.

{{ vars.ingestion_data | json_query( " [?type== ' IOC ' ] " ) }}

B.

{{ vars.ingestion_data | to_nice_json | ipaddr | hwaddr | email | hash }}

C.

{{ vars.ingestion_data | type_debug }}

D.

{{ vars.ingestion_data | extract_artifacts }}

Buy Now
Questions 11

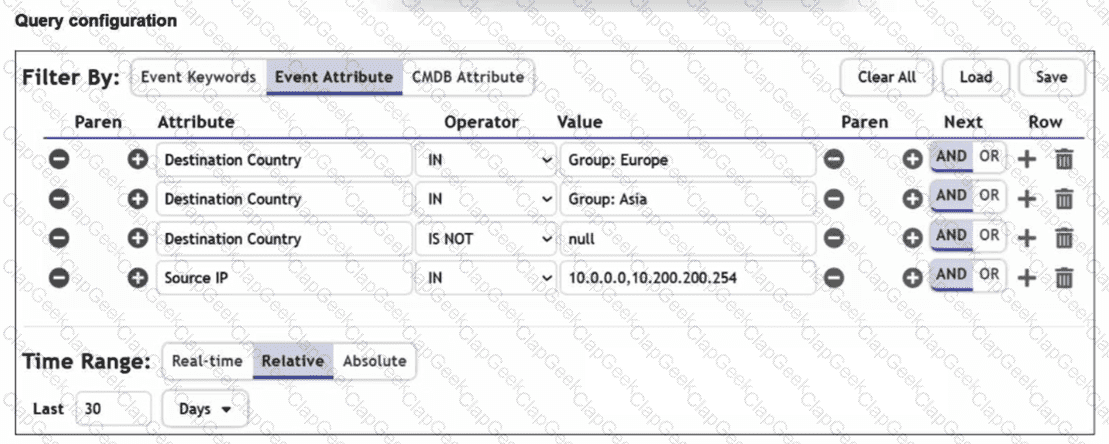
Refer to the exhibit.

You are trying to find traffic flows to destinations that are in Europe or Asia, for hosts in the local LAN segment. However, the query returns no results. Assume these logs exist on FortiSIEM.

Which three mistakes can you see in the query shown in the exhibit? (Choose three answers)

Options:

A.

The null value cannot be used with the IS NOT operator.

B.

The time range must be Absolute for queries that use configuration management database (CMDB) groups.

C.

There are missing parentheses between the first row (Group: Europe) and the second row (Group: Asia).

D.

The Source IP row operator must be BETWEEN 10.0.0.0, 10.200.200.254.

E.

The logical operator for the first row (Group: Europe) must be OR.

Buy Now
Questions 12

Review the incident report:

An attacker identified employee names, roles, and email patterns from public press releases, which were then used to craft tailored emails.

The emails were directed to recipients to review an attached agenda using a link hosted off the corporate domain.

Which two MITRE ATT & CK tactics best fit this report? (Choose two answers)

Options:

A.

Reconnaissance

B.

Discovery

C.

Initial Access

D.

Defense Evasion

Buy Now
Questions 13

You need to create a nested query in FortiSIEM that satisfies the following conditions:

Find all devices discovered by any FortiSIEM Windows Agent.

From those devices, identify those that have generated Windows Login Failure events.

Which two query components should be used for this nested query? Choose two answers.

Options:

A.

Outer Event Query

B.

Outer CMDB Query

C.

Inner CMDB Query

D.

Inner Event Query

Buy Now
Questions 14

Which three end user logs does FortiAnalyzer use to identify possible IOC compromised hosts? (Choose three answers)

Options:

A.

Web filter logs1

B.

Email filter logs

C.

DNS filter logs2

D.

Application filter logs

E.

IPS logs

Buy Now
Questions 15

Refer to Exhibit:

A SOC analyst is creating the Malicious File Detected playbook to run when FortiAnalyzer generates a malicious file event. The playbook must also update the incident with the malicious file event data.

What must the next task in this playbook be?

Options:

A.

A local connector with the action Update Asset and Identity

B.

A local connector with the action Attach Data to Incident

C.

A local connector with the action Run Report

D.

A local connector with the action Update Incident

Buy Now
Questions 16

Which two statements about the FortiAnalyzer Fabric topology are true? (Choose two.)

Options:

A.

Downstream collectors can forward logs to Fabric members.

B.

Logging devices must be registered to the supervisor.

C.

The supervisor uses an API to store logs, incidents, and events locally.

D.

Fabric members must be in analyzer mode.

Buy Now
Questions 17

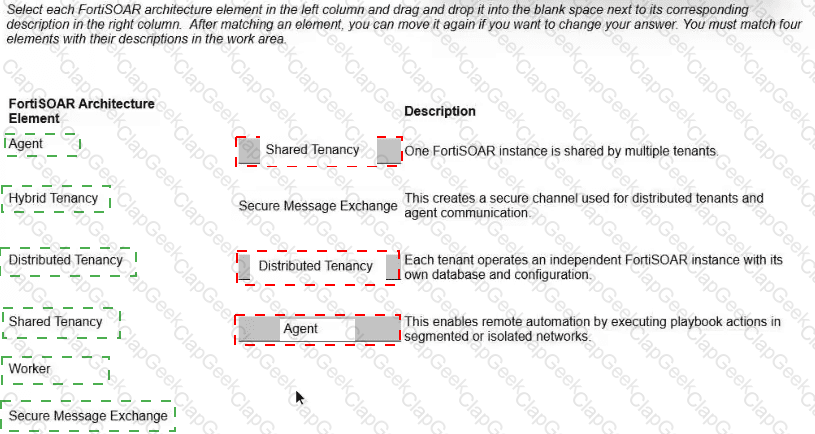
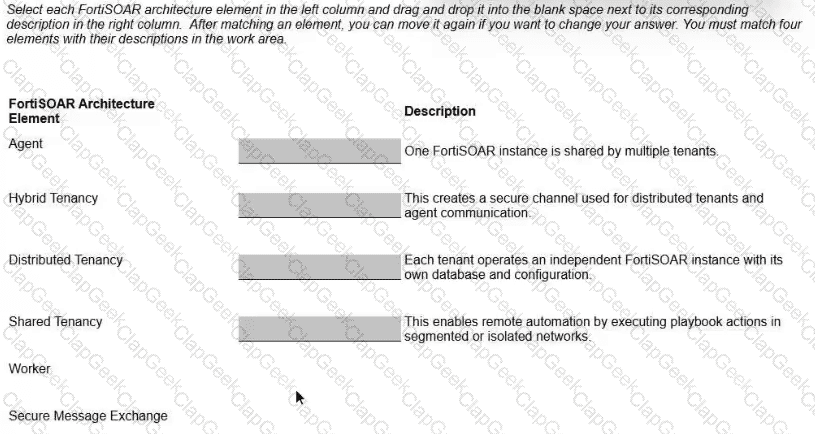
Match the FortiSOAR architecture element to its description.

Select each FortiSOAR architecture element in the left column and drag and drop it into the blank space next to its corresponding description in the right column. After matching an element, you can move it again if you want to change your answer. You must match four elements with their descriptions in the work area.
Options:

Buy Now
Questions 18

Which three are threat hunting activities? (Choose three answers)

Options:

A.

Enrich records with threat intelligence.

B.

Automate workflows.

C.

Generate a hypothesis.

D.

Perform packet analysis.

E.

Tune correlation rules.

Buy Now
Questions 19

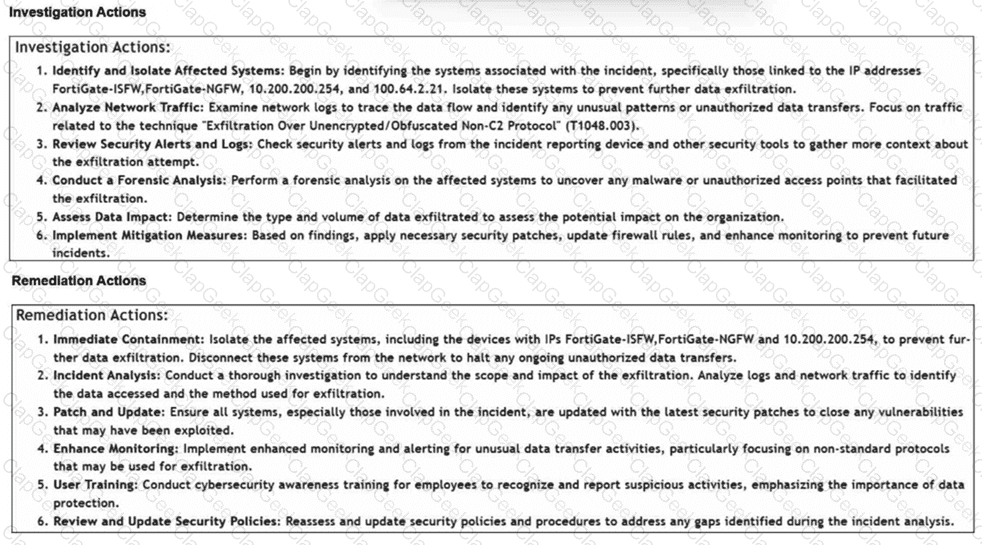
Refer to the exhibits.

How is the investigation and remediation output generated on FortiSIEM? (Choose one answer)

Options:

A.

By exporting an incident

B.

By running an incident report

C.

By using FortiAI to summarize the incident

D.

By viewing the Context tab of an incident

Buy Now
Questions 20

You suspect your organization has been a victim of numerous incidents carried out by the same threat actor. Which option allows you to group the incidents and track them? Choose one answer.

Options:

A.

Add a common tag to correlate them.

B.

Mark one incident as the parent and run a playbook to close the child incidents.

C.

Select those incidents and use the Merge function.

D.

Create a campaign and link related records to it.

Buy Now
Questions 21

You are designing a FortiSOAR hybrid multi-tenant deployment. The architecture must support remote tenant execution and automation inside segmented networks. Which three elements are true for this design? Choose three answers.

Options:

A.

The secure message exchange must be a dedicated instance instead of an embedded one.

B.

The FortiSOAR master cluster can host shared tenants, with strict data isolation between them.

C.

Each tenant or agent has a dedicated, access-controlled space on a secure message exchange for message routing.

D.

FortiSOAR tenant nodes or agents use TCP port 5671 to communicate with the secure message exchange.

E.

FortiSOAR agents are deployed on the master cluster to improve high availability (HA) performance.

Buy Now
Questions 22

Which two playbook triggers enable the use of trigger events in later tasks as trigger variables? (Choose two.)

Options:

A.

EVENT

B.

INCIDENT

C.

ON SCHEDULE

D.

ON DEMAND

Buy Now
Questions 23

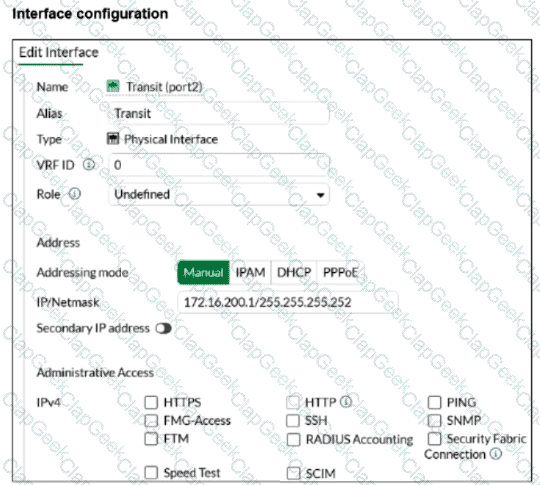
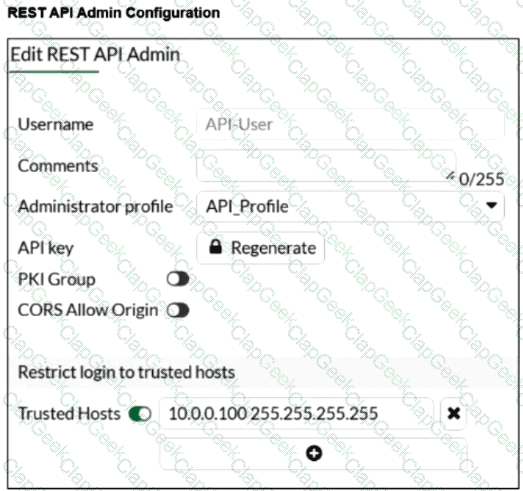
Refer to Exhibits:

You configured the FortiGate connector on FortiSOAR. You want to allow FortiSOAR 10.200.200.160 to perform actions on FortiGate 172.16.200.1. However, the connection attempt fails. Assume that the FortiGate connector is configured correctly on the FortiSOAR side.

Which two configurations are required on FortiGate? Choose two answers.

Options:

A.

HTTPS must be enabled on the FortiGate interface that FortiSOAR will communicate with.

B.

FortiSOAR IP address must be added under Trusted Hosts.

C.

The administrator profile must have System read and write permissions.

D.

The FortiGate interface role must be set to Custom API Endpoint.

Buy Now
Questions 24

Which two statements accurately describe the process to create a new rule from a search using FortiSIEM analytics? Choose two answers.

Options:

A.

Raw event logs cannot be used for incident rule creation.

B.

The incident action is automatically configured based on the event type.

C.

All search filter rows are added into a single subpattern.

D.

The default aggregate condition will always be COUNT(Matched Events) > = 1.

Buy Now
Questions 25

You are using FortiSIEM analytics to reference the configuration management database (CMDB) event type categories with the following requirements:

Attribute: Event Type

Value: Group: Logon Success

Which operator must you use for the analytics search? Choose one answer.

Options:

A.

CONTAIN

B.

IN

C.

HAS

D.

IS

Buy Now
Questions 26

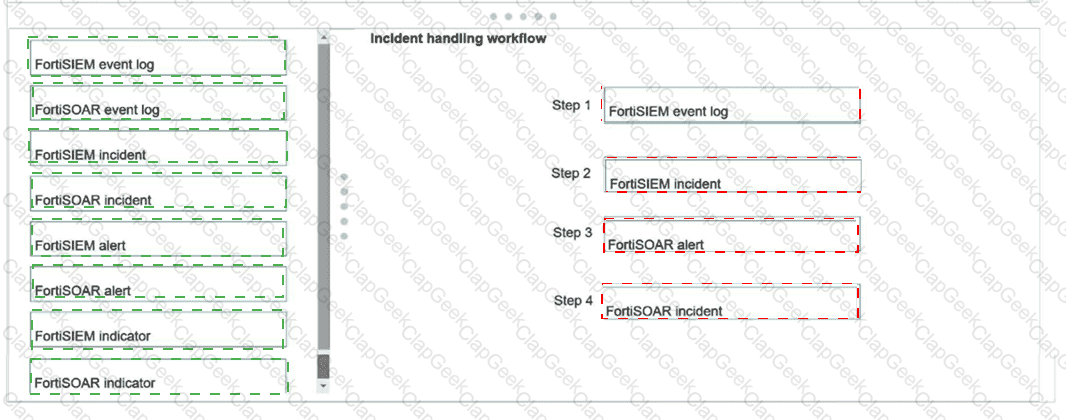
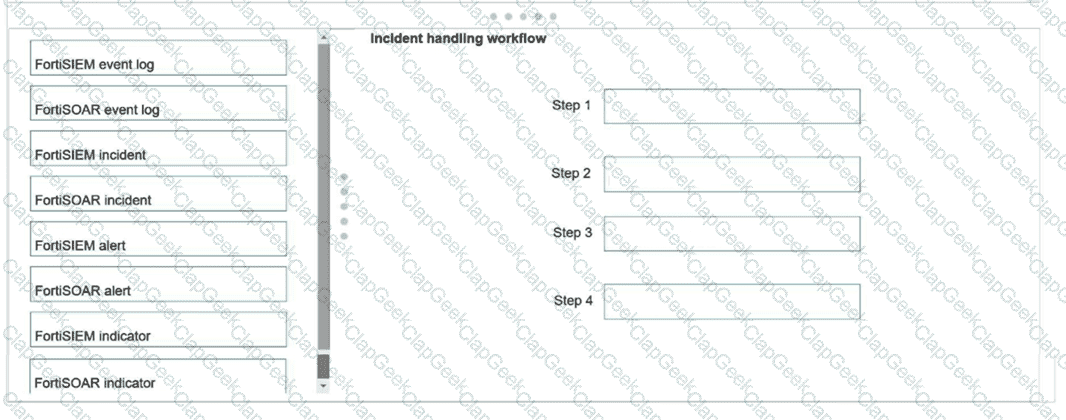
Using the default data ingestion wizard in FortiSOAR, place the incident handling workflow from FortiSIEM to FortiSOAR in the correct sequence. Select each workflow component in the left column, hold and drag it to a blank position in the column on the right. Place the four correct workflow components in order, placing the first step in the first position at the top of the column.
Options:

Buy Now
Questions 27

When configuring an Ingest Bulk Feed playbook step, which two restrictions must you consider? Choose two answers.

Options:

A.

It cannot use step output from a connector action.

B.

It is slower than the Create Record step.

C.

It will not trigger On Create triggers.

D.

It will not trigger On Update triggers.

Buy Now
Questions 28

Your company is doing a security audit To pass the audit, you must take an inventory of all software and applications running on all Windows devices

Which FortiAnalyzer connector must you use?
Options:

A.

FortiClient EMS

B.

ServiceNow

C.

FortiCASB

D.

Local Host

Buy Now
Exam Code: NSE7_SOC_AR-7.6
Exam Name: Fortinet NSE 7 - Security Operations 7.6 Architect
Last Update: Nov 18, 2026
Questions: 96
NSE7_SOC_AR-7.6 pdf

NSE7_SOC_AR-7.6 PDF

$22.5  $89.99
NSE7_SOC_AR-7.6 Engine

NSE7_SOC_AR-7.6 Testing Engine

$28.75  $114.99
NSE7_SOC_AR-7.6 PDF + Engine

NSE7_SOC_AR-7.6 PDF + Testing Engine

$35  $139.99