Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save75geek

NSE7_CDS_AR-7.6 Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect Questions and Answers

Questions 4

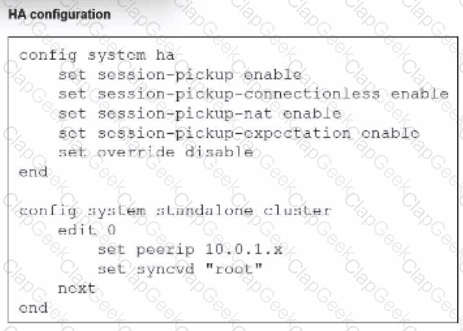
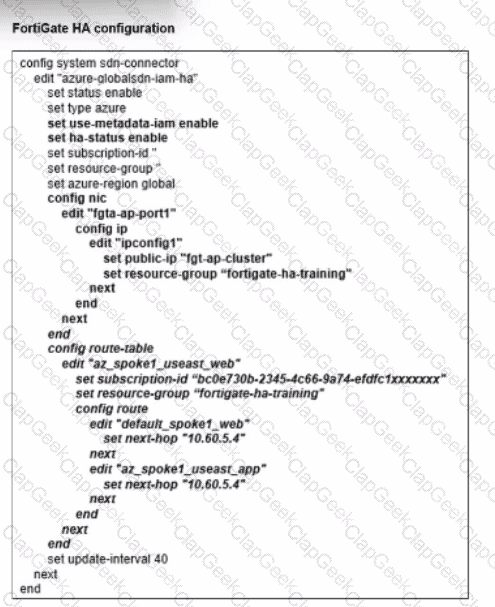
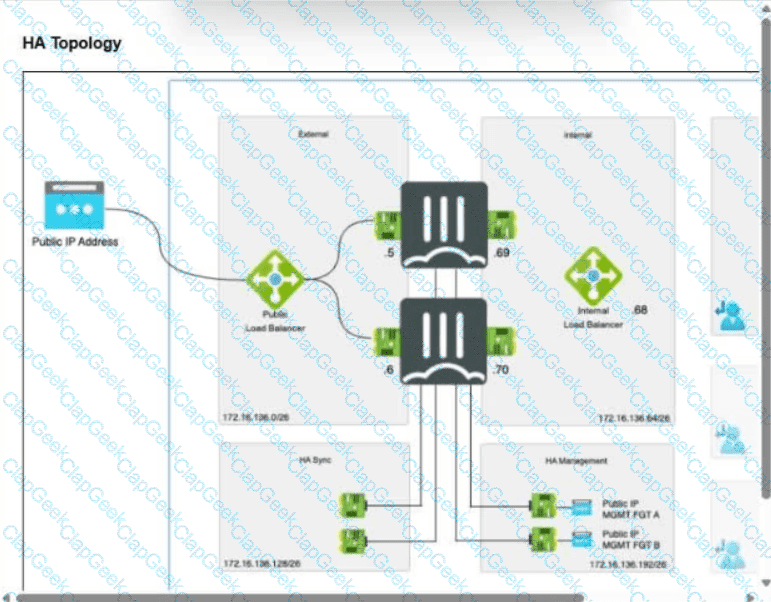
Refer to the exhibit.

You deployed an HA active-active load balance sandwich with two FortiGate VMs in Microsoft Azure.

After the deployment, you prefer to use FGSP to synchronize sessions, and allow asymmetric return traffic. In the environment, FortiGate port 1 and port 2 are facing external and internal load balancers respectively.

What IP address must you use in the peerip configuration?

Options:

A.

The opposite FortiGate port 2 IP address.

B.

The public load balancer port 2 IP address.

C.

The internal load balancer port 1 IP address.

D.

The opposite FortiGate port 1 IP address.

Buy Now
Questions 5

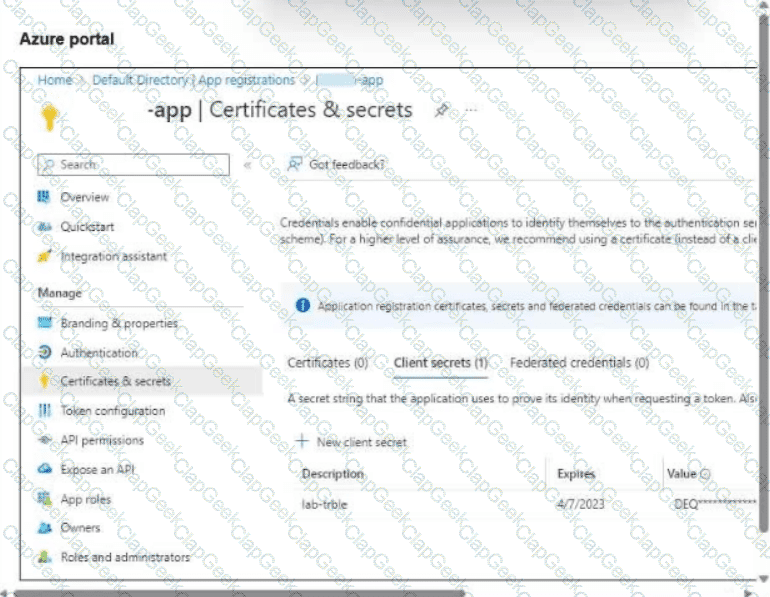
Refer to the exhibit.

An administrator is trying to deploy a FortiGate VM in Microsoft Azure using Terraform. However, during the configuration, the Azure client secret is no longer visible in the Azure portal.

How would the administrator obtain the Azure client secret to configure in Terraform?

Options:

A.

Log in to the Azure CLI as a power user to obtain the client secret.

B.

Create a new Azure account and assign it the Administrator role.

C.

Use the Terraform output file values to obtain the client secret.

D.

Create a new client secret and take note of it.

Buy Now
Questions 6

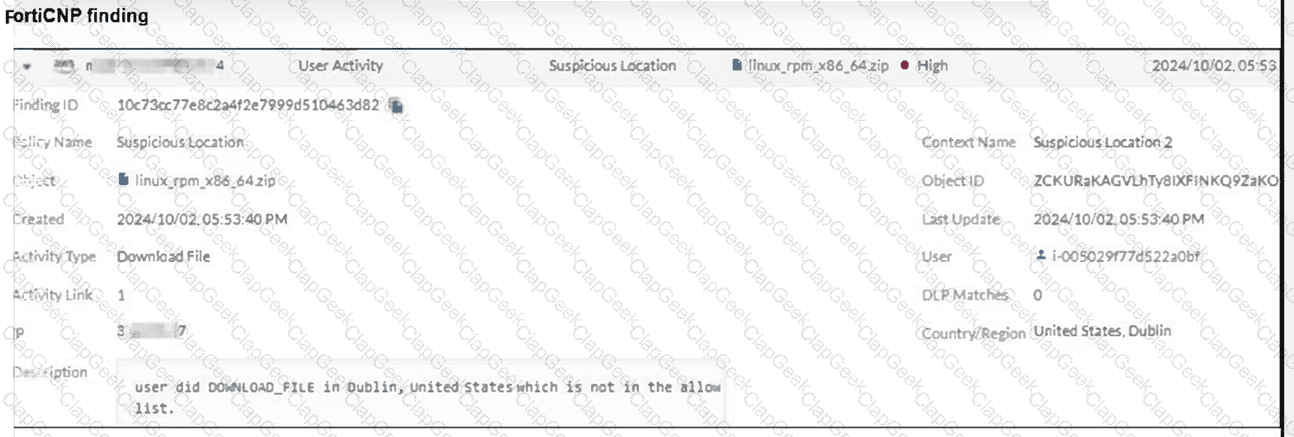
Refer to the exhibit.

Which FortiCNP policy type generated the finding shown in the exhibit? (Choose one answer)

Options:

A.

This finding was generated by a data scan policy.

B.

This finding was generated by a threat detection policy.

C.

This finding was generated by a risk management policy.

D.

This finding was generated by a file collection policy.

Buy Now
Questions 7

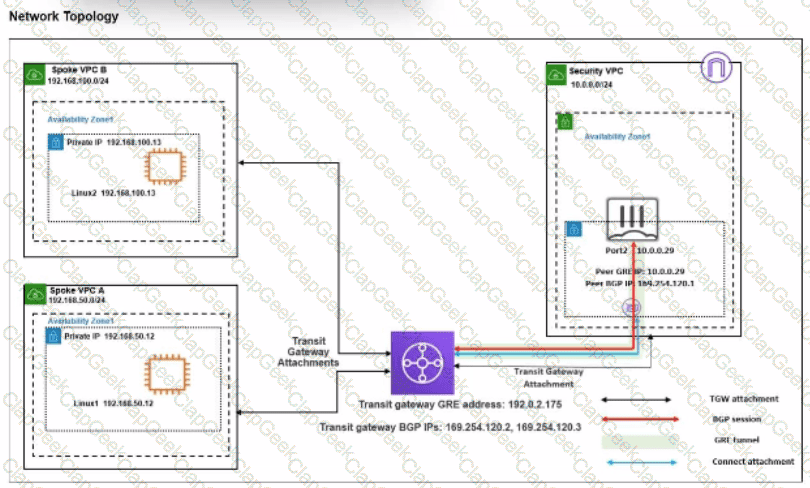
Refer to the exhibit.

You attempted to access the Linux1 EC2 instance directly from the internet using its public IP address in AWS. However, your connection is not successful.

Given the network topology, what can be the issue?

Options:

A.

There is no connection between VPC A and VPC B.

B.

There is no internet gateway attached to the Spoke VPC A.

C.

The Transit Gateway BGP IP address is incorrect.

D.

There is no elastic IP address attached to FortiGate in the Security VPC.

Buy Now
Questions 8

Refer to the exhibit.

You deployed a FortiGate HA active-passive cluster in Microsoft Azure.

Which two statements regarding this particular deployment are true? (Choose two.)

Options:

A.

You can use the vdom-exception command to synchronize the configuration.

B.

During a failover, all existing sessions are transferred to the new active FortiGate.

C.

The configuration does not synchronize between the primary and secondary devices.

D.

There is no SLA for API calls from Microsoft Azure.

Buy Now
Questions 9

Refer to the exhibit.

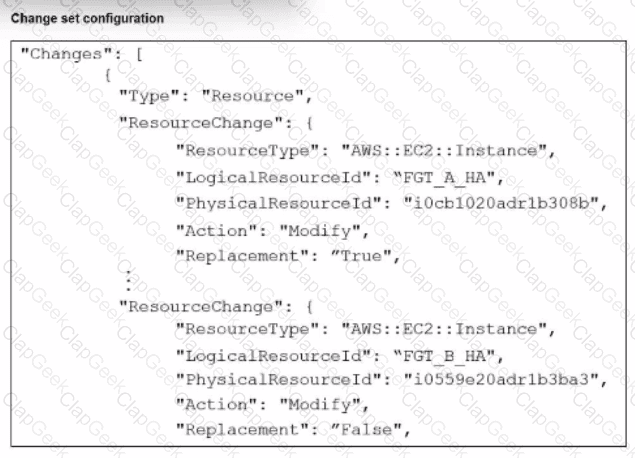
You are managing an active-passive FortiGate HA cluster in AWS that was deployed using CloudFormation. You have created a change set to examine the effects of some proposed changes to the current infrastructure. The exhibit shows some sections of the change set.

What will happen if you apply these changes?

Options:

A.

This deployment can be done without any traffic interruption.

B.

Both FortiGate VMs will get a new PhysicalResourceId.

C.

The updated FortiGate VMs will not have the latest configuration changes.

D.

CloudFormation checks if you will surpass your account quota.

Buy Now
Questions 10

Your administrator instructed you to deploy an Azure vWAN solution to create a connection between the main company site and branch sites to the other company VNETs. What is the best connection solution available between your company headquarters, branch sites, and the Azure vWAN hub? (Choose one answer)

Options:

A.

An L2TP connection

B.

SSL VPN connections

C.

GRE tunnels

D.

ExpressRoute

Buy Now
Questions 11

The cloud administration team is reviewing an AWS deployment that was done using CloudFormation.

The deployment includes six FortiGate instances that required custom configuration changes after being deployed. The team notices that unwanted traffic is reaching some of the FortiGate instances because the template is missing a security group.

To resolve this issue, the team decides to update the JSON template with the missing security group and then apply the updated template directly, without using a change set.

What is the result of following this approach?

Options:

A.

If new FortiGate instances are deployed later they will include the updated changes.

B.

Some of the FortiGate instances may be deleted and replaced with new copies.

C.

The update is applied, and the security group is added to all instances without interruption.

D.

CloudFormation rejects the update and warns that a new full stack is required.

Buy Now
Questions 12

How can the FortiCNAPP SmartFix feature assist security teams in handling vulnerabilities and code security?

Options:

A.

SmartFix can directly apply fixes to supported code repositories using APIs.

B.

SmartFix can suggest automated remediation steps for identified misconfigurations and vulnerabilities.

C.

SmartFix can aggregate multiple alerts into a single, prioritized view to reduce alert fatigue.

D.

SmartFix can list all possible versions with their known security issues and recommend the closest version that is free of vulnerabilities.

Buy Now
Questions 13

Refer to the exhibit.

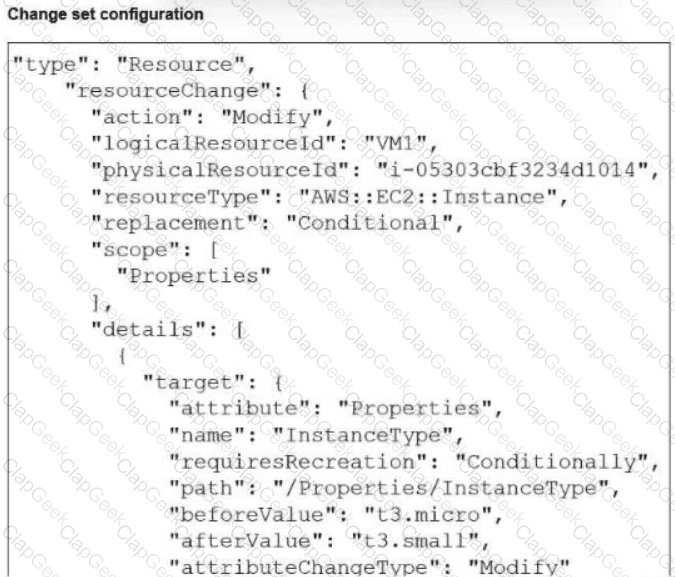
The exhibit shows partial output of changes that AWS found after you created a new change set.

What can you conclude from this output if you decide to execute this change set?

Options:

A.

Executing this change set will create a new VM, unless you do not have proper permissions.

B.

CloudFormation will check your account quota before executing the change set, to prevent errors.

C.

You should refer to the AWS documentation to prevent unplanned service interruptions.

D.

Resources deployed successfully will remain, even if other resources fail during execution.

Buy Now
Questions 14

Refer to the exhibit.

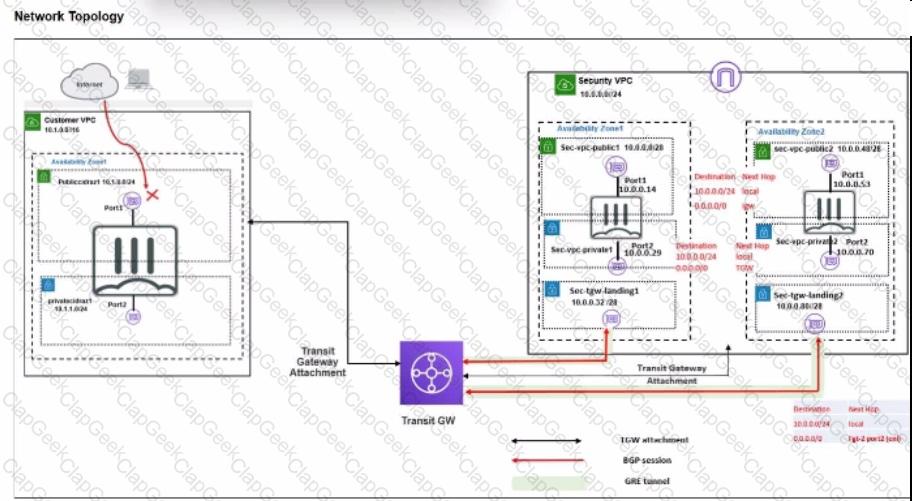
In your Amazon Web Services (AWS), you must allow inbound HTTPS access to the Customer VPC FortiGate VM from the internet. However, your HTTPS connection to the FortiGate VM in the Customer VPC is not successful.

Also, you must ensure that the Customer VPC FortiGate VM sends all the outbound Internet traffic through the Security VPC.

How do you correct this issue with minimal configuration changes? (Choose three.)

Options:

A.

Add a route with your local internet public IP address as the destination and the internet gateway as the target.

B.

Add a route with your local internet public IP address as the destination and the transit gateway as the target.

C.

Add a route to the destination 0.0.0.0/0 with the transit gateway as the target.

D.

Deploy an internet gateway, associate an EIP with the Customer VPC private subnet, and then add a new route with destination 0.0.0.0/0 with the internet gateway as the target.

E.

Deploy an internet gateway, attach it to the Customer VPC, and then associate an EIP with the port1 of the FortiGate in the Customer VPC.

Buy Now
Questions 15

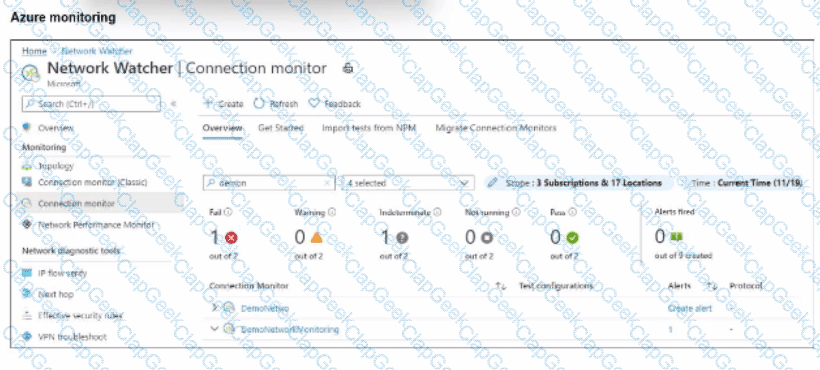
Refer to the exhibit.

After analyzing the native monitoring tools available in Azure, an administrator decides to use the tool displayed in the exhibit.

Why would an administrator choose this tool?

Options:

A.

To view details about Azure resources and their relationships across multiple regions.

B.

To obtain, and later examine, traffic flow data with a visualization tool.

C.

To help debug issues affecting virtual network gateways.

D.

To compare the latency of an on-premises site with the latency of an Azure application.

Buy Now
Questions 16

Refer to the exhibit.

Consider the active-active load balance sandwich scenario in Microsoft Azure.

What are two important facts in the active-active load balance sandwich scenario? (Choose two.)

Options:

A.

It is recommended to enable NAT on FortiGate policies.

B.

It uses the FGCP protocol for session synchronization by default.

C.

It uses the vdom-exception command to exclude the configuration from being synchronized by default.

D.

It supports session synchronization for handling asymmetric traffic.

Buy Now
Questions 17

Refer to the exhibit.

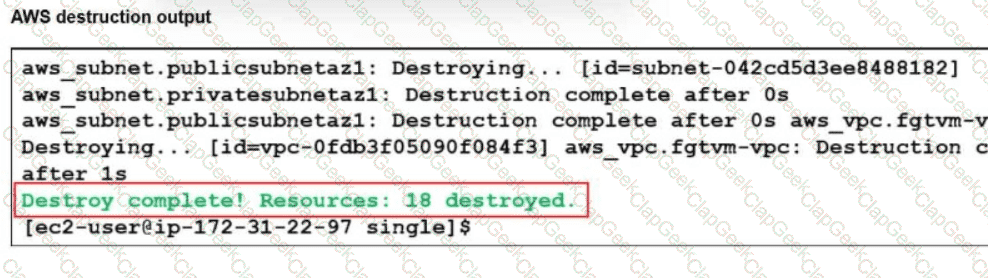
An administrator deployed a FortiGate-VM in a high availability (HA) (active/passive) architecture in Amazon Web Services (AWS) using Terraform for testing purposes. At the same time, the administrator deployed a single Linux server using AWS Marketplace.

Which two options are available for the administrator to delete all the resources created in this test? (Choose two.)

Options:

A.

The administrator must manually delete the Linux server.

B.

Use the terraform destroy all command.

C.

Use the terraform destroy command.

D.

Use the terraform validate command.

Buy Now
Questions 18

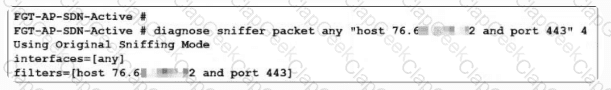
Refer to the exhibit.

An administrator has deployed a FortiGate VM in Amazon Web Services (AWS) and is trying to access it using its public IP address from their local computer. However, the connection is not successful, and at the same time FortiGate is not receiving any HTTPS or SSH traffic on its external interface.

What should the administrator check for a possible issue?

Options:

A.

Check the FortiGate instance ID.

B.

Check the FortiGate firewall policies.

C.

Check the debug flow for any network ACLs.

D.

Check the inbound rules of the security groups.

Buy Now
Questions 19

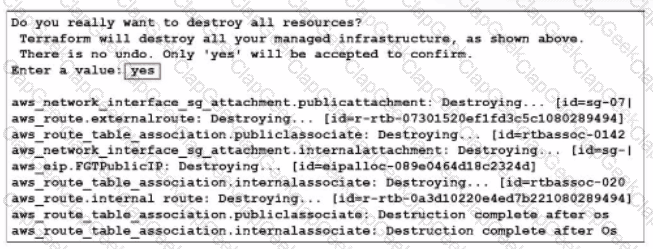
What would be the impact of confirming to delete all the resources in Terraform?
Options:

A.

It destroys all the resources tied to the AWS Identity and Access Management (IAM) user.

B.

It destroys all the resources in the resource group.

C.

It destroys all the resources in the .tfstate file.

D.

It destroys all the resources in the .tfvars file.

Buy Now
Questions 20

An administrator decides to use the Use managed identity option on the FortiGate SDN connector with Microsoft Azure. However, the SDN connector is failing on the connection.

What must the administrator do to correct this issue?
Options:

A.

Make sure to add the Client secret on FortiGate side of the configuration.

B.

Make sure to add the Tenant ID on FortiGate side of the configuration.

C.

Make sure to enable the system assigned managed identity on Azure.

D.

Make sure to set the type to system managed identity on FortiGate SDN connector settings.

Buy Now
Exam Code: NSE7_CDS_AR-7.6
Exam Name: Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect
Last Update: Oct 4, 2026
Questions: 67
NSE7_CDS_AR-7.6 pdf

NSE7_CDS_AR-7.6 PDF

$21.25  $84.99
NSE7_CDS_AR-7.6 Engine

NSE7_CDS_AR-7.6 Testing Engine

$25  $99.99
NSE7_CDS_AR-7.6 PDF + Engine

NSE7_CDS_AR-7.6 PDF + Testing Engine

$33.75  $134.99