Black Friday Early Access - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save75geek

GH-200 GitHub Actions Exam Questions and Answers

Questions 4

As a developer, you are authoring a workflow that will deploy to both DevCloud and TestCloud resources. Each cloud resource is accessed with a different deployment key. Which approach best allows you to use the same reusable workflow in separate jobs to target the different cloud resources?

Options:

A.

Create repository secrets named DevCloud.DEPLOY_KEY and TestCloud.DEPLOY_KEY so that the reusable workflow parses the secrets by resource name.

B.

Store the different keys in a DEPLOY_KEY environment secret in the DevCloud and TestCloud environments. Specify DEPLOY_KEY in the secrets section of the reusable workflow.

C.

Use a marketplace action to conditionally parse the DEPLOY_KEY repository secret based on the cloud resource name.

D.

Populate a DEPLOY_KEY repository secret with a JSON object containing DevCloud and TestCloud properties. Then specify DEPLOY_KEY.DevCloud in the secrets sections of the reusable workflow.

Buy Now
Questions 5

Which statement accurately describes using labels to route GitHub Actions workflows to runners?

Options:

A.

A user can assign multiple labels to a self-hosted runner and use the labels in a runs-on to target only runners that match all the specified labels.

B.

Labels apply only to GitHub-hosted runners and are ignored by self-hosted runners.

C.

GitHub Actions automatically assigns the runner’s IP address as a label, and the label must be used in a runs-on.

D.

To target a specific runner, the runs-on must match the runner’s hostname rather than its labels.

Buy Now
Questions 6

Which default GitHub environment variable indicates the owner and repository name?

Options:

A.

REPOSITORY NAME

B.

GITHUB REPOSITORY

C.

ENV REPOSITORY

D.

GITHUB WORKFLOW REPO

Buy Now
Questions 7

How can a workflow deployment mitigate the risk of multiple workflow runs deploying to a single cloud environment simultaneously?

(Each correct answer presents part of the solution. Choose two.)

Options:

A.

Pass the mutex into the deployment job.

B.

Configure the mutex setting in the environment.

C.

Specify a concurrency scope in the workflow.

D.

Specify a target environment in the deployment job.

E.

Set the concurrency in the deployment job to 1.

F.

Reference the mutex in the task performing the deployment.

Buy Now
Questions 8

When reviewing an action for use, what file defines its available inputs and outputs?

Options:

A.

inputs.yml

B.

config.json

C.

defaults.json

D.

workflow.yml

E.

action.yml

Buy Now
Questions 9

An organization ' s policies specify that only local actions are allowed. How should actions be distributed for this organization?

Options:

A.

Via the GitHub Marketplace

B.

Via the .github repository owned by the organization

C.

Via a repository owned by a third party

D.

Via repositories owned by the organization

Buy Now
Questions 10

In which scenarios could the GITHUB_TOKEN be used? (Choose two.)

Options:

A.

to leverage a self-hosted runner

B.

to create a repository secret

C.

to publish to GitHub Packages

D.

to create issues in the repo

E.

to read from the file system on the runner

F.

to add a member to an organization

Buy Now
Questions 11

As a developer, you need to use GitHub Actions to deploy a microservice that requires runtime access to a secure token. This token is used by a variety of other microservices managed by different teams in different repos. To minimize management overhead and ensure the token is secure, which mechanisms should you use to store and access the token? (Choose two.)

Options:

A.

Store the token in a configuration file in a private repository. Use GitHub Actions to deploy the configuration file to the runtime environment.

B.

Store the token as a GitHub encrypted secret in the same repo as the code. Create a reusable custom GitHub Action to access the token by the microservice at runtime.

C.

Use a corporate non-GitHub secret store (e.g., HashiCorp Vault) to store the token. During deployment, use GitHub Actions to store the secret in an environment variable that can be accessed at runtime.

D.

Store the token as a GitHub encrypted secret in the same repo as the code. During deployment, use GitHub Actions to store the secret in an environment variable that can be accessed at runtime.

E.

Store the token as an organizational-level encrypted secret in GitHub. During deployment, use GitHub Actions to store the secret in an environment variable that can be accessed at runtime.

Buy Now
Questions 12

Which of the following is the best way for an enterprise to prevent certain marketplace actions from running?

Options:

A.

Create a list of the actions that are restricted from being used as an enterprise policy. Every other action can be run.

B.

It is not possible; if an action is in the marketplace, its use cannot be restricted.

C.

Create a list that is maintained as a . yml file in a . github repository specified in the enterprise. Only these actions can be run.

D.

Create a list of the actions that are allowed to run as an enterprise policy. Only these actions can be run.

Buy Now
Questions 13

Which syntax correctly accesses a job output (output1) of an upstream job (job1) from a dependent job within a workflow?

Options:

A.

${{needs.job1.outputs.output1}}

B.

${{needs.job1.output1}}

C.

${{depends.job1.output1}}

D.

${{job1.outputs.output1}}

Buy Now
Questions 14

Your organization is managing secrets using GitHub encrypted secrets, including a secret named SuperSecret. As a developer, you need to create a version of that secret that contains a different value for use in a workflow that is scoped to a specific repository named MyRepo. How should you store the secret to access your specific version within your workflow?

Options:

A.

Create a duplicate entry for SuperSecret in the encrypted secret store and specify MyRepo as the scope.

B.

Create MyRepo_SuperSecret in GitHub encrypted secrets to specify the scope to MyRepo.

C.

Create a file with the SuperSecret. information in the .qithub/secrets folder in MyRepo.

D.

Create and access SuperSecret from the secrets store in MyRepo.

Buy Now
Questions 15

As a developer, how can you identify a composite action on GitHub?

Options:

A.

The action’s repository includes Dockerfile and package.json files.

B.

The action.yml metadata file has the runs.using value set to composite.

C.

The action’s repository name includes the keyword “composite.”

D.

The action’s repository includes an init.sh file in the root directory.

Buy Now
Questions 16

As a DevOps engineer, you need to execute a deployment to different environments like development and testing based on the labels added to a pull request. The deployment should use the releases branch and trigger only when there is a change in the files under apps folder. Which code block should be used to define the deployment workflow trigger?

Options:

A.

on:pull_request_label:branches:- ' releases ' paths:- ' apps/** '

B.

on:pull_request_review:types: [labeled]branches:- ' releases ' paths:- ' apps/** '

C.

on:pull_request:types: [labeled]branches:- ' releases/** ' paths:- ' apps '

D.

on:pull_request:types: [labeled]branches:- ' releases ' paths:- ' apps/** '

Buy Now
Questions 17

What are two reasons to keep an action in its own repository instead of bundling it with other application code? Each correct answer presents a complete solution.

NOTE: Each correct answer is worth one point.

Options:

A.

It allows sharing workflow secrets with other users.

B.

It widens the scope of the code base for developers fixing issues and extending the action.

C.

It makes the action.yml file optional.

D.

It makes it easier for the GitHub community to discover the action.

E.

It decouples the action ' s versioning from the versioning of other application code.

Buy Now
Questions 18

As a developer, how can you identify a JavaScript action on GitHub?

Options:

A.

The action.yml metadata file references a package.json file.

B.

The action ' s repository includes a js.yml file in the .github/workflows directory.

C.

The action’s repository name includes the keyword “JavaScript.”

D.

The action.yml metadata file has the runs.using value set to node16.

Buy Now
Questions 19

What metadata file in a custom action defines the main entry point?

Options:

A.

action.js

B.

index.js

C.

action.yml

D.

main.yml

Buy Now
Questions 20

As a DevOps engineer, you need to define a deployment workflow that runs after the build workflow has successfully completed. Without modifying the build workflow, which trigger should you define in the deployment workflow?

Options:

A.

repository_dispatch

B.

workflow_run

C.

workflow_exec

D.

workflow_dispatch

Buy Now
Questions 21

As a developer, your Actions workflow often reuses the same outputs or downloaded dependencies from one run to another. To cache dependencies for a job, you are using the GitHub cache action. Which input parameters are required for this action? (Choose two.)

Options:

A.

dependency: the name and version of a package to cache or restore

B.

key: the key created when saving a cache and the key used to search for a cache

C.

cache-hit: the copy action key used with restore parameter to restore the data from the cache

D.

path: the file path on the runner to cache or restore

E.

ref: the ref name of the branch to access and restore a cache created

F.

restore-keys: the copy action key used with cache parameter to cache the data

Buy Now
Questions 22

Which default environment variable specifies the branch or tag that triggered a workflow?

Options:

A.

GITHUB_TAG

B.

GITHUB_REF

C.

ENV_BRANCH

D.

GITHUB_BRANCH

Buy Now
Questions 23

As a developer, you need to integrate a GitHub Actions workflow with a third-party code quality provider that uses the Checks API. How should you trigger a follow-up workflow?

Options:

A.

Add the workflow_run webhook event as a trigger for the workflow for the code quality integration name

B.

Add the check_run webhook event as a trigger for the workflow when the code quality integration is completed

C.

Add the pull_request webhook event as a trigger for the workflow when the code quality integration is synchronized

D.

Add the deployment webhook event as a trigger for the workflow when the code quality integration is completed

Buy Now
Questions 24

You have a GitHub Enterprise Cloud Organization that contains private repositories for three apps. The workflow of each app has a job that uses repository secrets and calls a shared deployment action.

You plan to replace separate deployment scripts with a single custom action.

You need to recommend a distribution and versioning approach for the custom action. The solution must meet the following requirements:

    The action repository must be private.

    Only specific application repositories can use the action.

    The workflow reference must be resistant to changes in the action repository without requiring a workflow file change.

What should you recommend?

Options:

A.

Store the custom action in a public repository.

Publish the action to GitHub Marketplace.

Reference the action by using a full-length commit SHA.

B.

Store the custom action in a private repository.

Enable all the repositories in the organization to access the action.

Reference the action by using a full-length commit SHA.

C.

Store the custom action in a private repository.

Enable only selected repositories in the organization to access the action.

Reference the action by using a full-length commit SHA.

D.

Store the custom action in a private repository.

Enable only selected repositories in the organization to access the action.

Reference the action by using a semantic version tag.

Buy Now
Questions 25

You have exactly one Windows x64 self-hosted runner, and it is configured with custom tools. Which syntax could you use in the workflow to target that runner?

Options:

A.

self-hosted: [windows-x64]

B.

runs-on: [self-hosted, windows, x64]

C.

runs-on: windows-latest

D.

self-hosted: [windows, x64]

Buy Now
Questions 26

As a developer, you want to review the step that caused a workflow failure and the failed step ' s build logs. First navigate to the main page of the repository on GitHub. Which section contains the step failure information?

Options:

A.

Insights

B.

Code

C.

Actions

D.

Pull requests

E.

Issues

Buy Now
Questions 27

You need to use a specific version of an action. How should you use v1 of an actions/javascript-action repository in your workflow?

Options:

A.

steps:uses: actions/javascript-action/v1

B.

steps:uses: actions/javascript-actionversion: v1

C.

steps:uses: actions/javascript-action-v1

D.

steps:uses: actions/javascript-action@v1

Buy Now
Questions 28

Custom environment variables can be defined at multiple levels within a workflow file, including which three levels?

(Each correct answer presents a complete solution. Choose three.)

Options:

A.

Stage level

B.

Default level

C.

Step level

D.

Runner level

E.

Top level

F.

Job level

Buy Now
Questions 29

Your organization has a secret that must be available to all the repositories within GitHub Actions workflows.

You need to store the secret. The solution must minimize administrative effort.

What should you do in GitHub?

Options:

A.

For each GitHub repository, select Settings > Secrets and variables > Actions, and then add the secret.

B.

From your personal GitHub profile, select Settings > Developer settings > Secrets, and then add the secret.

C.

From the organization ' s page, select Settings > Security > Secrets, and then add the secret.

D.

From the organization ' s page, select Settings > Secrets and variables > Actions, and then add the secret.

Buy Now
Questions 30

What are the two types of environment protection rules you can configure? (Choose two.)

Options:

A.

required reviewers

B.

branch protections

C.

wait timer

D.

artifact storage

Buy Now
Questions 31

You need to make a script to retrieve workflow run logs by using the API. Which is the correct API endpoint to download a workflow run log?

Options:

A.

GET /repos/{owner}/{repo}/actions/runs/{run_id}/logs

B.

POST /repos/{owner}/{repo}/actions/runs/{run_id}/logs

C.

GET /repos/{owner}/{repo}/actions/artifacts/logs

D.

POST /repos/{owner}/{repo}/actions/runs/{run_id}

Buy Now
Questions 32

Which statement is true regarding the ability to delete a workflow run?

Options:

A.

Completed workflow runs may be deleted.

B.

Pending workflow runs may be deleted.

C.

Workflow runs must be older than 30 days to be deleted.

D.

Admin access is required to delete a workflow run.

Buy Now
Questions 33

Which workflow event is used to manually trigger a workflow run?

Options:

A.

create

B.

workflow_dispatch

C.

workflow_run

D.

status

Buy Now
Questions 34

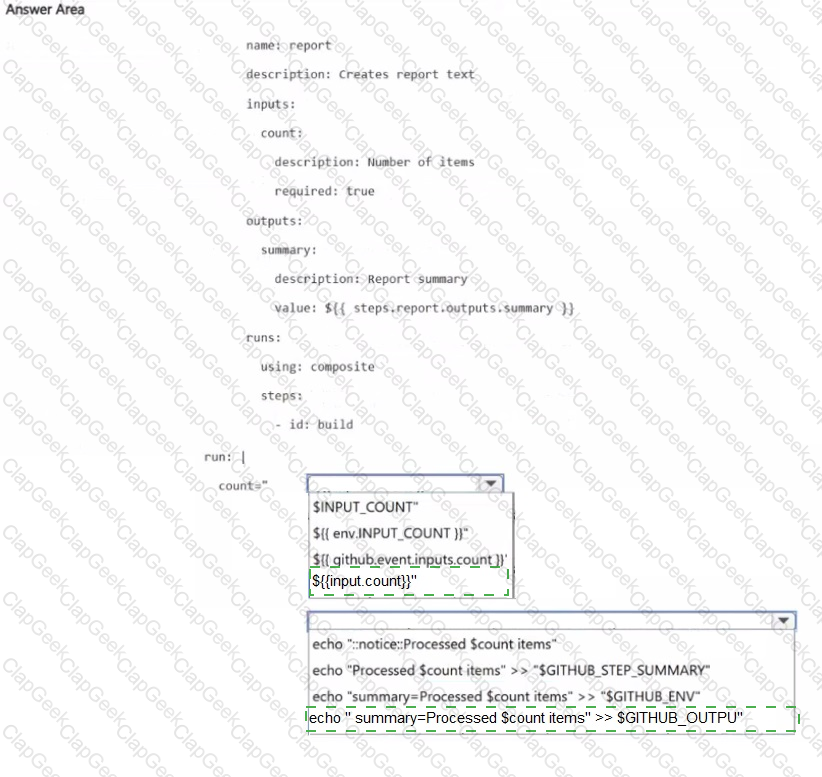
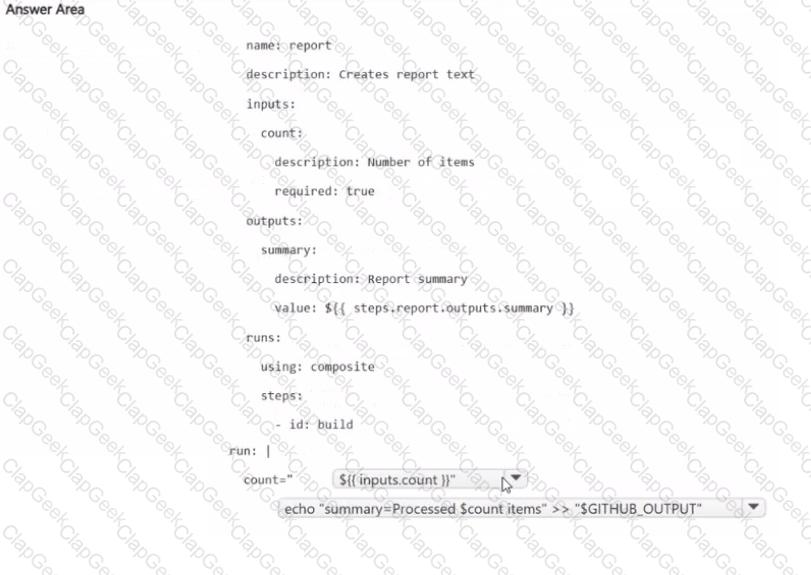
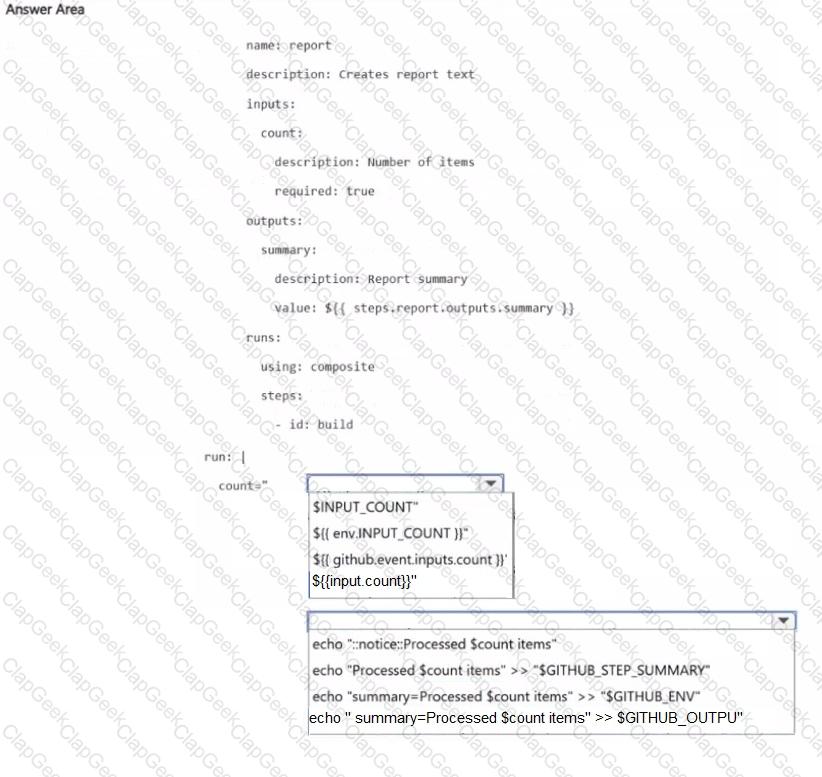
You have a GitHub repository that contains a composite action named Action1 and a workflow named Workflow1. Workflow1 contains the following steps:

• Calls Action1 in a step named report

• Passes count: ' 5 ' by using with

• Reads ${{ steps.report.outputs.summary )}

Action1 completes successfully, but the last step receives an empty value for summary.

You need to ensure that Action1 consumes the input of Workflow1 and exposes the expected output.

How should you complete the metadata file? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.
Options:

Buy Now
Questions 35

As a developer, one of your workflows requires Xcode version 11.2 hosted on macOS Catalina (version 10.15). You have already created and configured a self-hosted runner to conform to those requirements and registered it with your organization. What else should you do to ensure that the workflow accesses the correct runner instance?

(Each correct answer presents part of the solution. Choose three.)

Options:

A.

Create runner groups named macos-10.15 and xcode-11.2.

B.

In the workflow, specify:runs-on: [${{ groups.macos-10.15 }}, ${{ groups.xcode-11.2 }}]

C.

Assign the custom labels to the self-hosted runner.

D.

Create custom runner labels for macos-10.15 and xcode-11.2.

E.

Add your runner to the appropriate runner groups.

F.

In the workflow, specify:runs-on: [self-hosted, macos-10.15, xcode-11.2]

Buy Now
Questions 36

Which action type should be used to bundle a series of run steps into a reusable custom action?

Options:

A.

Composite action

B.

Bash script action

C.

Docker container action

D.

JavaScript action

Buy Now
Questions 37

How should you install the bats NPM package in your workflow?

A)

B)

C)

D)

Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Buy Now
Questions 38

You are a developer, and your container jobs are failing on a self-hosted runner. Which requirements must you check to ensure that the self-hosted runner is properly configured? (Choose two.)

Options:

A.

The self-hosted runner is running a Linux operating system.

B.

The self-hosted runner is running a Windows operating system.

C.

Docker is installed on the self-hosted runner.

D.

Kubernetes is installed on the self-hosted runner.

E.

The service status of Kubernetes is " active " .

Buy Now
Questions 39

Which of the following commands will set the $FOO environment variable within a script, so that it may be used in subsequent workflow job steps?

Options:

A.

run: echo " ::set-env name=FOO::bar "

B.

run: echo " FOO=bar " > > $GITHUB_ENV

C.

run: echo ${{ $FOO=bar }}

D.

run: export FOO=bar

Buy Now
Questions 40

GitHub-hosted runners support which capabilities? (Choose two.)

Options:

A.

automatic patching of both the runner and the underlying OS

B.

automatic file-system caching between workflow runs

C.

support for Linux, Windows, and mac

D.

support for a variety of Linux variations including CentOS, Fedora, and Debian

E.

requiring a payment mechanism (e.g., credit card) to use for private repositories

Buy Now
Questions 41

As a developer, you need to create a custom action written in Python. Which action type should you choose?

As a developer, you need to create a custom action written in Python. Which action type should you choose?

Options:

A.

JavaScript action

B.

composite run step

C.

Python action

D.

Docker container action

Buy Now
Questions 42

What is the smallest scope for an environment variable?

Options:

A.

the workflow settings

B.

a step

C.

a job

D.

the workflow env mapping

Buy Now
Questions 43

As a developer, you need to add the correct syntax to allow the following workflow file to be triggered by multiple types of events.

Which two code blocks should you add starting at line 5? Each correct answer presents a complete solution.

NOTE: Each correct answer is worth one point.

4 name: Node CI/CD

5

6

7

8 jobs:

9 build:

10 runs-on:

11 steps:

12 - uses: actions/checkout@v2

13 - uses: actions/setup-node@v1

14 with:

15 node-version: 12

16 - run: npm ci

17 - run: npm test

18

Options:

A.

on:env:- ' prod ' - ' qa ' - ' test '

B.

on: [push, commit]

C.

on: [push, pull_request]

D.

on:branches:- ' main ' - ' dev '

E.

on:push:branches:- mainrelease:types:- created

F.

on:schedule:- cron: ' */15 * * * * ' initiate:- ' main '

Buy Now
Questions 44

In which of the following scenarios should you use self-hosted runners? Each correct answer presents a complete solution.

NOTE: Each correct answer is worth one point.
Options:

A.

when the workflow jobs must be run on Windows 10

B.

when jobs must run for longer than 6 hours

C.

when you want to use macOS runners

D.

when GitHub Actions minutes must be used for the workflow runs

E.

when a workflow job needs to install software from the local network

Buy Now
Questions 45

Which run: command will set a step ' s output?

Options:

A.

run: echo " MY_OUTPUT=foo " > > $GITHUB_OUTPUT

B.

run: export MY_OUTPUT=foo

C.

run: echo ${{ $GITHUB_OUTPUT=foo }}

D.

run: echo " ::set-env name=MY OUTPUT::foo "

Buy Now
Exam Code: GH-200
Exam Name: GitHub Actions Exam
Last Update: Nov 15, 2026
Questions: 150
GH-200 pdf

GH-200 PDF

$23.75  $94.99
GH-200 Engine

GH-200 Testing Engine

$27.5  $109.99
GH-200 PDF + Engine

GH-200 PDF + Testing Engine

$36.25  $144.99