Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save75geek

350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Questions and Answers

Questions 4

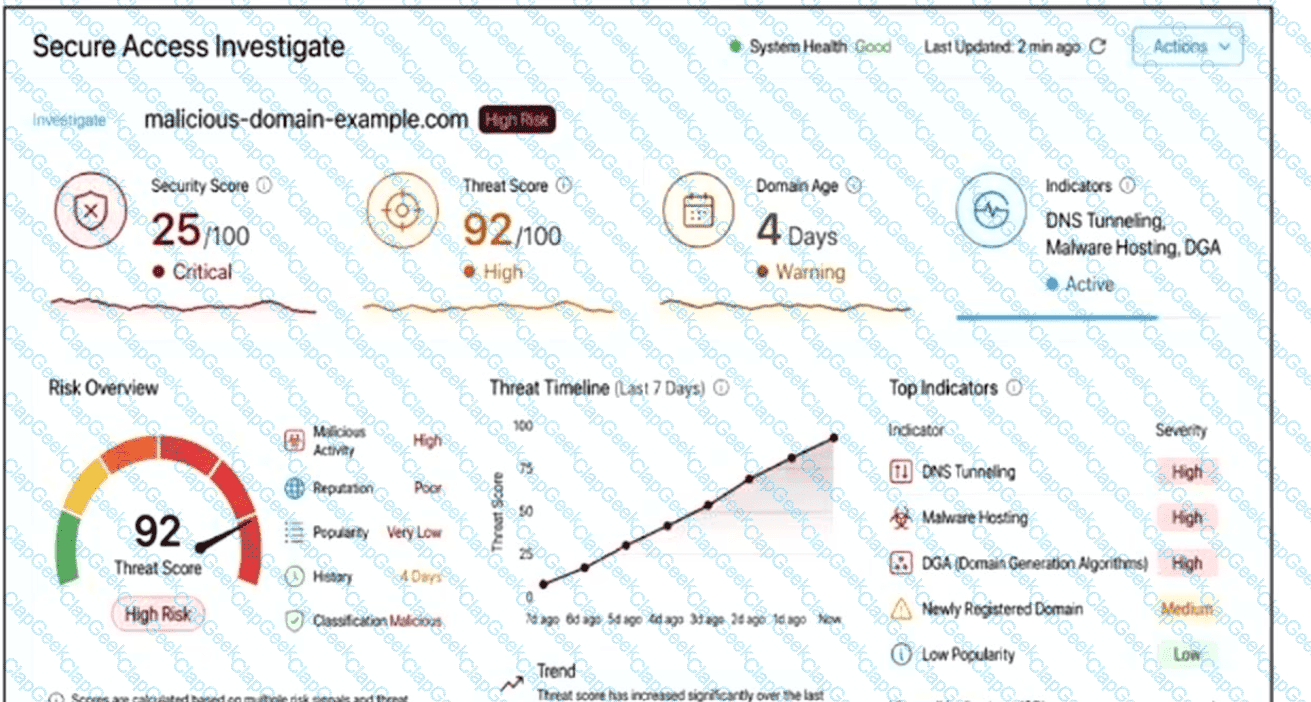
Refer to the exhibit.

What conclusion should an administrator draw about the URL malicious-domain-example.com?

Options:

A.

The domain is blocked solely because it is newly registered, regardless of the Threat Score.

B.

The domain is a legacy site that has been compromised, as indicated by its domain age.

C.

The domain is safe because its Security Score is 25/100.

D.

The high Threat Score together with DNS tunneling, malware hosting, and DGA indicators shows active malicious behavior.

Buy Now
Questions 5

An administrator is trying to determine which applications are being used in the network but does not want the

network devices to send metadata to Cisco Firepower. Which feature should be used to accomplish this?

Options:

A.

NetFlow

B.

Packet Tracer

C.

Network Discovery

D.

Access Control

Buy Now
Questions 6

What are two rootkit types? (Choose two)

Options:

A.

registry

B.

virtual

C.

bootloader

D.

user mode

E.

buffer mode

Buy Now
Questions 7

Which term describes when the Cisco Secure Firewall downloads threat intelligence updates from Cisco Tables?

Options:

A.

analysis

B.

sharing

C.

authoring

D.

consumption

Buy Now
Questions 8

Which PKI enrollment method allows the user to separate authentication and enrollment actions and also

provides an option to specify HTTP/TFTP commands to perform file retrieval from the server?

Options:

A.

url

B.

terminal

C.

profile

D.

selfsigned

Buy Now
Questions 9

Which Cisco platform ensures that machines that connect to organizational networks have the recommended

antivirus definitions and patches to help prevent an organizational malware outbreak?

Options:

A.

Cisco WiSM

B.

Cisco ESA

C.

Cisco ISE

D.

Cisco Prime Infrastructure

Buy Now
Questions 10

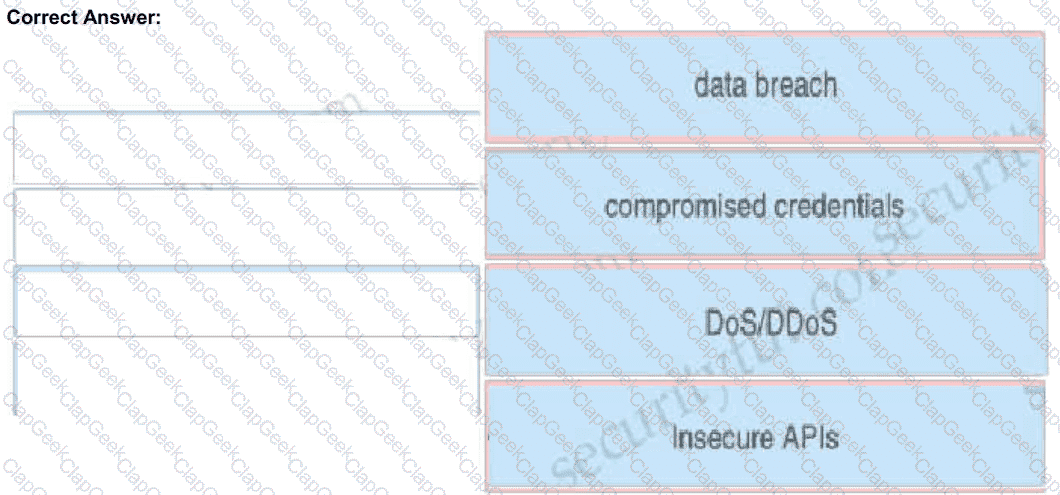
Drag and drop the threats from the left onto examples of that threat on the right
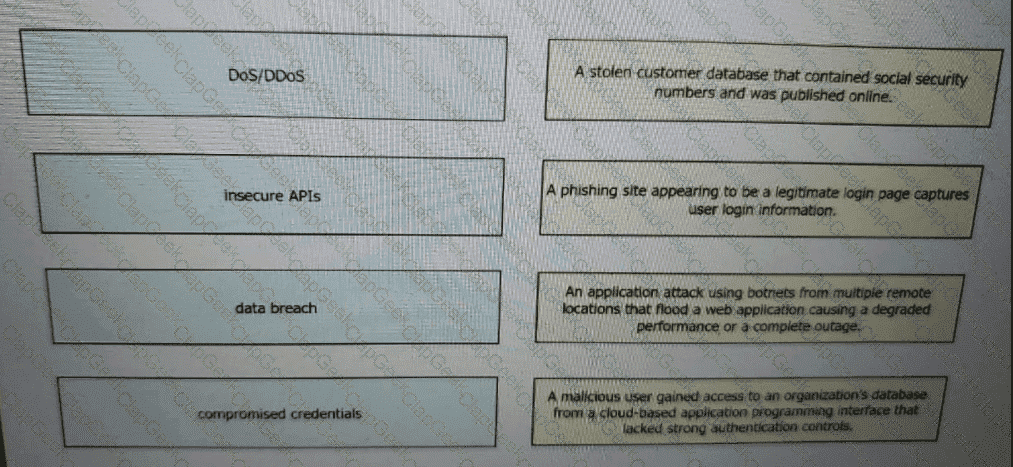
Options:

Buy Now
Questions 11

An email administrator is setting up a new Cisco ESA. The administrator wants to enable the blocking of greymail for the end user. Which feature must the administrator enable first?

Options:

A.

File Analysis

B.

IP Reputation Filtering

C.

Intelligent Multi-Scan

D.

Anti-Virus Filtering

Buy Now
Questions 12

Which protocol provides the strongest throughput performance when using Cisco AnyConnect VPN?

Options:

A.

TLSv1.2

B.

TLSv1.1

C.

BJTLSv1

D.

DTLSv1

Buy Now
Questions 13

Which characteristic is unique to a Cisco WSAv as compared to a physical appliance?

Options:

A.

supports VMware vMotion on VMware ESXi

B.

requires an additional license

C.

performs transparent redirection

D.

supports SSL decryption

Buy Now
Questions 14

What are the components of endpoint protection against social engineering attacks?

Options:

A.

IPsec

B.

IDS

C.

Firewall

D.

Cisco Secure Email Gateway

Buy Now
Questions 15

Which two functions does the Cisco Advanced Phishing Protection solution perform in trying to protect from phishing attacks? (Choose two.)

Options:

A.

blocks malicious websites and adds them to a block list

B.

does a real-time user web browsing behavior analysis

C.

provides a defense for on-premises email deployments

D.

uses a static algorithm to determine malicious

E.

determines if the email messages are malicious

Buy Now
Questions 16

What is a benefit of a Cisco Secure Email Gateway Virtual as compared to a physical Secure Email Gateway?
Options:

A.

simplifies the distribution of software updates

B.

provides faster performance

C.

provides an automated setup process

D.

enables the allocation of additional resources

Buy Now
Questions 17

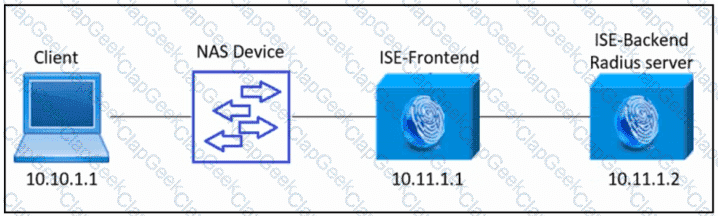
Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.

Which Cisco ISE configuration must be used?

Options:

A.

Set 10.11.1.2 as a network device in ISE-Frontend. Set port 1700/2083 for RADIUS authentication.

B.

Set 10.11.1.1 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

C.

Set 10.11.1.2 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

D.

Set 10.11.1.1 as a network device in ISE-Frontend. Set ports 1700/2083 for RADIUS authentication.

Buy Now
Questions 18

A customer has various external HTTP resources available including Intranet Extranet and Internet, with a

proxy configuration running in explicit mode. Which method allows the client desktop browsers to be configured

to select when to connect direct or when to use the proxy?

Options:

A.

Transport mode

B.

Forward file

C.

PAC file

D.

Bridge mode

Buy Now
Questions 19

On which part of the IT environment does DevSecOps focus?

Options:

A.

application development

B.

wireless network

C.

data center

D.

perimeter network

Buy Now
Questions 20

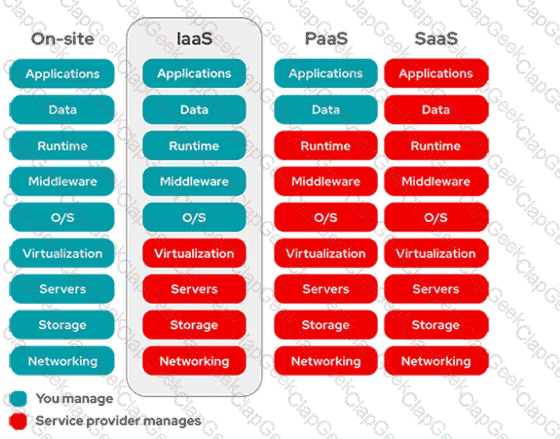
In which cloud services model is the tenant responsible for virtual machine OS patching?

Options:

A.

IaaS

B.

UCaaS

C.

PaaS

D.

SaaS

Buy Now
Questions 21

Which VPN provides scalability for organizations with many remote sites?

Options:

A.

DMVPN

B.

site-to-site iPsec

C.

SSL VPN

D.

GRE over IPsec

Buy Now
Questions 22

What is the purpose of the Cisco Endpoint loC feature?

Options:

A.

It provides stealth threat prevention.

B.

lt is a signature-based engine.

C.

lt is an incident response tool

D.

It provides precompromise detection.

Buy Now
Questions 23

What is a difference between FlexVPN and DMVPN?

Options:

A.

DMVPN uses IKEv1 or IKEv2, FlexVPN only uses IKEv1

B.

DMVPN uses only IKEv1 FlexVPN uses only IKEv2

C.

FlexVPN uses IKEv2, DMVPN uses IKEv1 or IKEv2

D.

FlexVPN uses IKEv1 or IKEv2, DMVPN uses only IKEv2

Buy Now
Questions 24

What is a difference between a zone-based firewall and a Cisco Adaptive Security Appliance firewall?

Options:

A.

Zone-based firewalls provide static routing based on interfaces, and Cisco Adaptive Security Appliance firewalls provide dynamic routing.

B.

Zone-based firewalls support virtual tunnel interfaces across different locations, and Cisco Adaptive Security Appliance firewalls support DMVPN.

C.

Zone-based firewalls have a default allow-all policy between interfaces in the same zone, and Cisco Adaptive Security Appliance firewalls have a deny-all policy.

D.

Zone-based firewalls are used in large deployments with multiple areas, and Cisco Adaptive Security Appliance firewalls are used in small deployments.

Buy Now
Questions 25

An engineer is configuring guest WLAN access using Cisco ISE and the Cisco WLC. Which action temporarily gives guest endpoints access dynamically while maintaining visibility into who or what is connecting?

Options:

A.

Modify the WLC configuration to require local WLC logins for the authentication prompts.

B.

Configure ISE and the WLC for guest redirection and services using a self-registered portal.

C.

Configure ISE and the WLC for guest redirection and services using a hotspot portal.

D.

Modify the WLC configuration to allow any endpoint to access an internet-only VLAN.

Buy Now
Questions 26

Which type of data does the Cisco Stealthwatch system collect and analyze from routers, switches, and firewalls?

Options:

A.

NTP

B.

syslog

C.

SNMP

D.

NetFlow

Buy Now
Questions 27

An engineer must modify an existing remote access VPN using a Cisco AnyConnect Secure Mobility client solution and a Cisco Secure Firewall. Currently, all the traffic generate by the user Is sent to the VPN tunnel and the engineer must now exclude some servers and access them directly instead. Which element must be modified to achieve this goat?

Options:

A.

NAT exemption

B.

encryption domain

C.

routing table

D.

group policy

Buy Now
Questions 28

A customer has various external HTTP resources available including Intranet. Extranet, and Internet, with a proxy configuration running in explicit mode Which method allows the client desktop browsers to be configured to select when to connect direct or when to use the proxy?

Options:

A.

Transparent mode

B.

Forward file

C.

PAC file

D.

Bridge mode

Buy Now
Questions 29

Which two types of policies are used by ZTNA to provide access to an application? (Choose two.)

Options:

A.

Context

B.

Access

C.

Site-to-site

D.

Identity

E.

Remote access

Buy Now
Questions 30

Which Dos attack uses fragmented packets to crash a target machine?

Options:

A.

smurf

B.

MITM

C.

teardrop

D.

LAND

Buy Now
Questions 31

What is an advantage of the Cisco Umbrella roaming client?

Options:

A.

the ability to see all traffic without requiring TLS decryption

B.

visibility into IP-based threats by tunneling suspicious IP connections

C.

the ability to dynamically categorize traffic to previously uncategorized sites

D.

visibility into traffic that is destined to sites within the office environment

Buy Now
Questions 32

Which threat intelligence standard contains malware hashes?

Options:

A.

advanced persistent threat

B.

open command and control

C.

structured threat information expression

D.

trusted automated exchange of indicator information

Buy Now
Questions 33

What is a feature of NetFlow Secure Event Logging?

Options:

A.

It exports only records that indicate significant events in a flow.

B.

It filters NSEL events based on the traffic and event type through RSVP.

C.

It delivers data records to NSEL collectors through NetFlow over TCP only.

D.

It supports v5 and v8 templates.

Buy Now
Questions 34

Which Cisco solution extends network visibility, threat detection, and analytics to public cloud environments?

Options:

A.

Cisco Umbrella

B.

Cisco Stealthwatch Cloud

C.

Cisco Appdynamics

D.

Cisco CloudLock

Buy Now
Questions 35

Which Cisco solution does Cisco Umbrella integrate with to determine if a URL is malicious?

Options:

A.

AMP

B.

AnyConnect

C.

DynDNS

D.

Talos

Buy Now
Questions 36

An engineer configured a new network identity in Cisco Umbrella but must verify that traffic is being routed

through the Cisco Umbrella network. Which action tests the routing?

Options:

A.

Ensure that the client computers are pointing to the on-premises DNS servers.

B.

Enable the Intelligent Proxy to validate that traffic is being routed correctly.

C.

Add the public IP address that the client computers are behind to a Core Identity.

D.

Browse to http://welcome.umbrella.com/ to validate that the new identity is working.

Buy Now
Questions 37

Which feature requires that network telemetry be enabled?

Options:

A.

per-interface stats

B.

SNMP trap notification

C.

Layer 2 device discovery

D.

central syslog system

Buy Now
Questions 38

What is a commonality between DMVPN and FlexVPN technologies?

Options:

A.

FlexVPN and DMVPN use IS-IS routing protocol to communicate with spokes

B.

FlexVPN and DMVPN use the new key management protocol

C.

FlexVPN and DMVPN use the same hashing algorithms

D.

IOS routers run the same NHRP code for DMVPN and FlexVPN

Buy Now
Questions 39

An engineer has enabled LDAP accept queries on a listener. Malicious actors must be prevented from quickly

identifying all valid recipients. What must be done on the Cisco ESA to accomplish this goal?

Options:

A.

Configure incoming content filters

B.

Use Bounce Verification

C.

Configure Directory Harvest Attack Prevention

D.

Bypass LDAP access queries in the recipient access table

Buy Now
Questions 40

Which API method and required attribute are used to add a device into Cisco DNA Center with the native API?

Options:

A.

GET and serialNumber

B.

userSudiSerlalNos and deviceInfo

C.

POST and name

D.

lastSyncTime and pid

Buy Now
Questions 41

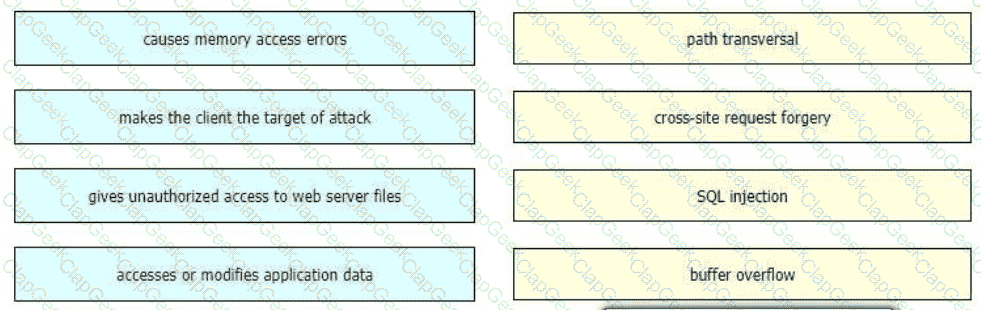
Drag and drop the exploits from the left onto the type of security vulnerability on the right.
Options:

Buy Now
Questions 42

Which two descriptions of AES encryption are true? (Choose two)

Options:

A.

AES is less secure than 3DES.

B.

AES is more secure than 3DES.

C.

AES can use a 168-bit key for encryption.

D.

AES can use a 256-bit key for encryption.

E.

AES encrypts and decrypts a key three times in sequence.

Buy Now
Questions 43

What is a difference between SQL injection and buffer overflow?

Options:

A.

SQL injection is delivered by a web form, and buffer overflow bypasses all forms of user authentication entirely.

B.

SQL injection gives unauthorized access to a database, and buffer overflow executes arbitrary code and corrupts memory.

C.

SQL injection causes denial-of-service, and buffer overflow bypasses all forms of user authentication.

D.

SQL injection is a stack-based attack, and buffer overflow is a heap-based attack.

Buy Now
Questions 44

Which two deployment model configurations are supported for Cisco FTDv in AWS? (Choose two)

Options:

A.

Cisco FTDv configured in routed mode and managed by an FMCv installed in AWS

B.

Cisco FTDv with one management interface and two traffic interfaces configured

C.

Cisco FTDv configured in routed mode and managed by a physical FMC appliance on premises

D.

Cisco FTDv with two management interfaces and one traffic interface configured

E.

Cisco FTDv configured in routed mode and IPv6 configured

Buy Now
Questions 45

Which Linux system call loads an eBPF program and manages eBPF maps within the kernel?

Options:

A.

perf_event_open()

B.

ioctl()

C.

prctl()

D.

bpf()

Buy Now
Questions 46

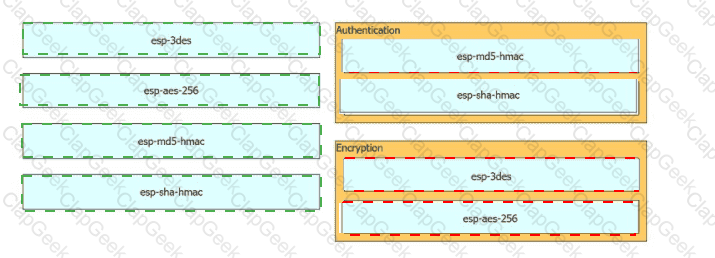
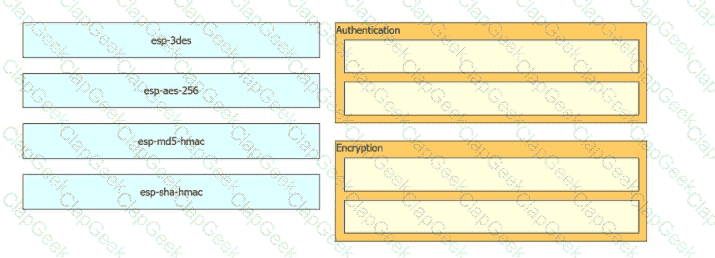
Drag and drop the cryptographic algorithms for IPsec from the left onto the cryptographic processes on the right.
Options:

Buy Now
Questions 47

A facilities team is onboarding a fleet of badge readers and IP cameras through MAB authentication on Cisco Catalyst access switches integrated with Cisco ISE. After Cisco ISE profiles each endpoint, an authorization policy must dynamically move the device into a dedicated IoT VLAN that differs from the access VLAN statically defined on the port. The endpoints lack a supplicant and cannot automatically renew their DHCP addresses. The network engineer requires Cisco ISE to issue a Change of Authorization that forces each endpoint to re-establish connectivity and request a fresh DHCP lease under the new authorization policy. Which configuration action must be performed on Cisco ISE to meet the requirement?

Options:

A.

Configure the authorization profile to send a CoA-Reauth to the access switch.

B.

Configure the authentication policy to send a CoA-Terminate to reconnect the endpoint.

C.

Configure the authorization profile to send a Port-Bounce CoA to the switch.

D.

Configure the authorization policy to send a CoA-Reconnect and rely on the idle timeout.

Buy Now
Questions 48

A switch with Dynamic ARP Inspection enabled has received a spoofed ARP response on a trusted interface.

How does the switch behave in this situation?

Options:

A.

It forwards the packet after validation by using the MAC Binding Table.

B.

It drops the packet after validation by using the IP & MAC Binding Table.

C.

It forwards the packet without validation.

D.

It drops the packet without validation.

Buy Now
Questions 49

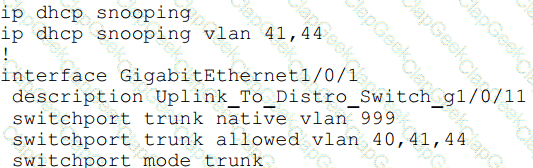
Refer to the exhibit.

An organization is using DHCP Snooping within their network. A user on VLAN 41 on a new switch is

complaining that an IP address is not being obtained. Which command should be configured on the switch

interface in order to provide the user with network connectivity?

Options:

A.

ip dhcp snooping verify mac-address

B.

ip dhcp snooping limit 41

C.

ip dhcp snooping vlan 41

D.

ip dhcp snooping trust

Buy Now
Questions 50

What is the term for the concept of limiting communication between applications or containers on the same node?

Options:

A.

container orchestration

B.

software-defined access

C.

microservicing

D.

microsegmentation

Buy Now
Questions 51

Which two Cisco Umbrella security categories are used to prevent command-and-control callbacks on port 53 and protect users from being tricked into providing confidential information? (Choose two.)

Options:

A.

DNS Tunneling VPN

B.

Dynamic DNS

C.

Newly Seen Domains

D.

Potentially Harmful Domains

E.

Phishing Attacks

Buy Now
Questions 52

Which technology must be used to implement secure VPN connectivity among company branches over a

private IP cloud with any-to-any scalable connectivity?

Options:

A.

DMVPN

B.

FlexVPN

C.

IPsec DVTI

D.

GET VPN

Buy Now
Questions 53

An engineer notices traffic interruption on the network. Upon further investigation, it is learned that broadcast

packets have been flooding the network. What must be configured, based on a predefined threshold, to

address this issue?

Options:

A.

Bridge Protocol Data Unit guard

B.

embedded event monitoring

C.

storm control

D.

access control lists

Buy Now
Questions 54

Based on the NIST 800-145 guide, which cloud architecture is provisioned for exclusive use by a specific group of consumers from different organizations and may be owned, managed, and operated by one or more of those organizations?

Options:

A.

hybrid cloud

B.

private cloud

C.

community cloud

D.

public cloud

Buy Now
Questions 55

Which encryption algorithm provides highly secure VPN communications?

Options:

A.

3DES

B.

AES 256

C.

AES 128

D.

DES

Buy Now
Questions 56

An engineer implements Cisco CloudLock to secure a Microsoft Office 365 application in the cloud. The engineer must configure protection for corporate files in case of any incidents. Which two actions must be taken to complete the implementation? (Choose two.)

Options:

A.

Expire the public share URL

B.

Send Cisco Webex message to specified users when an incident is triggered

C.

Transfer ownership of the files to a specified owner and folder

D.

Remove all users as collaborators on the files

E.

Disable the ability for commenters and viewers to download and copy the files

Buy Now
Questions 57

During a recent security audit a Cisco IOS router with a working IPSEC configuration using IKEv1 was flagged for using a wildcard mask with the crypto isakmp key command The VPN peer is a SOHO router with a dynamically assigned IP address Dynamic DNS has been configured on the SOHO router to map the dynamic IP address to the host name of vpn sohoroutercompany.com In addition to the command crypto isakmp key Cisc425007536 hostname vpn.sohoroutercompany.com what other two commands are now required on the Cisco IOS router for the VPN to continue to function after the wildcard command is removed? (Choose two)

Options:

A.

ip host vpn.sohoroutercompany.eom < VPN Peer IP Address >

B.

crypto isakmp identity hostname

C.

Add the dynamic keyword to the existing crypto map command

D.

fqdn vpn.sohoroutercompany.com < VPN Peer IP Address >

E.

ip name-server < DNS Server IP Address >

Buy Now
Questions 58

An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users. Which action accomplishes this goal?

Options:

A.

Restrict access to only websites with trusted third-party signed certificates.

B.

Modify the user’s browser settings to suppress errors from Cisco Umbrella.

C.

Upload the organization root CA to Cisco Umbrella.

D.

Install the Cisco Umbrella root CA onto the user’s device.

Buy Now
Questions 59

An organization recently installed a Cisco Secure Web Appliance and would like to take advantage of the AVC engine to allow the organization to create a policy to control application-specific activity. After enabling the AVC engine, what must be done to implement this?

Options:

A.

Use an access policy group to configure application control settings.

B.

Use security services to configure the traffic monitor.

C.

Use URL categorization to prevent the application traffic.

D.

Use web security reporting to validate engine functionality.

Buy Now
Questions 60

Which industry standard is used to integrate Cisco ISE and pxGrid to each other and with other

interoperable security platforms?

Options:

A.

IEEE

B.

IETF

C.

NIST

D.

ANSI

Buy Now
Questions 61

Which network monitoring solution uses streams and pushes operational data to provide a near real-time view

of activity?

Options:

A.

SNMP

B.

SMTP

C.

syslog

D.

model-driven telemetry

Buy Now
Questions 62

Which type of dashboard does Cisco DNA Center provide for complete control of the network?

Options:

A.

service management

B.

centralized management

C.

application management

D.

distributed management

Buy Now
Questions 63

Which endpoint solution protects a user from a phishing attack?

Options:

A.

Cisco Identity Services Engine

B.

Cisco AnyConnect with ISE Posture module

C.

Cisco AnyConnect with Network Access Manager module

D.

Cisco AnyConnect with Umbrella Roaming Security module

Buy Now
Questions 64

Which Cisco security solution stops exfiltration using HTTPS?

Options:

A.

Cisco FTD

B.

Cisco AnyConnect

C.

Cisco CTA

D.

Cisco ASA

Buy Now
Questions 65

A malicious user gained network access by spoofing printer connections that were authorized using MAB on

four different switch ports at the same time. What two catalyst switch security features will prevent further

violations? (Choose two)

Options:

A.

DHCP Snooping

B.

802.1AE MacSec

C.

Port security

D.

IP Device track

E.

Dynamic ARP inspection

F.

Private VLANs

Buy Now
Questions 66

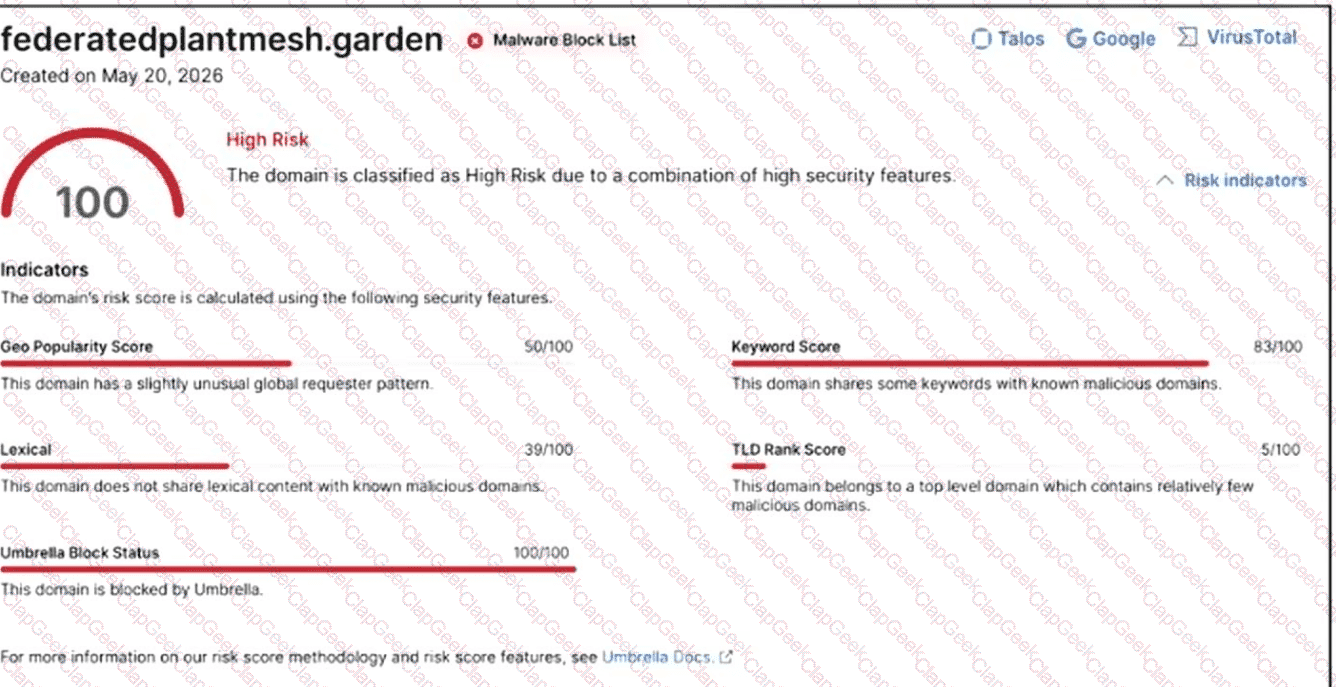
Refer to the exhibit.

A threat analyst is investigating the domain federatedplantmesh.garden after it appeared in DNS logs from several roaming users. In the Cisco Secure Access Investigate dashboard, the analyst notes that several individual indicators, including Lexical, TLD, and Geo Popularity, are not strongly elevated, yet the overall Risk Score is 100. What is occurring?
Options:

A.

The overall score of 100 is inconsistent and likely a dashboard-rendering error; the domain must be queried again before the classification is trusted.

B.

The infrastructure fields are blank, but the Umbrella Block Status of 100/100 and the malware security category identify the non-resolving domain as high risk.

C.

The Keyword Score of 83 is the only elevated indicator driving the overall score, and the classification is invalid unless confirmed through the Dispute Categorization link.

D.

The Dispute Categorization link means that the malware classification is contested, and the blank IP and ASN fields confirm that the domain has no active threat infrastructure.

Buy Now
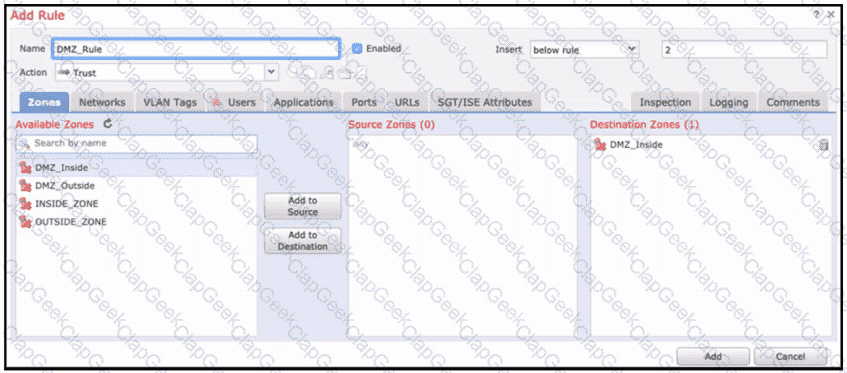
Questions 67

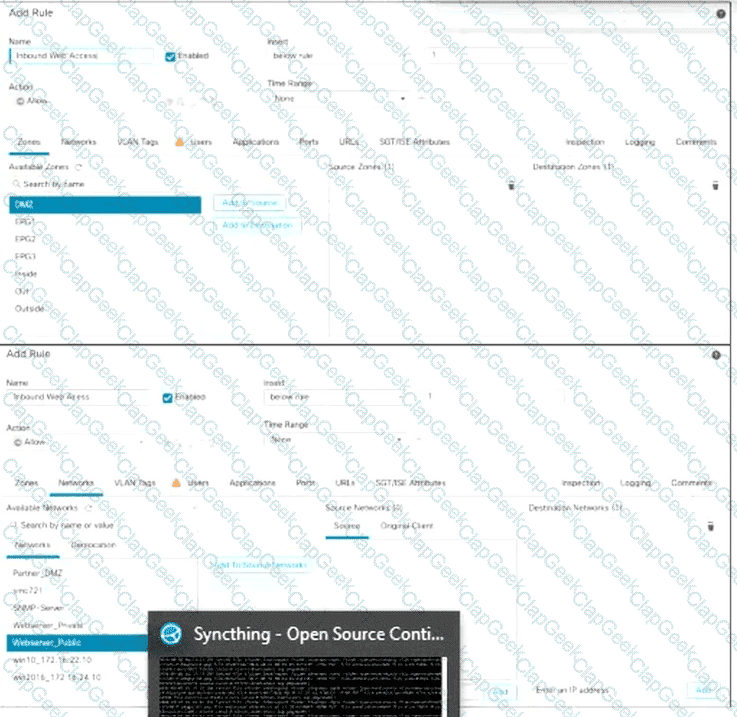
Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?

Options:

A.

All traffic from any zone will be allowed to the DMZ_inside zone only after inspection.

B.

No traffic will be allowed through to the DMZ_inside zone regardless of if it ' s trusted or not.

C.

No traffic will be allowed through to the DMZ_inside zone unless it ' s already trusted.

D.

All traffic from any zone to the DMZ_inside zone will be permitted with no further inspection.

Buy Now
Questions 68

Which Cisco cloud security software centrally manages policies on multiple platforms such as Cisco ASA, Cisco Firepower, Cisco Meraki, and AWS?

Options:

A.

Cisco Defense Orchestrator

B.

Cisco Configuration Professional

C.

Cisco Secureworks

D.

Cisco DNAC

Buy Now
Questions 69

Which feature must be configured before implementing NetFlow on a router?

Options:

A.

SNMPv3

B.

syslog

C.

VRF

D.

IP routing

Buy Now
Questions 70

Which component of Cisco umbrella architecture increases reliability of the service?

Options:

A.

Anycast IP

B.

AMP Threat grid

C.

Cisco Talos

D.

BGP route reflector

Buy Now
Questions 71

Which two protocols must be configured to authenticate end users to the Web Security Appliance? (Choose two.)

Options:

A.

NTLMSSP

B.

Kerberos

C.

CHAP

D.

TACACS+

E.

RADIUS

Buy Now
Questions 72

An engineer must deploy a Cisco Secure Web Appliance. Antimalware scanning must use the Outbreak Heuristics antimalware category on files identified as malware before performing any other processes. What must be configured on the Secure Web Appliance to meet the requirements?

Options:

A.

Sophos scanning engine

B.

Webroot scanning engine

C.

McAfee scanning engine

D.

Adaptive Scanning

Buy Now
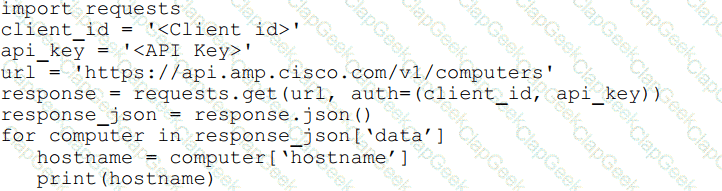
Questions 73

Refer to the exhibit.

What will happen when the Python script is executed?

Options:

A.

The hostname will be translated to an IP address and printed.

B.

The hostname will be printed for the client in the client ID field.

C.

The script will pull all computer hostnames and print them.

D.

The script will translate the IP address to FODN and print it

Buy Now
Questions 74

A network engineer is trying to figure out whether FlexVPN or DMVPN would fit better in their environment.

They have a requirement for more stringent security multiple security associations for the connections, more efficient VPN establishment as well consuming less bandwidth. Which solution would be best for this and why?

Options:

A.

DMVPN because it supports IKEv2 and FlexVPN does not

B.

FlexVPN because it supports IKEv2 and DMVPN does not

C.

FlexVPN because it uses multiple SAs and DMVPN does not

D.

DMVPN because it uses multiple SAs and FlexVPN does not

Buy Now
Questions 75

An engineer needs a cloud solution that will monitor traffic, create incidents based on events, and integrate with

other cloud solutions via an API. Which solution should be used to accomplish this goal?

Options:

A.

SIEM

B.

CASB

C.

Adaptive MFA

D.

Cisco Cloudlock

Buy Now
Questions 76

What are two functionalities of SDN Northbound APIs? (Choose two.)

Options:

A.

Northbound APIs provide a programmable interface for applications to dynamically configure the network.

B.

Northbound APIs form the interface between the SDN controller and business applications.

C.

OpenFlow is a standardized northbound API protocol.

D.

Northbound APIs use the NETCONF protocol to communicate with applications.

E.

Northbound APIs form the interface between the SDN controller and the network switches or routers.

Buy Now
Questions 77

Drag and drop the features of Cisco ASA with Firepower from the left onto the benefits on the right.
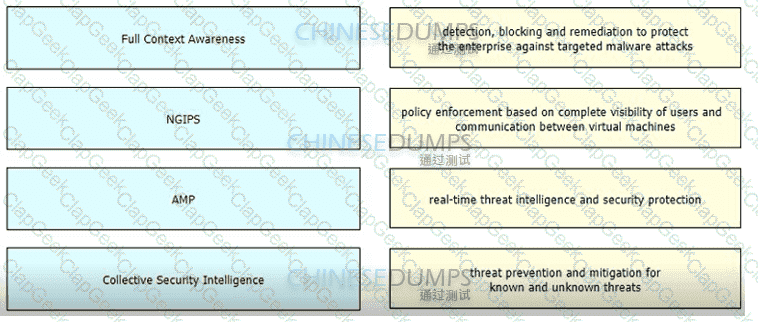
Options:

Buy Now
Questions 78

An organization is using Cisco Firepower and Cisco Meraki MX for network security and needs to centrally

manage cloud policies across these platforms. Which software should be used to accomplish this goal?

Options:

A.

Cisco Defense Orchestrator

B.

Cisco Secureworks

C.

Cisco DNA Center

D.

Cisco Configuration Professional

Buy Now
Questions 79

What is the term for when an endpoint is associated to a provisioning WLAN that is shared with guest

access, and the same guest portal is used as the BYOD portal?

Options:

A.

single-SSID BYOD

B.

multichannel GUI

C.

dual-SSID BYOD

D.

streamlined access

Buy Now
Questions 80

Which portion of the network do EPP solutions solely focus on and EDR solutions do not?

Options:

A.

server farm

B.

perimeter

C.

core

D.

East-West gateways

Buy Now
Questions 81

What is a required prerequisite to enable malware file scanning for the Secure Internet Gateway?

Options:

A.

Enable IP Layer enforcement.

B.

Activate the Advanced Malware Protection license

C.

Activate SSL decryption.

D.

Enable Intelligent Proxy.

Buy Now
Questions 82

Which feature enables a Cisco ISR to use the default bypass list automatically for web filtering?

Options:

A.

filters

B.

group key

C.

company key

D.

connector

Buy Now
Questions 83

How is Cisco Umbrella configured to log only security events?

Options:

A.

per policy

B.

in the Reporting settings

C.

in the Security Settings section

D.

per network in the Deployments section

Buy Now
Questions 84

A pharmaceutical research facility has implemented a “Clean Room” network segment to protect sensitive research data and automated manufacturing equipment. Strict compliance requirements mandate that all network traffic logs from the Cisco Secure Firewall serving the segment be forwarded to Splunk for auditing. A Splunk Universal Forwarder is deployed locally on the log-collection servers to monitor syslog files. The engineer must configure the Universal Forwarder to monitor the local syslog files and assign a specific source type for proper ingestion into Splunk. Which stanza configuration must be used to meet the requirements?

Options:

A.

inputs.conf using [monitor:///var/log/syslog]

B.

server.conf using [monitor:///syslog]

C.

props.conf using [syslog]

D.

outputs.conf using [tcpout]

Buy Now
Questions 85

A security engineer must protect endpoints when a file appears harmless during initial inspection but later shows malicious behavior. The solution must continuously observe process and file activity after execution and respond when a threat emerges. The infrastructure includes Cisco Secure Endpoint. Which feature must the engineer configure to meet the requirements?

Options:

A.

File Reputation

B.

Continuous Behavioral Monitoring

C.

Forensic Analysis

D.

System Process Protection

Buy Now
Questions 86

An engineer must implement a file transfer solution between a company ' s data center and branches. The company has numerous servers hosted in a hybrid cloud implementation. The file transfer protocol must support authentication, protect the data against unauthorized access, and ensure that users cannot list directories or remove files remotely. Which protocol must be used?

Options:

A.

SCP

B.

SSH

C.

FTPS

D.

SFTP

Buy Now
Questions 87

How is a cross-site scripting attack executed?

Options:

A.

Force a currently authenticated end user to execute unwanted actions on a web app

B.

Execute malicious client-side scripts injected to a client via a web app

C.

Inject a database query via the input data from the client to a web app

D.

Intercept communications between a client and a web server

Buy Now
Questions 88

Which Cisco ISE feature helps to detect missing patches and helps with remediation?

Options:

A.

posture assessment

B.

profiling policy

C.

authentication policy

D.

enabling probes

Buy Now
Questions 89

An engineer is configuring Cisco WSA and needs to enable a separated email transfer flow from the Internet and from the LAN. Which deployment mode must be used to accomplish this goal?

Options:

A.

single interface

B.

multi-context

C.

transparent

D.

two-interface

Buy Now
Questions 90

What are two characteristics of Cisco Catalyst Center APIs? (Choose two.)

Options:

A.

Postman is required to utilize Cisco Catalyst Center API calls.

B.

They are Cisco proprietary.

C.

They do not support Python scripts.

D.

They view the overall health of the network.

E.

They quickly provision new devices.

Buy Now
Questions 91

An engineer is configuring AMP for endpoints and wants to block certain files from executing. Which outbreak

control method is used to accomplish this task?

Options:

A.

device flow correlation

B.

simple detections

C.

application blocking list

D.

advanced custom detections

Buy Now
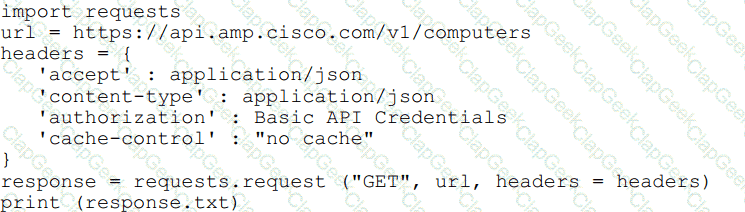
Questions 92

Refer to the exhibit.

What will happen when this Python script is run?

Options:

A.

The compromised computers and malware trajectories will be received from Cisco AMP

B.

The list of computers and their current vulnerabilities will be received from Cisco AMP

C.

The compromised computers and what compromised them will be received from Cisco AMP

D.

The list of computers, policies, and connector statuses will be received from Cisco AMP

Buy Now
Questions 93

A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?

Options:

A.

Enable global settings with default URL filtering.

B.

Configure a file policy in an access control policy.

C.

Apply web filtering in an access control policy.

D.

Block the social-media URL category in the destination-network condition of an access control rule.

Buy Now
Questions 94

What is the difference between a vulnerability and an exploit?

Options:

A.

A vulnerability is a hypothetical event for an attacker to exploit

B.

A vulnerability is a weakness that can be exploited by an attacker

C.

An exploit is a weakness that can cause a vulnerability in the network

D.

An exploit is a hypothetical event that causes a vulnerability in the network

Buy Now
Questions 95

An engineer integrates Cisco FMC and Cisco ISE using pxGrid Which role is assigned for Cisco FMC?

Options:

A.

client

B.

server

C.

controller

D.

publisher

Buy Now
Questions 96

Which action configures the IEEE 802.1X Flexible Authentication feature lo support Layer 3 authentication mechanisms?

Options:

A.

Identity the devices using this feature and create a policy that allows them to pass Layer 2 authentication.

B.

Configure WebAuth so the hosts are redirected to a web page for authentication.

C.

Modify the Dot1x configuration on the VPN server lo send Layer 3 authentications to an external authentication database

D.

Add MAB into the switch to allow redirection to a Layer 3 device for authentication.

Buy Now
Questions 97

Client workstations are experiencing extremely poor response time. An engineer suspects that an attacker is eavesdropping and making independent connections while relaying messages between victims to make them think they are talking to each other over a private connection. Which feature must be enabled and configured to provide relief from this type of attack?

Options:

A.

Link Aggregation

B.

Reverse ARP

C.

private VLANs

D.

Dynamic ARP Inspection

Buy Now
Questions 98

Which Cisco platform provides an agentless solution to provide visibility across the network including encrypted traffic analytics to detect malware in encrypted traffic without the need for decryption?

Options:

A.

Cisco Advanced Malware Protection

B.

Cisco Stealthwatch

C.

Cisco Identity Services Engine

D.

Cisco AnyConnect

Buy Now
Questions 99

What are two functions of TAXII in threat intelligence sharing? (Choose two.)

Options:

A.

determines the " what " of threat intelligence

B.

Supports STIX information

C.

allows users to describe threat motivations and abilities

D.

exchanges trusted anomaly intelligence information

E.

determines how threat intelligence information is relayed

Buy Now
Questions 100

What is a benefit of using a multifactor authentication strategy?

Options:

A.

It provides visibility into devices to establish device trust.

B.

It provides secure remote access for applications.

C.

It provides an easy, single sign-on experience against multiple applications

D.

lt protects data by enabling the use of a second validation of identity.

Buy Now
Questions 101

What is the function of Cisco Cloudlock for data security?

Options:

A.

data loss prevention

B.

controls malicious cloud apps

C.

detects anomalies

D.

user and entity behavior analytics

Buy Now
Questions 102

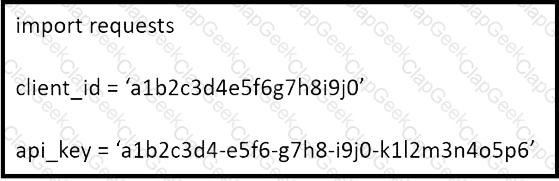
Refer to the exhibit.

What does the API key do while working with https://api.amp.cisco.com/v1/computers?

Options:

A.

displays client ID

B.

HTTP authorization

C.

Imports requests

D.

HTTP authentication

Buy Now
Questions 103

Which Cisco product provides proactive endpoint protection and allows administrators to centrally manage the

deployment?

Options:

A.

NGFW

B.

AMP

C.

WSA

D.

ESA

Buy Now
Questions 104

An engineer is configuring Cisco Secure Endpoint to enhance network security by specifying a large set of external IP addresses that must be monitored for potential threats. The engineer is configuring an IP List and must add the IP addresses to the list. Which configuration action must the engineer take next to meet the requirement?

Options:

A.

Add the IP addresses using the global bulk configuration wizard.

B.

Automate a threat-feed subscription using an API.

C.

Use the data-upload function and import a file formatted as JSON.

D.

Use the Add Multiple Rows feature and paste all addresses into the input field.

Buy Now
Questions 105

Which solution detects threats across a private network, public clouds, and encrypted traffic?

Options:

A.

Cisco Stealthwatch

B.

Cisco CTA

C.

Cisco Encrypted Traffic Analytics

D.

Cisco Umbrella

Buy Now
Questions 106

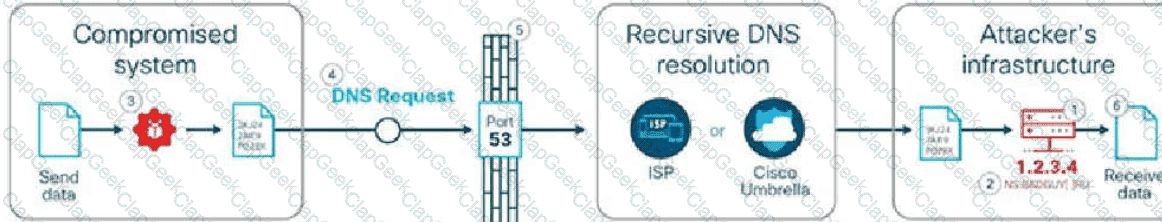
How is data sent out to the attacker during a DNS tunneling attack?

Options:

A.

as part of the UDP/53 packet payload

B.

as part of the domain name

C.

as part of the TCP/53 packet header

D.

as part of the DNS response packet

Buy Now
Questions 107

A network engineer must enable DHCP snooping on the corporate switches only for VLAN 2. Management requires DHCP traffic from unauthorized servers to be dropped. DHCP snooping is already enabled globally, and the uplink interface toward the authorized DHCP server is already trusted. Which configuration command must be applied to meet the requirement?

Options:

A.

ip dhcp snooping trust vlan 2

B.

ip dhcp relay information trusted vlan 2

C.

ip dhcp snooping information option vlan 2

D.

ip dhcp snooping vlan 2

Buy Now
Questions 108

What is an advantage of network telemetry over SNMP pulls?

Options:

A.

accuracy

B.

encapsulation

C.

security

D.

scalability

Buy Now
Questions 109

Which CoA response code is sent if an authorization state is changed successfully on a Cisco IOS device?

Options:

A.

CoA-NCL

B.

CoA-NAK

C.

СоА-МАВ

D.

CoA-ACK

Buy Now
Questions 110

An organization has two systems in their DMZ that have an unencrypted link between them for communication.

The organization does not have a defined password policy and uses several default accounts on the systems.

The application used on those systems also have not gone through stringent code reviews. Which vulnerability

would help an attacker brute force their way into the systems?

Options:

A.

weak passwords

B.

lack of input validation

C.

missing encryption

D.

lack of file permission

Buy Now
Questions 111

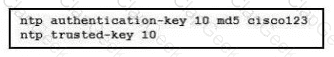
Refer to the exhibit.

A network engineer is testing NTP authentication and realizes that any device synchronizes time with this router and that NTP authentication is not enforced What is the cause of this issue?

Options:

A.

The key was configured in plain text.

B.

NTP authentication is not enabled.

C.

The hashing algorithm that was used was MD5. which is unsupported.

D.

The router was not rebooted after the NTP configuration updated.

Buy Now
Questions 112

An engineer must deploy Cisco Secure Email with Cloud URL Analysis and must meet these requirements:

To protect the network from large-scale virus outbreaks

To protect the network from non-viral attacks such as phishing scams and malware distribution

To provide active analysis of the structure of the URL and information about the domain and page contents

Which two prerequisites must the engineer ensure are configured? (Choose two.)

Options:

A.

Scanning enabled for each Verdict, Prepend Subject and Deliver.

B.

Outbreak Filters must be enabled globally.

C.

Enable TLS by setting to Preferred to the Default Domain.

D.

Service Logs must be enabled.

E.

Enable Rejected Connection Logging.

Buy Now
Questions 113

Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize

applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?

Options:

A.

Cisco Security Intelligence

B.

Cisco Application Visibility and Control

C.

Cisco Model Driven Telemetry

D.

Cisco DNA Center

Buy Now
Questions 114

Which action must be taken in the AMP for Endpoints console to detect specific MD5 signatures on endpoints and then quarantine the files?

Options:

A.

Configure an advanced custom detection list.

B.

Configure an IP Block & Allow custom detection list

C.

Configure an application custom detection list

D.

Configure a simple custom detection list

Buy Now
Questions 115

Which protocol does the BYOD component in Cisco ISE use to obtain a unique device certificate from an internal CA?

Options:

A.

CMP

B.

SCEP

C.

SFTP

D.

OCSP

Buy Now
Questions 116

Which two deployment modes does the Cisco ASA FirePower module support? (Choose two)

Options:

A.

transparent mode

B.

routed mode

C.

inline mode

D.

active mode

E.

passive monitor-only mode

Buy Now
Questions 117

An engineer must configure Cisco AMP for Endpoints so that it contains a list of files that should not be executed by users. These files must not be quarantined. Which action meets this configuration requirement?

Options:

A.

Identity the network IPs and place them in a blocked list.

B.

Modify the advanced custom detection list to include these files.

C.

Create an application control blocked applications list.

D.

Add a list for simple custom detection.

Buy Now
Questions 118

An administrator is establishing a new site-to-site VPN connection on a Cisco IOS router. The organization

needs to ensure that the ISAKMP key on the hub is used only for terminating traffic from the IP address of

172.19.20.24. Which command on the hub will allow the administrator to accomplish this?

Options:

A.

crypto ca identity 172.19.20.24

B.

crypto isakmp key Cisco0123456789 172.19.20.24

C.

crypto enrollment peer address 172.19.20.24

D.

crypto isakmp identity address 172.19.20.24

Buy Now
Questions 119

Which license is required for Cisco Security Intelligence to work on the Cisco Next Generation Intrusion

Prevention System?

Options:

A.

control

B.

malware

C.

URL filtering

D.

protect

Buy Now
Questions 120

Refer to the exhibit. When creating an access rule for URL filtering, a network engineer adds certain categories and individual URLs to block. What is the result of the configuration?

Options:

A.

Only URLs for botnets with reputation scores of 1-3 will be blocked.

B.

Only URLs for botnets with a reputation score of 3 will be blocked.

C.

Only URLs for botnets with reputation scores of 3-5 will be blocked.

D.

Only URLs for botnets with a reputation score of 3 will be allowed while the rest will be blocked.

Buy Now
Questions 121

Which proxy mode must be used on Cisco WSA to redirect TCP traffic with WCCP?

Options:

A.

transparent

B.

redirection

C.

forward

D.

proxy gateway

Buy Now
Questions 122

A recent change left network engineers unable to SSH into a branch Cisco Catalyst switch. The engineer confirms that the TACACS server group TACACS-GROUP is defined but unreachable. There is no fallback to the local database when TACACS+ is unavailable. Security policy requires TACACS+ as the primary authentication method with automatic fallback to local accounts. Which configuration command must be added to resolve the issue?

Options:

A.

aaa authentication login ssh LOCAL TACACS-GROUP

B.

aaa authentication login group TACACS-GROUP local

C.

aaa authentication login default group TACACS-GROUP local

D.

aaa authentication serial console TACACS-GROUP LOCAL

Buy Now
Questions 123

What is a benefit of using Cisco FMC over Cisco ASDM?

Options:

A.

Cisco FMC uses Java while Cisco ASDM uses HTML5.

B.

Cisco FMC provides centralized management while Cisco ASDM does not.

C.

Cisco FMC supports pushing configurations to devices while Cisco ASDM does not.

D.

Cisco FMC supports all firewall products whereas Cisco ASDM only supports Cisco ASA devices

Buy Now
Questions 124

An administrator configures a Cisco WSA to receive redirected traffic over ports 80 and 443. The organization requires that a network device with specific WSA integration capabilities be configured to send the traffic to the WSA to proxy the requests and increase visibility, while making this invisible to the users. What must be done on the Cisco WSA to support these requirements?

Options:

A.

Configure transparent traffic redirection using WCCP in the Cisco WSA and on the network device

B.

Configure active traffic redirection using WPAD in the Cisco WSA and on the network device

C.

Use the Layer 4 setting in the Cisco WSA to receive explicit forward requests from the network device

D.

Use PAC keys to allow only the required network devices to send the traffic to the Cisco WSA

Buy Now
Questions 125

What must be enabled to secure SaaS-based applications?

Options:

A.

modular policy framework

B.

two-factor authentication

C.

application security gateway

D.

end-to-end encryption

Buy Now
Questions 126

Which statement about IOS zone-based firewalls is true?

Options:

A.

An unassigned interface can communicate with assigned interfaces

B.

Only one interface can be assigned to a zone.

C.

An interface can be assigned to multiple zones.

D.

An interface can be assigned only to one zone.

Buy Now
Questions 127

A network engineer is tasked with configuring a Cisco ISE server to implement external authentication against Active Directory. What must be considered about the authentication requirements? (Choose two.)

Options:

A.

RADIUS communication must be permitted between the ISE server and the domain controller.

B.

The ISE account must be a domain administrator in Active Directory to perform JOIN operations.

C.

Active Directory only supports user authentication by using MSCHAPv2.

D.

LDAP communication must be permitted between the ISE server and the domain controller.

E.

Active Directory supports user and machine authentication by using MSCHAPv2.

Buy Now
Questions 128

What limits communication between applications or containers on the same node?

Options:

A.

microsegmentation

B.

container orchestration

C.

microservicing

D.

Software-Defined Access

Buy Now
Questions 129

Using Cisco Cognitive Threat Analytics, which platform automatically blocks risky sites, and test unknown sites for hidden advanced threats before allowing users to click them?

Options:

A.

Cisco Identity Services Engine (ISE)

B.

Cisco Enterprise Security Appliance (ESA)

C.

Cisco Web Security Appliance (WSA)

D.

Cisco Advanced Stealthwatch Appliance (ASA)

Buy Now
Questions 130

Which role is a default guest type in Cisco ISE?

Options:

A.

Monthly

B.

Yearly

C.

Contractor

D.

Full-Time

Buy Now
Questions 131

How is DNS tunneling used to exfiltrate data out of a corporate network?

Options:

A.

It corrupts DNS servers by replacing the actual IP address with a rogue address to collect information or start other attacks.

B.

It encodes the payload with random characters that are broken into short strings and the DNS serverrebuilds the exfiltrated data.

C.

It redirects DNS requests to a malicious server used to steal user credentials, which allows further damageand theft on the network.

D.

It leverages the DNS server by permitting recursive lookups to spread the attack to other DNS servers.

Buy Now
Questions 132

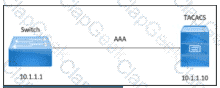
Refer to the exhibit.

An engineer must configure a Cisco switch to perform PPP authentication via a TACACS server located at IP address 10.1.1.10. Authentication must fall back to the local database using the username LocalUser and password C1Sc0451069341l if the TACACS server is unreachable.

Drag and drop the commands from the left onto the corresponding configuration steps on the right.
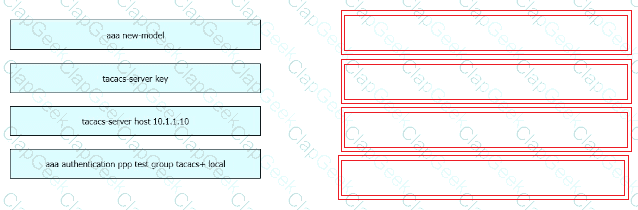
Options:

Buy Now
Questions 133

Which capability allows an administrator to configure forensics rules in Cisco Secure Workload?

Options:

A.

Custom clauses

B.

MITRE ATT & CK framework only predefined

C.

Cisco Secure Workload predefined

D.

Windows or Linux application

Buy Now
Questions 134

A large retail enterprise is deploying Cisco Secure Private Access to enable remote employees to reach internal applications without manual intervention. The IT department requires a seamless, zero-touch enrollment process in which users are registered and authenticated transparently without requiring end-user action. The architecture must support robust high availability for back-end connectivity to ensure continuous access to private resources. Which configuration approach must the administrator implement to meet the requirement?

Options:

A.

Implement ZTA with Certificate Enrollment and multiple Connector Groups associated with the private resource.

B.

Configure ZTA with SAML Enrollment and multiple Connector Groups associated with the private resource.

C.

Define a VPN Machine Tunnel with Certificate Enrollment and Connector Groups associated with the private resource.

D.

Apply ZTA with SAML Enrollment, including passwordless enrollment, and a single Connector associated with the private resource.

Buy Now
Questions 135

Which two application layer preprocessors are used by Firepower Next Generation Intrusion Prevention

System? (Choose two)

Options:

A.

packet decoder

B.

SIP

C.

modbus

D.

inline normalization

E.

SSL

Buy Now
Questions 136

What does Cisco AMP for Endpoints use to help an organization detect different families of malware?

Options:

A.

Ethos Engine to perform fuzzy fingerprinting

B.

Tetra Engine to detect malware when me endpoint is connected to the cloud

C.

Clam AV Engine to perform email scanning

D.

Spero Engine with machine learning to perform dynamic analysis

Buy Now
Questions 137

Drag and drop the suspicious patterns for the Cisco Tetration platform from the left onto the correct definitions on the right.
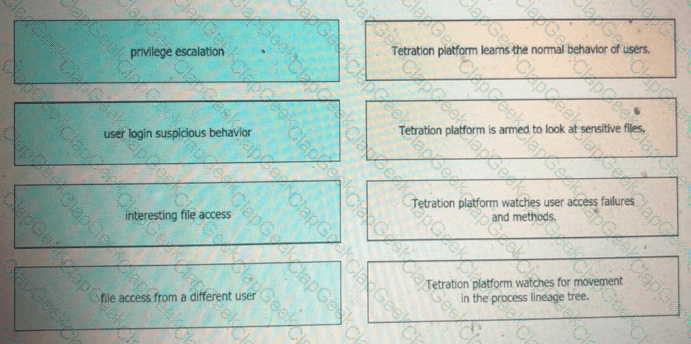
Options:

Buy Now
Questions 138

A Cisco Firepower administrator needs to configure a rule to allow a new application that has never been seen

on the network. Which two actions should be selected to allow the traffic to pass without inspection? (Choose

two)

Options:

A.

permit

B.

trust

C.

reset

D.

allow

E.

monitor

Buy Now
Questions 139

Which component of a Cisco IOS NetFlow solution enables the aggregation of data packets into flows?

Options:

A.

Analyzer

B.

Sampler

C.

Collector

D.

Exporter

Buy Now
Questions 140

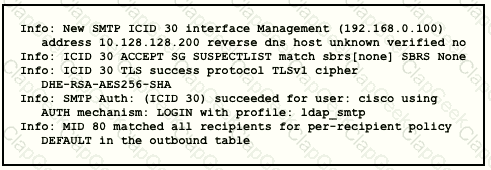
Refer to the exhibit.

Which type of authentication is in use?

Options:

A.

LDAP authentication for Microsoft Outlook

B.

POP3 authentication

C.

SMTP relay server authentication

D.

external user and relay mail authentication

Buy Now
Questions 141

Which two features of Cisco Email Security can protect your organization against email threats? (Choose two)

Options:

A.

Time-based one-time passwords

B.

Data loss prevention

C.

Heuristic-based filtering

D.

Geolocation-based filtering

E.

NetFlow

Buy Now
Questions 142

After deploying a Cisco ESA on your network, you notice that some messages fail to reach their destinations.

Which task can you perform to determine where each message was lost?

Options:

A.

Configure the trackingconfig command to enable message tracking.

B.

Generate a system report.

C.

Review the log files.

D.

Perform a trace.

Buy Now
Questions 143

What is the recommendation in a zero-trust model before granting access to corporate applications and resources?

Options:

A.

To use a wired network, not wireless

B.

To use strong passwords

C.

To use multifactor authentication

D.

To disconnect from the network when inactive

Buy Now
Questions 144

Refer to the exhibit.

aaa new-model

aaa authentication dot1x default group ISE-SERVERS

aaa authorization network default group ISE-SERVERS

aaa accounting dot1x default start-stop group ISE-SERVERS

!

radius server RADIUS_SRV

address ipv4 172.16.10.12 auth-port 1812 acct-port 1813

key shared-secret C1sc0123

!

aaa group server radius ISE-SERVERS

server name RADIUS_SRV

radius-server vsa send authentication

radius-server vsa send accounting

radius-server attribute 6 on-for-login-auth

radius-server attribute 8 include-in-access-req

radius-server attribute 25 access-request include

ip device tracking

!

interface range GigabitEthernet1/0/1 - 48

switchport

switchport host

authentication priority dot1x mab

authentication order dot1x mab

A security engineer is integrating a new Cisco Catalyst access switch with Cisco ISE to enforce port-based network access control using 802.1X. The AAA RADIUS server group and access interfaces are configured on the Cisco Catalyst switch. Cisco ISE has authentication and authorization policies, the workstation supplicants are configured as expected, and connectivity between the switch and ISE is working. During testing, the workstations fail to trigger authentication sessions, and no RADIUS requests appear in the ISE logs or on the switch interfaces. Which two configuration commands must be added to the Cisco Catalyst switch? (Choose two.)

Options:

A.

Configure the dot1x system-auth-control command globally.

B.

Implement the aaa server radius dynamic-author command globally.

C.

Apply the dot1x pae authenticator command under interfaces that require 802.1X.

D.

Configure the ip radius source-interface command globally.

E.

Add the mab command under all switch interfaces.

Buy Now
Questions 145

Which security solution protects users leveraging DNS-layer security?

Options:

A.

Cisco ISE

B.

Cisco FTD

C.

Cisco Umbrella

D.

Cisco ASA

Buy Now
Questions 146

What is the purpose of the Trusted Automated exchange cyber threat intelligence industry standard?

Options:

A.

public collection of threat intelligence feeds

B.

threat intelligence sharing organization

C.

language used to represent security information

D.

service used to exchange security information

Buy Now
Questions 147

What is an advantage of using a next-generation firewall compared to a traditional firewall?

Options:

A.

Next-generation firewalls have stateless inspection capabilities, and traditional firewalls use stateful inspection.

B.

Next-generation firewalls use dynamic packet filtering, and traditional firewalls use static packet filtering.

C.

Next-generation firewalls have threat intelligence feeds, and traditional firewalls use signature detection.

D.

Next-generation firewalls use intrusion prevention policies, and traditional firewalls use intrusion detection policies.

Buy Now
Questions 148

Which posture assessment requirement provides options to the client for remediation and requires the

remediation within a certain timeframe?

Options:

A.

Audit

B.

Mandatory

C.

Optional

D.

Visibility

Buy Now
Questions 149

Drag and drop the VPN functions from the left onto the descriptions on the right.
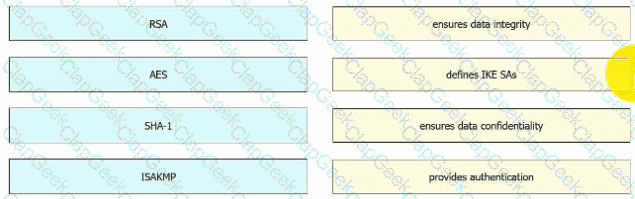
Options:

Buy Now
Questions 150

When NetFlow is applied to an interface, which component creates the flow monitor cache that is used

to collect traffic based on the key and nonkey fields in the configured record?

Options:

A.

records

B.

flow exporter

C.

flow sampler

D.

flow monitor

Buy Now
Questions 151

An administrator has been tasked with configuring the Cisco Secure Email Gateway to ensure there are no viruses before quarantined emails are delivered. In addition, delivery of mail from known bad mail servers must be prevented. Which two actions must be taken in order to meet these requirements? (Choose two.)

Options:

A.

Deploy the Secure Email Gateway in the DMZ.

B.

Use outbreak filters from Cisco Talos.

C.

Configure a recipient access table.

D.

Enable a message tracking service.

E.

Scan quarantined emails using AntiVirus signatures.

Buy Now
Questions 152

Which VMware platform does Cisco ACI integrate with to provide enhanced visibility, provide policy integration and deployment, and implement security policies with access lists?

Options:

A.

VMware APIC

B.

VMwarevRealize

C.

VMware fusion

D.

VMware horizons

Buy Now
Questions 153

What are two list types within AMP for Endpoints Outbreak Control? (Choose two)

Options:

A.

blocked ports

B.

simple custom detections

C.

command and control

D.

allowed applications

E.

URL

Buy Now
Questions 154

Which two tasks allow NetFlow on a Cisco ASA 5500 Series firewall? (Choose two)

Options:

A.

Enable NetFlow Version 9.

B.

Create an ACL to allow UDP traffic on port 9996.

C.

Apply NetFlow Exporter to the outside interface in the inbound direction.

D.

Create a class map to match interesting traffic.

E.

Define a NetFlow collector by using the flow-export command

Buy Now
Questions 155

Which Talos reputation center allows you to track the reputation of IP addresses for email and web traffic?

Options:

A.

IP Blacklist Center

B.

File Reputation Center

C.

AMP Reputation Center

D.

IP and Domain Reputation Center

Buy Now
Questions 156

An engineer is trying to securely connect to a router and wants to prevent insecure algorithms from being used.

However, the connection is failing. Which action should be taken to accomplish this goal?

Options:

A.

Disable telnet using the no ip telnet command.

B.

Enable the SSH server using the ip ssh server command.

C.

Configure the port using the ip ssh port 22 command.

D.

Generate the RSA key using the crypto key generate rsa command.

Buy Now
Questions 157

An engineer needs to configure a Cisco Secure Email Gateway (SEG) to prompt users to enter multiple forms of identification before gaining access to the SEG. The SEG must also join a cluster using the preshared key of cisc421555367. What steps must be taken to support this?

Options:

A.

Enable two-factor authentication through a RADIUS server, and then join the cluster via the SEG GUI.

B.

Enable two-factor authentication through a TACACS+ server, and then join the cluster via the SEG CLI.

C.

Enable two-factor authentication through a RADIUS server, and then join the cluster via the SEG CLI

D.

Enable two-factor authentication through a TACACS+ server, and then join the cluster via the SEG GUI.

Buy Now
Questions 158

Why is it important to have a patching strategy for endpoints?

Options:

A.

to take advantage of new features released with patches

B.

so that functionality is increased on a faster scale when it is used

C.

so that known vulnerabilities are targeted and having a regular patch cycle reduces risks

D.

so that patching strategies can assist with disabling nonsecure protocols in applications

Buy Now
Questions 159

Which Cisco IOS XE command rejects packets with a source IP address that fails a reverse-path-forwarding prefix check on the ingress interface?

Options:

A.

ip verify unicast source reachable-via both

B.

ip verify unicast source reachable-via rx

C.

ip verify unicast source reachable-via tx

D.

ip verify unicast source reachable-via any

Buy Now
Questions 160

An engineer is configuring Cisco Umbrella and has an identity that references two different policies. Which action ensures that the policy that the identity must use takes precedence over the second one?

Options:

A.

Configure the default policy to redirect the requests to the correct policy

B.

Place the policy with the most-specific configuration last in the policy order

C.

Configure only the policy with the most recently changed timestamp

D.

Make the correct policy first in the policy order

Buy Now
Questions 161

Which CLI command is used to enable URL filtering support for shortened URLs on the Cisco ESA?

Options:

A.

webadvancedconfig

B.

websecurity advancedconfig

C.

outbreakconfig

D.

websecurity config

Buy Now
Questions 162

A university policy must allow open access to resources on the Internet for research, but internal workstations are exposed to malware. Which Cisco AMP feature allows the engineering team to determine whether a file is installed on a selected few workstations?

Options:

A.

file prevalence

B.

file discovery

C.

file conviction

D.

file manager

Buy Now
Questions 163

What is a feature of an endpoint detection and response solution?

Options:

A.

Preventing attacks by identifying harmful events with machine learning and conduct-based defense

B.

Rapidly and consistently observing and examining data to mitigate threats

C.

Capturing and clarifying data on email, endpoints, and servers to mitigate threats

D.

Ensuring the security of network devices by choosing which devices are allowed to reach the network

Buy Now
Questions 164

An organization wants to secure users, data, and applications in the cloud. The solution must be API-based and

operate as a cloud-native CASB. Which solution must be used for this implementation?

Options:

A.

Cisco Cloudlock

B.

Cisco Cloud Email Security

C.

Cisco Firepower Next-Generation Firewall

D.

Cisco Umbrella

Buy Now
Questions 165

What do tools like Jenkins, Octopus Deploy, and Azure DevOps provide in terms of application and

infrastructure automation?

Options:

A.

continuous integration and continuous deployment

B.

cloud application security broker

C.

compile-time instrumentation

D.

container orchestration

Buy Now
Questions 166

Which two authentication protocols are supported by the Cisco WSA? (Choose two.)

Options:

A.

WCCP

B.

NTLM

C.

TLS

D.

SSL

E.

LDAP

Buy Now
Questions 167

Which system facilitates deploying microsegmentation and multi-tenancy services with a policy-based container?

Options:

A.

SDLC

B.

Docker

C.

Lambda

D.

Contiv

Buy Now
Questions 168

Which two features are used to configure Cisco ESA with a multilayer approach to fight viruses and malware?

(Choose two)

Options:

A.

Sophos engine

B.

white list

C.

RAT

D.

outbreak filters

E.

DLP

Buy Now
Questions 169

Which security solution uses NetFlow to provide visibility across the network, data center, branch offices, and cloud?

Options:

A.

Cisco CTA

B.

Cisco Encrypted Traffic Analytics

C.

Cisco Umbrella

D.

Cisco Secure Network Analytics

Buy Now
Questions 170

A network administrator is using the Cisco ESA with AMP to upload files to the cloud for analysis. The network

is congested and is affecting communication. How will the Cisco ESA handle any files which need analysis?

Options:

A.

AMP calculates the SHA-256 fingerprint, caches it, and periodically attempts the upload.

B.

The file is queued for upload when connectivity is restored.

C.

The file upload is abandoned.

D.

The ESA immediately makes another attempt to upload the file.

Buy Now
Questions 171

Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)

Options:

A.

posture assessment

B.

aaa authorization exec default local

C.

tacacs-server host 10.1.1.250 key password

D.

aaa server radius dynamic-author

E.

CoA

Buy Now
Questions 172

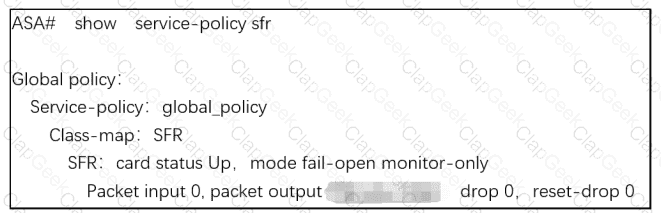
Refer to the exhibit.

What are two indications of the Cisco Firepower Services Module configuration?

(Choose two.)

Options:

A.

The module is operating in IDS mode.

B.

Traffic is blocked if the module fails.

C.

The module fails to receive redirected traffic.

D.

The module is operating in IPS mode.

E.

Traffic continues to flow if the module fails.

Buy Now
Questions 173

Refer to the exhibit.

A newly installed stack of Cisco Catalyst switches has been integrated with Cisco ISE for 802.1X port control and downloadable access control list (dACL) enforcement. Test workstations authenticate successfully, but the expected dACL never appears in the port configuration, leaving all traffic unrestricted. Packet captures confirm that Cisco ISE transmits the correct attributes, yet the switches classify them as “unknown” and ignore the instructions. A review of the running configuration shows complete AAA and 802.1X configuration. Which configuration command must be added to resolve the issue?

Options:

A.

radius-server vsa send accounting

B.

aaa authorization network default group radius

C.

radius-server vsa send authentication

D.

aaa authorization exec default group radius

Buy Now
Questions 174

An engineer used a posture check on a Microsoft Windows endpoint and discovered that the MS17-010 patch

was not installed, which left the endpoint vulnerable to WannaCry ransomware. Which two solutions mitigate

the risk of this ransom ware infection? (Choose two)

Options:

A.

Configure a posture policy in Cisco Identity Services Engine to install the MS17-010 patch before allowingaccess on the network.

B.

Set up a profiling policy in Cisco Identity Service Engine to check and endpoint patch level before allowingaccess on the network.

C.

Configure a posture policy in Cisco Identity Services Engine to check that an endpoint patch level is metbefore allowing access on the network.

D.

Configure endpoint firewall policies to stop the exploit traffic from being allowed to run and replicatethroughout the network.

E.

Set up a well-defined endpoint patching strategy to ensure that endpoints have critical vulnerabilities patched in a timely fashion.

Buy Now
Questions 175

Which OWASP LLM risk involves an attacker embedding hidden instructions in user input to manipulate the model’s behavior?

Options:

A.

Output Truncation

B.

Prompt Injection

C.

System Prompt Leakage

D.

Data Exfiltration

Buy Now
Questions 176

What is the intent of a basic SYN flood attack?

Options:

A.

to solicit DNS responses

B.

to exceed the threshold limit of the connection queue

C.

to flush the register stack to re-initiate the buffers

D.

to cause the buffer to overflow

Buy Now
Questions 177

Which two products are used to forecast capacity needs accurately in real time? (Choose two.)

Options:

A.

Cisco Secure Workload

B.

Cisco Umbrella

C.

Cisco Workload Optimization Manager

D.

Cisco AppDynamics

E.

Cisco Cloudlock

Buy Now
Questions 178

Which two activities can be done using Cisco DNA Center? (Choose two)

Options:

A.

DHCP

B.

Design

C.

Accounting

D.

DNS

E.

Provision

Buy Now
Questions 179

Which feature is used to restrict communication between interfaces on a Cisco ASA?

Options:

A.

VLAN subinterfaces

B.

Traffic zones

C.

Security levels

D.

VxLAN interfaces

Buy Now
Questions 180

Which type of encryption uses a public key and private key?

Options:

A.

Asymmetric

B.

Symmetric

C.

Linear

D.

Nonlinear

Buy Now
Questions 181

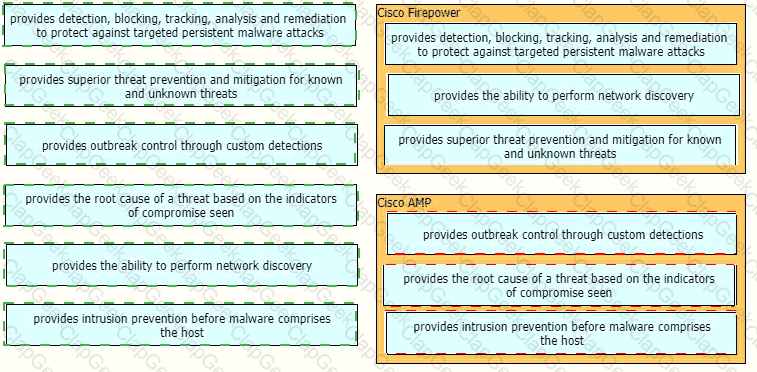
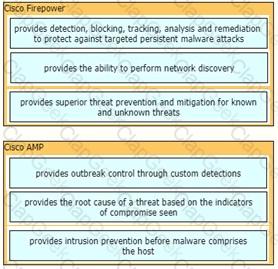
Drag and drop the capabilities of Cisco Firepower versus Cisco AMP from the left into the appropriate category on the right.
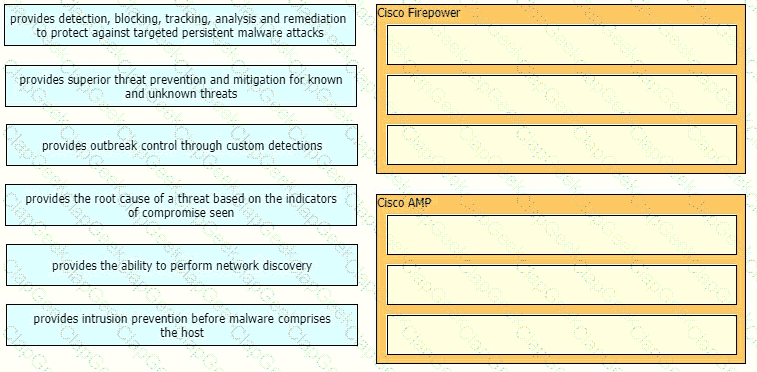
Options:

Buy Now
Questions 182

How does Cisco Umbrella protect clients when they operate outside of the corporate network?

Options:

A.

by modifying the registry for DNS lookups

B.

by using Active Directory group policies to enforce Cisco Umbrella DNS servers

C.

by using the Cisco Umbrella roaming client

D.

by forcing DNS queries to the corporate name servers

Buy Now
Questions 183

What Cisco command shows you the status of an 802.1X connection on interface gi0/1?

Options:

A.

show authorization status

B.

show authen sess int gi0/1

C.

show connection status gi0/1

D.

show ver gi0/1

Buy Now
Questions 184

A security administrator is designing an email protection solution for an onsite email server and must meet these requirements:

Remove malware from email before it reaches corporate premises

Drop emails with risky links automatically

Block access to newly infected sites with real-time URL analysis

Which solution must be used?

Options:

A.

Cisco Secure Email Cloud

B.

Cisco Security for Office 365

C.

Cisco Stealthwatch Cloud

D.

Cisco Secure Email and Web Manager Cloud

Buy Now
Questions 185

What is a benefit of flexible NetFlow records?

Options:

A.

They are used for security

B.

They are used for accounting

C.

They monitor a packet from Layer 2 to Layer 5

D.

They have customized traffic identification

Buy Now
Questions 186

A network engineer entered the snmp-server user asmith myv7 auth sha cisco priv aes 256

cisc0xxxxxxxxx command and needs to send SNMP information to a host at 10.255.255.1. Which

command achieves this goal?

Options:

A.

snmp-server host inside 10.255.255.1 version 3 myv7

B.

snmp-server host inside 10.255.255.1 snmpv3 myv7

C.

snmp-server host inside 10.255.255.1 version 3 asmith

D.

snmp-server host inside 10.255.255.1 snmpv3 asmith

Buy Now
Questions 187

An administrator configures a new destination list in Cisco Umbrella so that the organization can block specific domains for its devices. What should be done to ensure that all subdomains of domain.com are blocked?

Options:

A.

Configure the *.com address in the block list.

B.

Configure the *.domain.com address in the block list

C.

Configure the *.domain.com address in the block list

D.

Configure the domain.com address in the block list

Buy Now
Questions 188

A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:

    Matching IKEv2 proposals, preshared keys, and IPsec transform sets

    Access control rules permitting the traffic

    Crypto maps applied to the outside interfaces

    VPN traffic exempted from inspection

During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?

Options:

A.

Configure NAT exemption for traffic between the interesting subnet pairs.

B.

Create a tunnel group with preshared-key authentication under connection profiles.

C.

Enable IKEv2 fragmentation on both peers to reduce packet size.

D.

Attach the new VPN policy to the global prefilter default action.

Buy Now
Questions 189

In which two customer environments is the Cisco Secure Web Appliance Virtual connector traffic direction method selected? (Choose two.)

Options:

A.

Customer needs to support roaming users.

B.

Customer does not own Cisco hardware and needs Transparent Redirection (WCCP).

C.

Customer owns ASA Appliance and Virtual Form Factor is required.

D.

Customer does not own Cisco hardware and needs Explicit Proxy.

E.

Customer owns ASA Appliance and SSL Tunneling is required.

Buy Now
Questions 190

Which two activities are performed using Cisco Catalyst Center? (Choose two.)

Options:

A.

DHCP

B.

Design

C.

Provision

D.

DNS

E.

Accounting

Buy Now
Questions 191

What is a language format designed to exchange threat intelligence that can be transported over the TAXII

protocol?

Options:

A.

STIX

B.

XMPP

C.

pxGrid

D.

SMTP

Buy Now
Questions 192

Which kind of API that is used with Cisco DNA Center provisions SSIDs, QoS policies, and update software versions on switches?

Options:

A.

Integration

B.

Intent

C.

Event

D.

Multivendor

Buy Now
Questions 193

What are two things to consider when using PAC files with the Cisco WSA? (Choose two.)
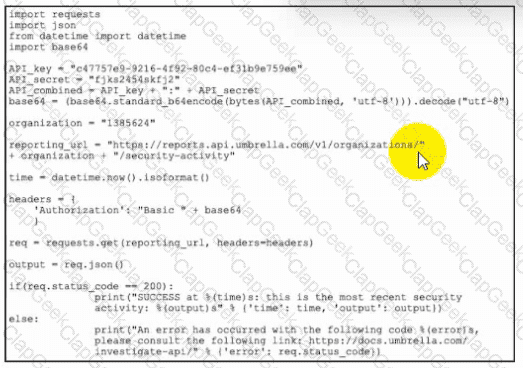
Options:

A.

If the WSA host port is changed, the default port redirects web traffic to the correct port automatically.

B.

PAC files use if-else statements to determine whether to use a proxy or a direct connection for traffic between the PC and the host.

C.

The WSA hosts PAC files on port 9001 by default.

D.

The WSA hosts PAC files on port 6001 by default.

E.

By default, they direct traffic through a proxy when the PC and the host are on the same subnet.

Buy Now
Questions 194

What must be used to share data between multiple security products?

Options:

A.

Cisco Rapid Threat Containment

B.

Cisco Platform Exchange Grid

C.

Cisco Advanced Malware Protection

D.

Cisco Stealthwatch Cloud

Buy Now
Questions 195

Refer to the exhibit. Which task is the Python script performing by using the Cisco Umbrella API?

Options:

A.

Creating a list of the latest security events

B.

Copying a list of the latest security activity

C.

Retrieving a list of the latest security events

D.

Sending a list of the latest security activity

Buy Now
Questions 196

A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256

cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?

Options:

A.

snmp-server host inside 10.255.254.1 version 3 andy

B.

snmp-server host inside 10.255.254.1 version 3 myv3

C.

snmp-server host inside 10.255.254.1 snmpv3 andy

D.

snmp-server host inside 10.255.254.1 snmpv3 myv3

Buy Now
Questions 197

What is a difference between weak passwords and missing encryption?

Options:

A.

Weak passwords allow programs to be renamed, and missing encryption hides .exe extensions.

B.

Weak passwords cause programs to crash, and missing encryption sends data to a memory location.

C.

Weak passwords consume bandwidth, and missing encryption allows user information to be hijacked.

D.

Weak passwords are guessed easily, and missing encryption allows information to be decrypted.

Buy Now
Questions 198

II

An engineer musí set up 200 new laptops on a network and wants to prevent the users from moving their laptops around to simplify administration Which switch port MAC address security setting must be used?

Options:

A.

sticky

B.

static

C.

aging

D.

maximum

Buy Now
Questions 199

For which two conditions can an endpoint be checked using ISE posture assessment? (Choose two)

Options:

A.

Windows service

B.

computer identity

C.

user identity

D.

Windows firewall

E.

default browser

Buy Now
Questions 200

Drag and drop the descriptions from the left onto the correct protocol versions on the right.
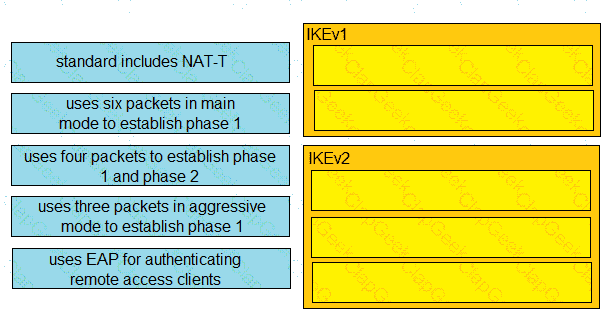
Options:

Buy Now
Questions 201

What are two differences between a Cisco WSA that is running in transparent mode and one running in explicit mode? (Choose two)

Options:

A.

The Cisco WSA responds with its own IP address only if it is running in explicit mode.

B.

The Cisco WSA is configured in a web browser only if it is running in transparent mode.

C.

The Cisco WSA responds with its own IP address only if it is running in transparent mode.

D.

The Cisco WSA uses a Layer 3 device to redirect traffic only if it is running in transparent mode.

E.

When the Cisco WSA is running in transparent mode, it uses the WSA ' s own IP address as the HTTP request destination.

Buy Now
Questions 202

A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT” and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?

Options:

A.

EDR

B.

CASB

C.

Secure Firewall

D.

CWPP

Buy Now
Questions 203

Which DevSecOps implementation process gives a weekly or daily update instead of monthly or quarterly in the applications?

Options:

A.

Orchestration

B.

CI/CD pipeline

C.

Container

D.

Security

Buy Now
Questions 204

Which Cisco platform onboards the endpoint and can issue a CA signed certificate while also automatically configuring endpoint network settings to use the signed endpoint certificate, allowing the endpoint to gain network access?

Options:

A.

Cisco ISE

B.

Cisco NAC

C.

Cisco TACACS+

D.

Cisco WSA

Buy Now
Questions 205

When network telemetry is implemented, what is important to be enabled across all network infrastructure devices to correlate different sources?

Options:

A.

CDP

B.

NTP

C.

syslog

D.

DNS

Buy Now
Questions 206

What is the recommendation in a zero-trust model before granting access to corporate applications and

resources?

Options:

A.

to use multifactor authentication

B.

to use strong passwords

C.

to use a wired network, not wireless

D.

to disconnect from the network when inactive

Buy Now
Questions 207

What causes alert fatigue in Cisco XDR?

Options:

A.

Alerts lacking sufficient context to be accurate

B.

Reauthentication of an active endpoint during a vulnerability incident

C.

Notifications from too few devices in a data-breach event

D.

Automatic policy enforcement during a suspicious event

Buy Now
Questions 208

An organization uses Cisco FMC to centrally manage multiple Cisco FTD devices. The default management

port conflicts with other communications on the network and must be changed. What must be done to ensure

that all devices can communicate together?

Options:

A.

Manually change the management port on Cisco FMC and all managed Cisco FTD devices

B.

Set the tunnel to go through the Cisco FTD

C.

Change the management port on Cisco FMC so that it pushes the change to all managed Cisco FTDdevices

D.

Set the tunnel port to 8305

Buy Now
Questions 209

Which Cisco WSA feature supports access control using URL categories?

Options:

A.

transparent user identification

B.

SOCKS proxy services

C.

web usage controls

D.

user session restrictions

Buy Now
Questions 210

Refer to the exhibit.

A security engineer is publishing a public web server located in the DMZ of a Cisco Secure Firewall Threat Defense device managed by Cisco Secure Firewall Management Center. The required network objects, Webserver_Private and Webserver_Public, are already defined, and an Auto NAT static rule mapping the public address to the private DMZ address is in place. The web server must be reachable from any source on the Internet. The engineer must configure a new Access Control Rule within the existing Access Control Policy. Which two configuration actions must be performed to meet the requirements? (Choose two.)

Options:

A.

Add DMZ as the Source Zone and Outside as the Destination Zone.

B.

Add Webserver_Private as the Source Network and Webserver_Public as the Destination Network.

C.

Add Any as the Source Network and Webserver_Private as the Destination Network.

D.

Add Any as the Source Network and Webserver_Public as the Destination Network.

E.

Add Outside as the Source Zone and DMZ as the Destination Zone.

Buy Now
Questions 211

Which Cisco Secure Endpoint feature tracks the propagation and execution path of a malicious file across the environment?

Options:

A.

Exclusion Lists

B.

Device Flow Correlation

C.

Incident Manager

D.

File Trajectory

Buy Now
Questions 212

Drag and drop the capabilities from the left onto the correct technologies on the right.
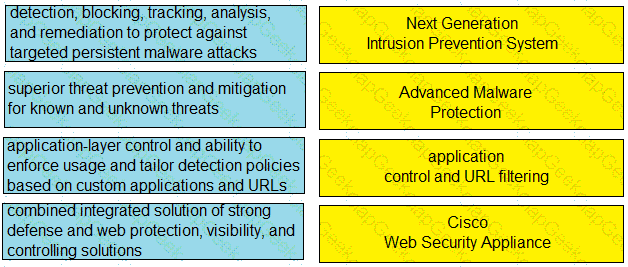
Options:

Buy Now
Questions 213

Which IETF attribute is supported for the RADIUS CoA feature?

Options:

A.

24 State

B.

30 Calling-Station-ID

C.

42 Acct-Session-ID

D.

81 Message-Authenticator

Buy Now
Questions 214

Which type of DNS abuse exchanges data between two computers even when there is no direct connection?

Options:

A.

Malware installation

B.

Command-and-control communication

C.

Network footprinting

D.

Data exfiltration

Buy Now
Questions 215

Which flaw does an attacker leverage when exploiting SQL injection vulnerabilities?

Options:

A.

user input validation in a web page or web application

B.

Linux and Windows operating systems

C.

database

D.

web page images

Buy Now
Questions 216

A networking team must harden an organization ' s network from VLAN hopping attacks. The team disables Dynamic Trunking Protocol and puts any unused ports in an unused VLAN. A trunk port is used as a trunk link. What must the team configure next to harden the network against VLAN hopping attacks?

Options:

A.

disable STP on the network devices

B.

dedicated VLAN ID for all trunk ports

C.

DHCP snooping on all the switches

D.

enable port-based network access control

Buy Now
Questions 217

Refer to the exhibit,

which command results in these messages when attempting to troubleshoot an iPsec VPN connection?

Options:

A.

debug crypto isakmp

B.

debug crypto ipsec endpoint

C.

debug crypto Ipsec

D.

debug crypto isakmp connection

Buy Now
Questions 218

What is a benefit of using Cisco Umbrella?

Options:

A.

DNS queries are resolved faster.

B.

Attacks can be mitigated before the application connection occurs.

C.

Files are scanned for viruses before they are allowed to run.

D.

It prevents malicious inbound traffic.

Buy Now
Questions 219

Drag and drop the security solutions from the left onto the benefits they provide on the right.
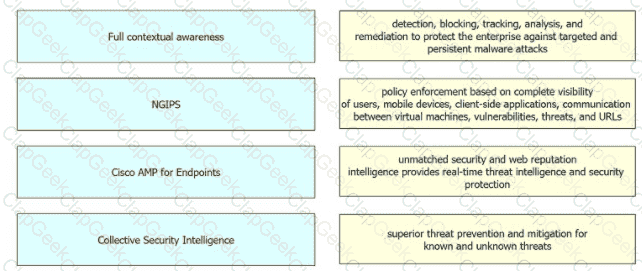
Options:

Buy Now
Questions 220

What is the purpose of threat intelligence in the Cisco Security Reference Architecture?

Options:

A.

To assist with threat monitoring and incident response

B.

To manage access control and authentication mechanisms

C.

To analyze network traffic and identify potential vulnerabilities

D.

To ensure compliance with industry regulations

Buy Now
Questions 221

Which solution should be leveraged for secure access of a CI/CD pipeline?

Options:

A.

Duo Network Gateway

B.

remote access client

C.

SSL WebVPN

D.

Cisco FTD network gateway

Buy Now
Questions 222

A network engineer must configure a Cisco Secure Email Gateway to prompt users to enter two forms of information before gaining access. The Secure Email Gateway must also join a cluster machine using preshared keys. What must be configured to meet these requirements?

Options:

A.

Enable two-factor authentication through a RADIUS server and then join the cluster by using the Secure Email Gateway CLI.

B.

Enable two-factor authentication through a TACACS+ server and then join the cluster by using the Secure Email Gateway CLI.

C.

Enable two-factor authentication through a RADIUS server and then join the cluster by using the Secure Email Gateway GUI.

D.

Enable two-factor authentication through a TACACS+ server and then join the cluster by using the Secure Email Gateway GUI.

Buy Now
Questions 223

A network engineer must monitor user and device behavior within the on-premises network. This data must be sent to the Cisco Stealthwatch Cloud analytics platform for analysis. What must be done to meet this

requirement using the Ubuntu-based VM appliance deployed in a VMware-based hypervisor?

Options:

A.

Configure a Cisco FMC to send syslogs to Cisco Stealthwatch Cloud

B.

Deploy the Cisco Stealthwatch Cloud PNM sensor that sends data to Cisco Stealthwatch Cloud

C.

Deploy a Cisco FTD sensor to send network events to Cisco Stealthwatch Cloud

D.

Configure a Cisco FMC to send NetFlow to Cisco Stealthwatch Cloud

Buy Now
Questions 224

An administrator is configuring N I P on Cisco ASA via ASDM and needs to ensure that rogue NTP servers cannot insert themselves as the authoritative time source Which two steps must be taken to accomplish this task? (Choose two)

Options:

A.

Specify the NTP version

B.

Configure the NTP stratum

C.

Set the authentication key

D.

Choose the interface for syncing to the NTP server

E.

Set the NTP DNS hostname

Buy Now
Questions 225

Under which two circumstances is a CoA issued? (Choose two)

Options:

A.

A new authentication rule was added to the policy on the Policy Service node.

B.

An endpoint is deleted on the Identity Service Engine server.

C.

A new Identity Source Sequence is created and referenced in the authentication policy.

D.

An endpoint is profiled for the first time.

E.

A new Identity Service Engine server is added to the deployment with the Administration persona

Buy Now
Questions 226

What are two workloaded security models? (Choose two)

Options:

A.

SaaS

B.

IaaS

C.

on-premises

D.

off-premises

E.

PaaS

Buy Now
Questions 227

A security administrator must implement a network intrusion policy in Cisco Secure Firewall to block new potential threats without sacrificing network performance. The administrator plans to create a base policy with a broad rule set optimized to protect the environment without significantly affecting throughput. Which type of policy should the administrator create?

Options:

A.

Maximum Detection

B.

Balanced Security and Connectivity

C.

Connectivity Over Security

D.

Security Over Connectivity

Buy Now
Questions 228

Cisco SensorBase gaihers threat information from a variety of Cisco products and services and performs analytics to find patterns on threats Which term describes this process?

Options:

A.

deployment

B.

consumption

C.

authoring

D.

sharing

Buy Now
Questions 229

A Cisco ESA network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Cisco ESA is not dropping files that have an undetermined verdict. What is causing this issue?

Options:

A.

The policy was created to send a message to quarantine instead of drop

B.

The file has a reputation score that is above the threshold

C.

The file has a reputation score that is below the threshold

D.

The policy was created to disable file analysis

Buy Now
Questions 230

Which Cisco DNA Center Intent API action is used to retrieve the number of devices known to a DNA Center?

Options:

A.

GET https://fqdnOrlPofDnaCenterPlatform/dna/intent/api/v1/network-device/count

B.

GET https://fqdnOrlPofDnaCenterPlatform/dna/intent/api/v1/network-device

C.

GET https://fqdnOrlPofDnaCenterPlatform/dna/intent/api/v1/networkdevice?parameter1=value & parameter2=value & ....

D.

GET https://fqdnOrlPofDnaCenterPlatform/dna/intent/api/v 1/networkdevice/startIndex/recordsToReturn

Buy Now
Questions 231

A network engineer is configuring NetFlow top talkers on a Cisco router Drag and drop the steps in the process from the left into the sequence on the right
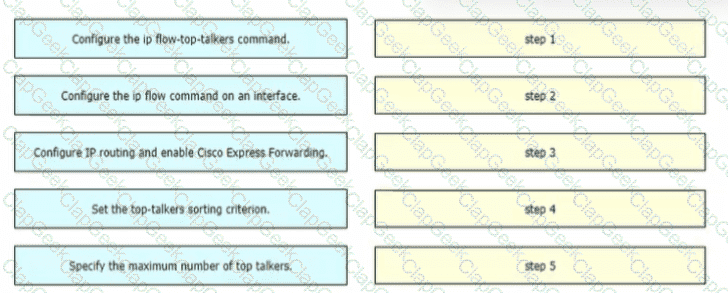
Options:

Buy Now
Questions 232

Which feature of Cisco ASA allows VPN users to be postured against Cisco ISE without requiring an inline

posture node?

Options:

A.

RADIUS Change of Authorization

B.

device tracking

C.

DHCP snooping

D.

VLAN hopping

Buy Now
Questions 233

Which two behavioral patterns characterize a ping of death attack? (Choose two)

Options:

A.

The attack is fragmented into groups of 16 octets before transmission.

B.

The attack is fragmented into groups of 8 octets before transmission.

C.

Short synchronized bursts of traffic are used to disrupt TCP connections.

D.

Malformed packets are used to crash systems.

E.

Publicly accessible DNS servers are typically used to execute the attack.

Buy Now
Questions 234

Which ESA implementation method segregates inbound and outbound email?

Options:

A.

one listener on a single physical Interface

B.

pair of logical listeners on a single physical interface with two unique logical IPv4 addresses and one IPv6 address

C.

pair of logical IPv4 listeners and a pair Of IPv6 listeners on two physically separate interfaces

D.

one listener on one logical IPv4 address on a single logical interface

Buy Now
Questions 235

Why would a user choose an on-premises ESA versus the CES solution?

Options:

A.

Sensitive data must remain onsite.

B.

Demand is unpredictable.

C.

The server team wants to outsource this service.

D.

ESA is deployed inline.

Buy Now
Questions 236

What is a prerequisite when integrating a Cisco ISE server and an AD domain?

Options:

A.

Place the Cisco ISE server and the AD server in the same subnet

B.

Configure a common administrator account

C.

Configure a common DNS server

D.

Synchronize the clocks of the Cisco ISE server and the AD server

Buy Now
Questions 237

Which Cisco ASA deployment model is used to filter traffic between hosts in the same IP subnet using higher-level protocols without readdressing the network?

Options:

A.

routed mode

B.

transparent mode

C.

single context mode

D.

multiple context mode

Buy Now
Questions 238

What is the purpose of a NetFlow version 9 template record?

Options:

A.

It specifies the data format of NetFlow processes.

B.

It provides a standardized set of information about an IP flow.

C.

lt defines the format of data records.

D.

It serves as a unique identification number to distinguish individual data records

Buy Now
Questions 239

An engineer is configuring Cisco Secure Endpoint to enhance security by preventing the execution of certain files by users. The engineer needs to ensure that the specific executable file name Cisco_Software_0505446151.exe is blocked from running while never being quarantined. What must the engineer configure to meet the requirement?

Options:

A.

Create advanced custom detection list.

B.

Configure application control blocked applications list.

C.

Implement simple custom detection list.

D.

Enable scheduled scans to detect and block the executable files.

Buy Now
Questions 240

Which feature of a secure CI/CD pipeline defends container workloads against detected exploits, application flaws, configuration errors, and policy violations?
Options:

A.

Control groups

B.

Separation of duties

C.

Runtime protection

D.

Cloud-native firewalling

Buy Now
Exam Code: 350-701
Exam Name: Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)
Last Update: Sep 13, 2026
Questions: 801
350-701 pdf

350-701 PDF

$23.75  $94.99
350-701 Engine

350-701 Testing Engine

$27.5  $109.99
350-701 PDF + Engine

350-701 PDF + Testing Engine

$36.25  $144.99