Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save75geek

NSE5_FSW_AD-7.6 Fortinet NSE 5 - FortiSwitch 7.6 Administrator Questions and Answers

Questions 4

To enhance service in emergency situations, to which LLDP-MED Type-Length-Values does Forti-Switch advertise to IP phones?

Options:

A.

Network policy

B.

Inventory management

C.

Location

D.

Power management

Buy Now
Questions 5

Exhibit.

port24 is the only uplink port connected to the network where access to FortiSwitch management services is possible. However, FortiSwitch is still not accessible on the management interface. Which two actions should you take to fix the issue and access FortiSwitch? (Choose two.)

Options:

A.

You must add port24 native VLAN as an allowed VLAN on internal.

B.

You must add VLAN ID 200 to the allowed VLANS on internal.

C.

You must allow VLAN ID 4094 on port24, if management traffic is tagged.

D.

You should use VLAN ID 4094 as the native VLAN on port24.

Buy Now
Questions 6

How does FortiGate handle configuration of flow tracking sampling if you export the settings to a managed FortiSwitch stack with sampling mode set to perimeter is true?

Options:

A.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces.

B.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces, except ICL and ISL interfaces.

C.

FortiGate configures and enables flow sampling on FortiSwitch but does not change existing sampling settings of interfaces.

D.

FortiGate configures and enables egress sampling on all management interfaces.

Buy Now
Questions 7

Exhibit.

The exhibit shows the current status of the ports on the managed FortiSwitch.

Access-1.

Why would FortiGate display a serial number in the Native VLAN column associated with the port23 entry?

Options:

A.

Port23 is a member of a trunk that uses the Access-1 FortiSwitch senal number as the name of the trunk.

B.

Port23 is configured as the dedicated management interface.

C.

A standalone switch with the showm serial number is connected on por123.

D.

Ports connect to adjacent FortiSwitch devices will show their.serial number as the na-tive VLAN

Buy Now
Questions 8

(Full question statement start from here)

What is one key advantage of using a sniffer profile on FortiSwitch compared to using the sniffer command? (Choose one answer)

Options:

A.

It allows packet capture on all switch ports without limitations.

B.

It eliminates the need to use access control lists (ACLs) or port mirroring for analysis.

C.

It automatically filters irrelevant traffic types.

D.

It automatically decrypts SSL/TLS traffic for full packet inspection.

Buy Now
Questions 9

You are designing a FortiSwitch backbone where every FortiSwitch device must connect to every other FortiSwitch for maximum redundancy. To maintain connectivity while preventing loops, which protocol or feature must you configure on the switches? (Choose one answer)

Options:

A.

Multichassis link aggregation group (MCLAG)

B.

Spanning Tree Protocol (STP)

C.

Full mesh high availability (HA)

D.

Link aggregation group (LAG)

Buy Now
Questions 10

Refer to the exhibit.

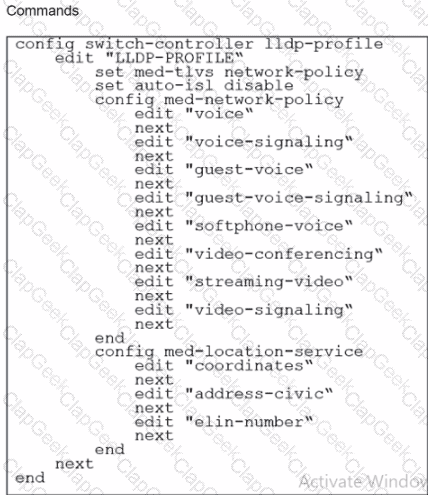
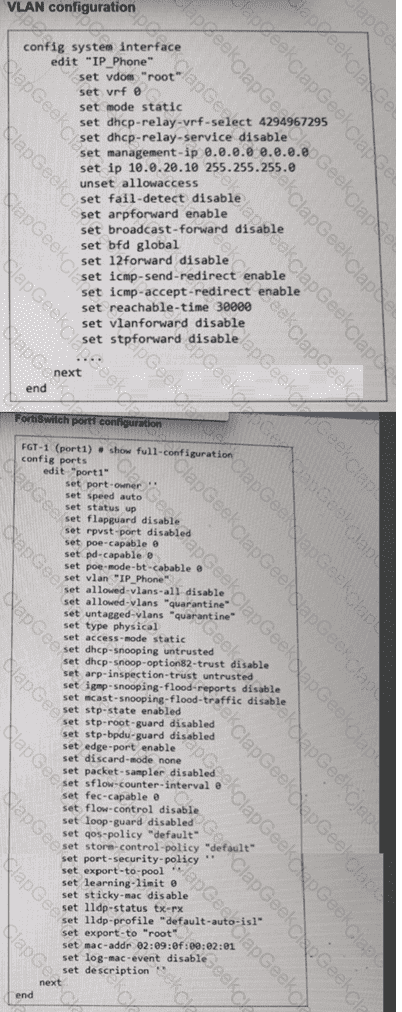
The profile shown in the exhibit is assigned to a group of managed FortiSwitch ports, and these ports are connected to endpoints which are powered by PoE.

Which configuration action can you perform on the LLDP profile to cause these endpoints to exchange PoE information and negotiate power with the managed FortiSwitch?

Options:

A.

Create new a LLDP-MED application type to define the PoE parameters.

B.

Assign a new LLDP profile to handle different LLDP-MED TLVs.

C.

Define an LLDP-MED location ID to use standard protocols for power.

D.

Add power management as part of LLDP-MED TLVs to advertise.

Buy Now
Questions 11

How does FortiSwitch perform actions on ingress and egress traffic using the access control list (ACL)?

Options:

A.

Only high-end FortiSwitch models support ACL.

B.

ACL can be used only at the prelookup stage in the traffic processing pipeline.

C.

Classifiers enable matching traffic based only on the VLAN ID.

D.

FortiSwitch checks ACL policies only from top to bottom.

Buy Now
Questions 12

Which two rules used by MSTP are similar to rules used by other STP methods? (Choose two.)

Options:

A.

MSTP uses port role election, similar to rapid STP on the instances.

B.

MSTP uses alternate path and primary path, similar to regular STP.

C.

MSTP uses root bridge selection, similar to rapid STP

D.

MSTP uses timers for transitioning the ports, similar to regular STP.

Buy Now
Questions 13

You are managing FortiSwitch ports from a FortiGate device with multiple VDOMs. Which two methods can you use to assign FortiSwitch ports to VDOMs? (Choose two answers)

Options:

A.

Assigning the port directly to a specific VDOM for dedicated physical isolation

B.

Use FortiGate policies to control inter-VDOM traffic for FortiSwitch ports

C.

Use interface role mapping to dynamically assign FortiSwitch ports to VDOMs based on Dynamic Host Configuration Protocol (DHCP) scope

D.

Using a virtual port pool (VPP) to create virtualized ports that can be assigned to different VDOMs

Buy Now
Questions 14

FortiGate is unable to establish a tunnel with the FortiSwitch device it is supposed to manage Based on the debug output shown in the exhibit, what is the reason for the failure?

Options:

A.

The handshake process timed out before FortiSwitch responded.

B.

DTLS client hello had the incorrect pre-shared key.

C.

The CAPWAP tunnel failed to come up due to a mismatch in time.

D.

FortiSwitch has disabled FortiLink and is only managed as a standalone.

Buy Now
Questions 15

Which interfaces on FortiSwitch send out FortiLink discovery frames by default in order to detect a FortiGate with an enabled FortiLink interface?

Options:

A.

All ports have auto-discovery enabled by default.

B.

No ports are enabled by default for auto-discovery. This must be configured under config switch interface.

C.

The ports with auto-discovery enabled by default are dependent upon the FortiSwitch model.

D.

The last four switch ports on FortiSwitch have auto-discovery enabled by default.

Buy Now
Questions 16

Which two statements about DHCP snooping enabled on a FortiSwitch VLAN are true? (Choose two.)

Options:

A.

Enabling DHCP snooping on a FortiSwitch VLAN ensures requests and replies are seen by all DHCP servers.

B.

switch-controller-dhcp-snooping-verify-mac verifies the destination MAC address to protect against DHCP exhaustion attacks.

C.

By default, all FortiSwitch ports are set to forward client DHCP requests to untrusted ports.

D.

Settings related to DHCP option 82 are only configurable through the CLI

Buy Now
Questions 17

Which statement about the IGMP snooping querier when enabled on a VLAN is true?

Options:

A.

Active multicast receiver entries are aging on each IGMP query sent on the VLAN

B.

IGMP reports on the VLAN are forwarded to all switch ports.

C.

The setting can only be enabled using the FortiSwitch CLI.

D.

All other indirectly connected switches will be unable to get IGMP multicast traffic.

Buy Now
Questions 18

Which statement about 802.1X security profiles using MAC-based authentication mode is true?

Options:

A.

FortiSwitch allows connectivity to all hosts connected to a port, if one host is authenticated.

B.

FortiSwitch can grant each device a different access level based on the credentials provided

C.

FortiSwitch performs faster when using this security mode on the ports.

D.

FortiSwitch must communicate with the RADIUS server to authenticate devices

Buy Now
Questions 19

In which two ways can you assign a FortiSwitch port to a VDOM using multi-tenancy setup? (Choose two.)

Options:

A.

Switch the FortiLink interface to the target VDOM.

B.

Remove the managed FortiSwitch and allocate ports directly on FortiSwitch.

C.

Create a virtual port pool on the FortiGate CLI.

D.

Assign a port to a VDOM directly on the managed FortiSwitch.

Buy Now
Questions 20

Which LLDP-MED Type-Length-Values does FortiSwitch collect from endpoints to track network devices and determine their characteristics?

Options:

A.

Network policy

B.

Power management

C.

Location

D.

Inventory management

Buy Now
Questions 21

You are configuring VLANs on a FortiSwitch device managed by FortiGate. Which two statements accurately describe VLAN assignment requirements and behavior on FortiSwitch ports? (Choose two answers)

Options:

A.

Untagged defines the list of VLANs that are allowed on the port for both ingress and egress traffic.

B.

Untagged VLAN applies to egress traffic only.

C.

You can assign only one native VLAN on a port.

D.

VLAN assignments must be configured directly on the FortiSwitch.

Buy Now
Questions 22

Which statement about the quarantine VLAN on FortiSwitch is true?

Options:

A.

Quarantine VLAN has no DHCP server

B.

Users who fail 802.1X authentication can be placed on the quarantine VLAN.

C.

It is only used for quarantined devices if global setting is set to quarantine by VLAN.

D.

FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.

Buy Now
Questions 23

Which two statements about the FortiLink authorization process are true? (Choose two.)

Options:

A.

The administrator must manually pre-authorize FortiGate on FortiSwitch by adding the FortiGate serial number.

B.

FortiSwitch requires a reboot to complete the authorization process.

C.

A FortiLink frame is sent by FortiGate to FortiSwitch to complete the authorization.

D.

FortiLink authorization sets the FortiSwitch management mode to FortiLink.

Buy Now
Questions 24

You need to mirror traffic from a source port on Switch A to a monitoring device on Switch C. For that purpose, you’re configuring Remote Switched Port Analyzer (RSPAN).1Due to the nature of RSPAN, what is the best practice when setting it up? (Choose one answer)

Options:

A.

Use the same VLAN already configured for regular data traffic.

B.

Use a dedicated VLAN assigned only to monitoring devices.

C.

Use a dynamic VLAN that includes all switch ports.

D.

Use the RSPAN VLAN as a native VLAN on all trunk ports.

Buy Now
Questions 25

Which two statements about VLAN assignments on FortiSwitch ports are true? (Choose two.)

Options:

A.

Configure a native VLAN on the FortiLink

B.

Assign an IP address and subnet mask to FortiSwitch VLANs

C.

Only assign one native VLAN on a port

D.

Assign untagged VLANs using FortiGate CLI

Buy Now
Questions 26

When Dynamic Host Configuration Protocol (DHCP) snooping is enabled on a FortiSwitch VLAN, which two statements are true? (Choose two answers)

Options:

A.

DHCP replies are accepted only on trusted ports.

B.

DHCP snooping blocks all unicast traffic.

C.

Option 82 can be inserted into DHCP requests.

D.

DHCP requests are dropped if sent from trusted ports.

Buy Now
Questions 27

Which is a requirement to enable SNMP v2c on a managed FortiSwitch?

Options:

A.

Create an SNMP user to use for authentication and encryption.

B.

Specify an SNMP host to send traps to.

C.

Enable an SNMP v3 to handle traps messages with SNMP hosts.

D.

Configure SNMP agent and communities.

Buy Now
Questions 28

Which statement about using MAC, IP, and protocol-based VLANs on FortiSwitch is true?

Options:

A.

lt is a scalable and secure solution in comparison to other Layer 2 security measures.

B.

FortiSwitch uses only the Ethernet type to assign traffic to VLANs.

C.

It provides benefits that can be obtained when using 802.1X authentication.

D.

Endpoints are required to use the same FortiSwitch port to remain members of the VLAN.

Buy Now
Questions 29

Refer to the configuration:

Which two conditions does FortiSwitch need to meet to successfully configure the options shown in the exhibit above? (Choose two.)

Options:

A.

The FortiSwitch model is equipped with a maximum of 54 interfaces

B.

FortiSwitch would need to be rebooted.

C.

The split port can be assigned to a native VLAN.

D.

The Dort full speed prior to the split was 100G QSFP+.

Buy Now
Questions 30

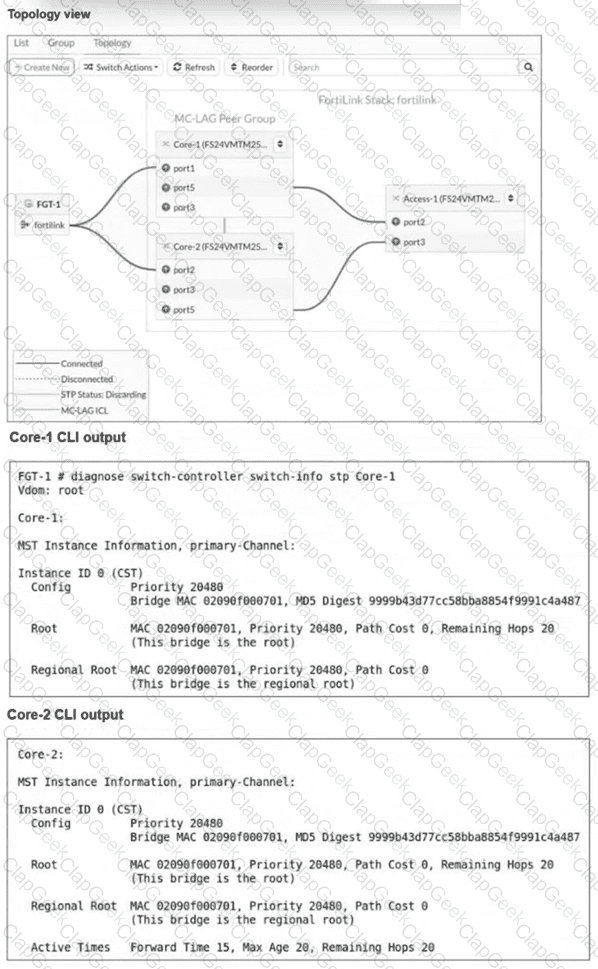
Refer to the exhibits.

An administrator has deployed two FortiSwitch devices, Core-1 and Core-2, as multichassis link aggregation group (MCLAG) peers. These switches are connected to FortiGate for FortiLink and to an access switch (Access-1) using an inter-switch link (ISL). After configuration, the administrator notices that both Core-1 and Core-2 are claiming to be the root bridge in the Multiple Spanning Tree Protocol (MSTP) topology. What explains this behavior? (Choose one answer)

Options:

A.

FortiGate participates in MSTP and causes both switches to assume the root bridge role.

B.

The ISL was not configured correctly, leading to MSTP inconsistency.

C.

Both switches share the same bridge ID because MCLAG treats them as one logical switch.

D.

MCLAG automatically disables STP on all peer switches.

Buy Now
Questions 31

Which packet capture method allows FortiSwitch to capture traffic on trunks and management interfaces?

Options:

A.

SPAN

B.

Sniffer profile

C.

sFlow

D.

TCP dump

Buy Now
Questions 32

What happens when a routed VLAN interface (RVI) is configured on a FortiSwitch port or trunk? (Choose one answer)

Options:

A.

VLAN 1 is automatically assigned for management.

B.

The port becomes a layer 3 interface with VLAN 4095 assigned automatically.1

C.

All VLANs on the port are terminated in a trunk by default.

D.

The port becomes a layer 3 interface and assigned to VLAN 1.

Buy Now
Questions 33

What type of multimode transceiver can be used to split a 40G port?

Options:

A.

QSFP+ transceiver

B.

SFP transceiver

C.

QSFP transceiver

D.

SFP+ transceiver

Buy Now
Questions 34

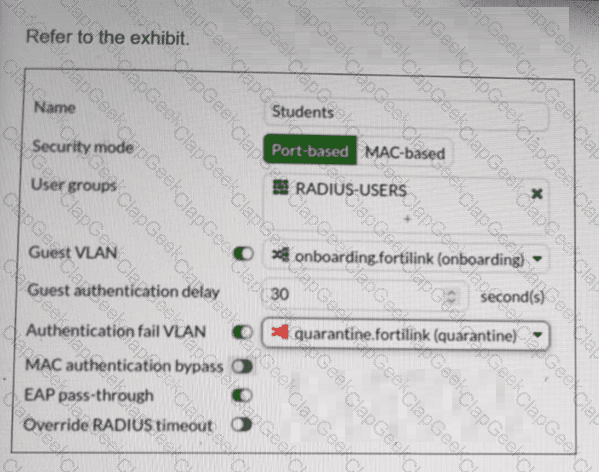
Refer to the exhibit.

FortiSwitch 802.1X port security configuration is shown. A user connects their laptop to the port and attempts to authenticate using 802.1X, but enters the wrong credentials multiple times. What will the result to the device be? (Choose one answer)
Options:

A.

The device will be placed into the VLAN quarantine.

B.

The port will shut down for security reasons.

C.

The device will be placed into the VLAN onboarding.

D.

The device will be assigned to the default management VLAN.

Buy Now
Exam Code: NSE5_FSW_AD-7.6
Exam Name: Fortinet NSE 5 - FortiSwitch 7.6 Administrator
Last Update: Sep 19, 2026
Questions: 114
NSE5_FSW_AD-7.6 pdf

NSE5_FSW_AD-7.6 PDF

$21.25  $84.99
NSE5_FSW_AD-7.6 Engine

NSE5_FSW_AD-7.6 Testing Engine

$25  $99.99
NSE5_FSW_AD-7.6 PDF + Engine

NSE5_FSW_AD-7.6 PDF + Testing Engine

$33.75  $134.99