Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save75geek

Network-Security-Essentials Network Security Essentials for Locally-Managed Fireboxes Questions and Answers

Questions 4

You enable a network device monitoring application on a server with IP address 10.0.1.22. After you run the application, it reports that it cannot ping the Firebox at 10.0.1.1, and you see this log message in Traffic Monitor. What is the most likely cause of this issue? (Select one.)

(Log: Deny 10.0.1.22 10.0.1.1 icmp/8 255-Unhandled Internal Packet-00)

Options:

A.

The server IP address is on the Blocked Sites list

B.

There is no route on the Firebox for the 10.0.1.0/24 subnet

C.

The dynamic NAT statement is not configured correctly for the 10.0.1.0/24 subnet

D.

The default Unhandled Internal Packet policy is at the top of the policy set

E.

There is no policy that allows Ping traffic from the server to the Firebox alias

Buy Now
Questions 5

You want to send traffic from the Internet to your internal web server through the Firebox. You see the traffic is allowed in Traffic Monitor, but the web server cannot be reached. You use the TCP Dump Diagnostic Task and collect this information from the Firebox interface connected to the web server. What could cause the problem? (Select two.)

Options:

A.

The web server has firewall software installed that blocks incoming connections

B.

The HTTPS proxy is blocking the connection because Gateway AntiVirus detected a virus

C.

The Firebox Dynamic NAT rules are configured incorrectly

D.

The IP address of the web server is on the Firebox Blocked Sites list

E.

The web server default gateway is configured incorrectly

Buy Now
Questions 6

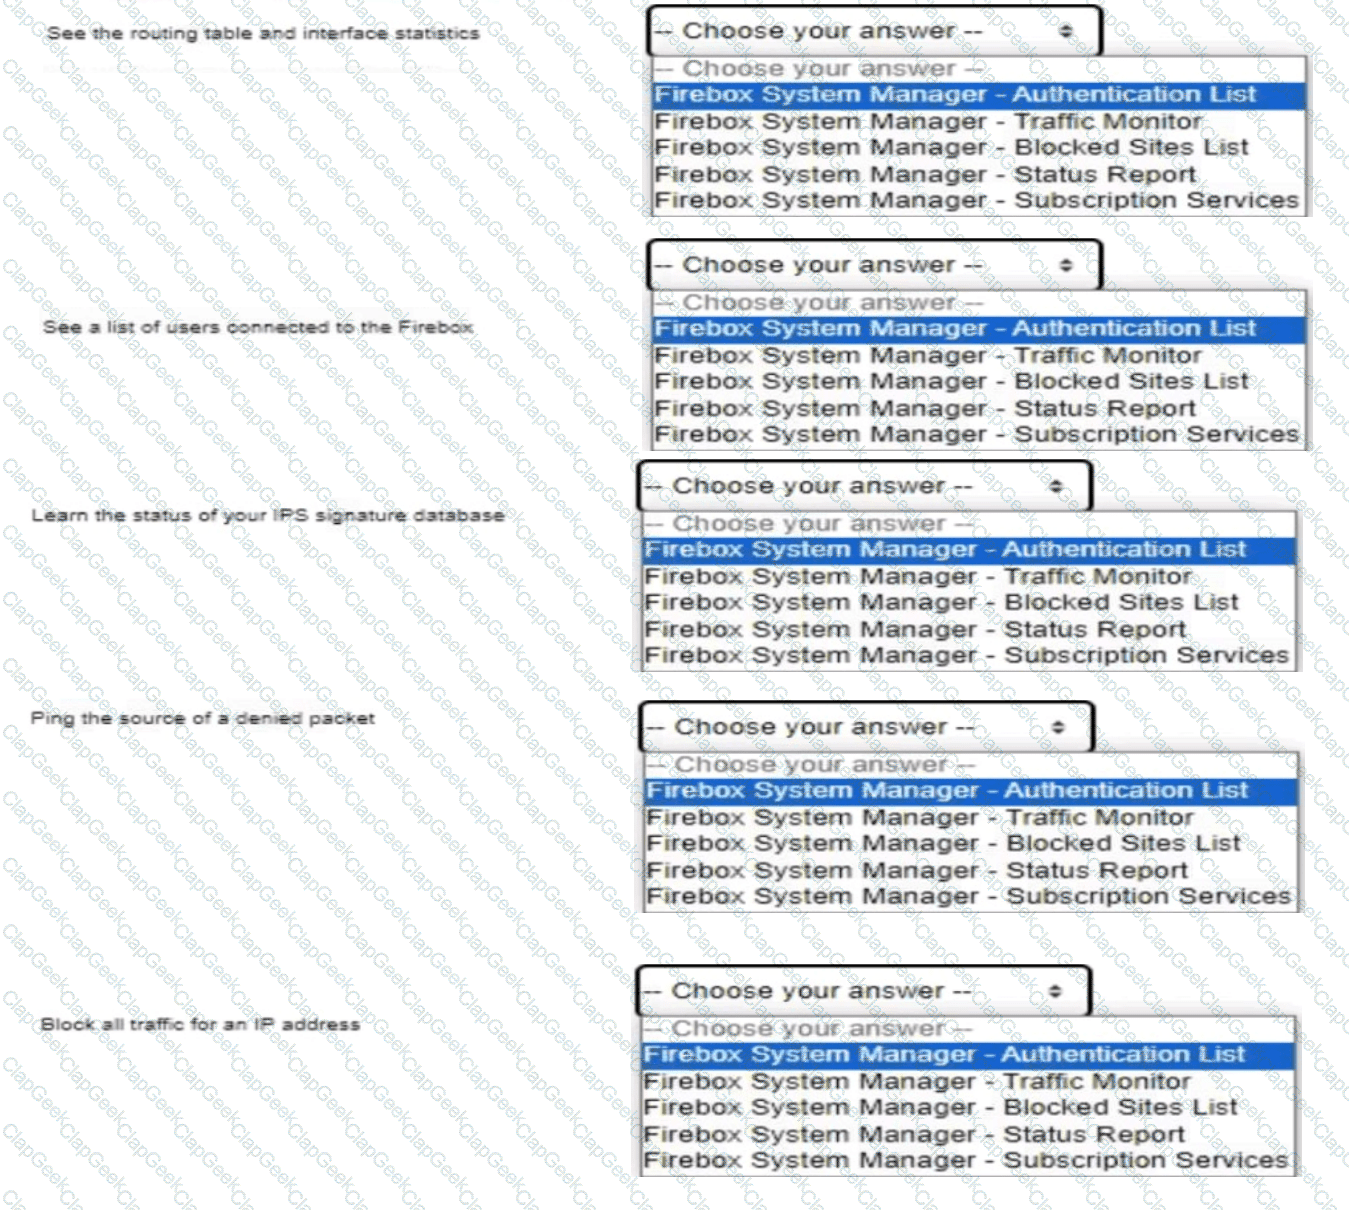
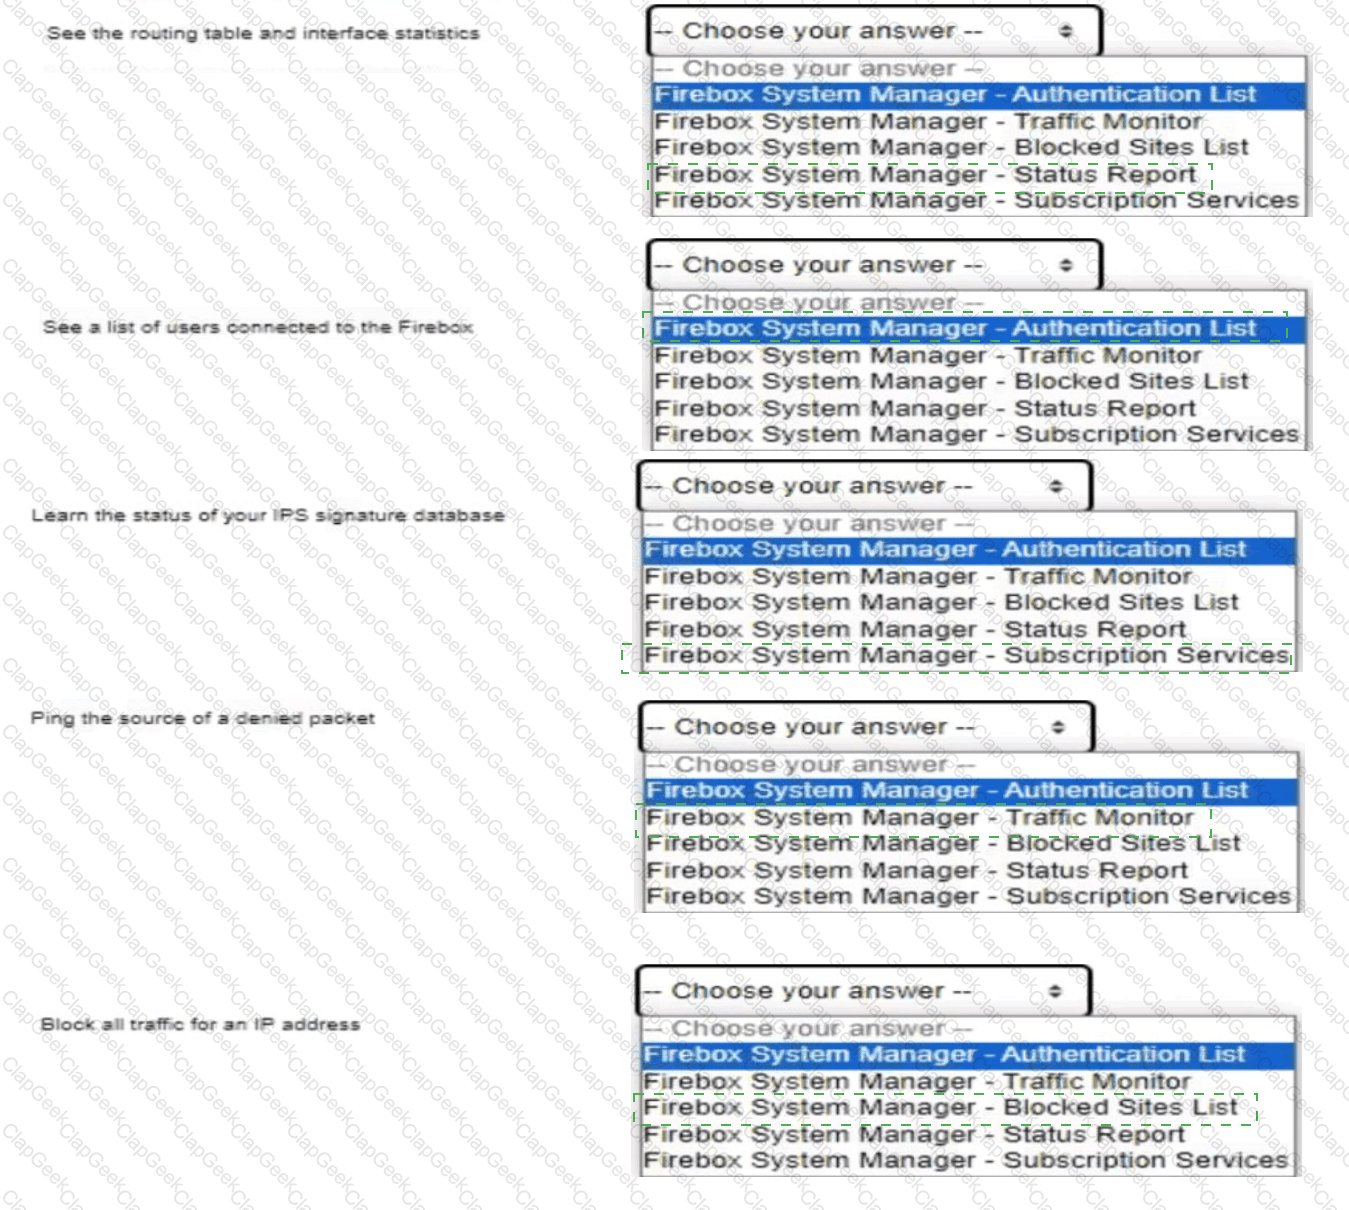
In Firebox System Manager, where can you perform each of these tasks?

Options:

Buy Now
Questions 7

The Firebox can scan the contents of encrypted zip files with Gateway AntiVirus when HTTPS content inspection is enabled.

Options:

A.

True

B.

False

Buy Now
Questions 8

Your network was the target of an attack last week. You want to learn more about the source of the attack. What monitoring tools can you use to get started? (Select one.)

Options:

A.

Traffic Monitor in Firebox System Manager

B.

FireWatch in Fireware Web UI

C.

Discovery in Fireware Web UI

D.

WatchGuard Log Catalog

E.

Log Search and reports in WatchGuard Cloud or Dimension

Buy Now
Questions 9

Which WatchGuard tools can you use to review the traffic log messages generated by your Firebox? (Select three.)

Options:

A.

FireWatch

B.

Policy Manager

C.

Traffic Monitor

D.

Dimension

E.

Status Report

F.

WatchGuard Cloud

Buy Now
Questions 10

When you migrate a configuration file from one Firebox to a new Firebox, which settings transfer to the new device? (Select two.)

Options:

A.

Management users

B.

Certificates

C.

Policies

D.

DNS servers

E.

Feature key

Buy Now
Questions 11

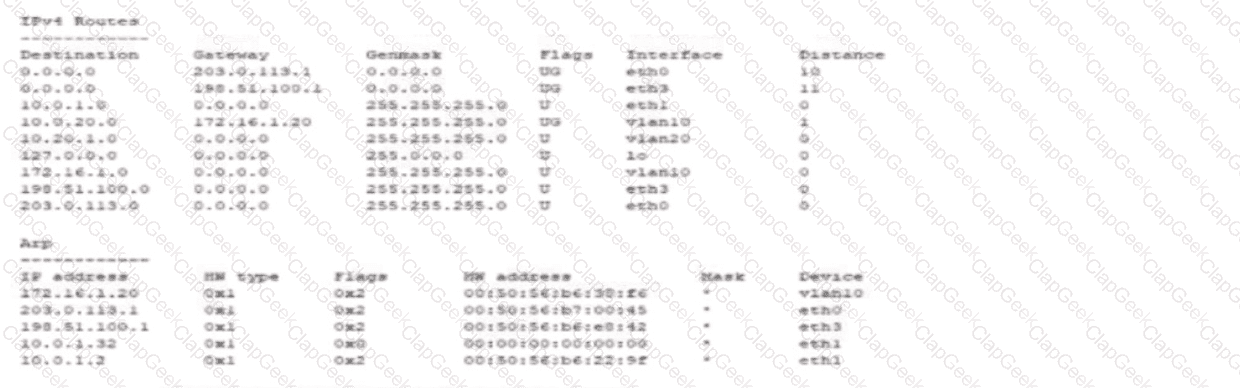
You configured your Firebox interfaces and routes and want to verify the status of the routes and connected hosts. You found this information in Firebox System Manager > Status Report. What is true about the IPv4 routes and ARP table in this deployment? (Select one.)
Options:

A.

The Firebox is publicly reachable at 198.51.100.1 through the eth0 interface

B.

10.0.20.53 can be reached through the vlan20 interface

C.

The MAC address for the default gateway that currently routes traffic is 00:50:56:b5:e5:42

D.

The MAC address for 172.16.1.20 is 00:50:56:b0:22:0f

E.

The Firebox cannot resolve a MAC address for 10.0.1.32

Buy Now
Questions 12

Your users have no network connectivity on their computers in the 10.0.40.0/24 network. You investigate and discover the DHCP address pool for this network is exhausted, but there are no available IP addresses in the network to assign. Which of these options can you use to expand the IP address space of this network? (Select two.)

Options:

A.

Change the IP address of the 10.0.40.1/24 network to 10.0.40.123/24

B.

Enable a wireless SSID for the 10.0.40.1/24 network

C.

Add 10.0.50.1/24 to the 10.0.40.1/24 network as a secondary network

D.

Create a Dynamic NAT rule for traffic from the 10.0.40.1/24 network going to the 10.0.50.1/24 network

E.

Bridge the 10.0.40.1/24 network across additional interfaces

Buy Now
Questions 13

You recently installed network monitoring software on your server and then performed a port scan for each IP address in the network. When the scan finishes, you notice that the server lost access to the Internet. What is the most likely cause of this issue? (Select one.)

Options:

A.

The server IP address was added to the Blocked Sites list because of the default packet handling port scan rule

B.

The policy that handles outbound traffic was automatically disabled because the Firebox was port scanned

C.

The port scan traffic matched a default HTTP proxy content type rule configured with a Block action

D.

The server IP address was added to the Blocked Sites list because the network was flooded with ESP traffic during the port scan

E.

The server IP address was added to the Blocked Sites list because an IPS signature was matched during the port scan

Buy Now
Questions 14

In a Mobile VPN configuration, why would you choose default-route (full tunnel) VPN instead of split tunnel VPN? (Select one.)

Options:

A.

Default-route VPN uses less bandwidth.

B.

Default-route VPN enables your Firebox to examine all remote user traffic.

C.

Default-route VPN uses less processing power.

D.

Default-route VPN automatically allows dynamic NAT.

E.

Default-route VPN is the only option you can use to apply security services to connections routed to your internal servers.

Buy Now
Questions 15

In the network configuration shown in this image, which aliases include Eth2 as a member? (Select three.)

Options:

A.

Any-Trusted

B.

Optional-1

C.

Any-External

D.

Any-Optional

E.

Any

Buy Now
Questions 16

Users cannot download a PDF file from your intranet. You know the file is safe to download. When you review the log messages, you see that IntelligentAV identified the file as malicious. The only way to resolve this is to change the file extension.

Options:

A.

True

B.

False

Buy Now
Questions 17

If you have only one public IP address, can you use Static NAT to enable inbound connections to both an email server and a web server on the private network? (Select one.)

Options:

A.

Yes, if both servers are on different private subnets

B.

No, you must use Dynamic NAT to route inbound connections to more than one server

C.

No, you must assign a public IP address to each server

D.

Yes, if both servers use different ports

Buy Now
Questions 18

What does a Firebox configured with default firewall policies do with outbound traffic that does not have a configured route? (Select one.)
Options:

A.

Sends the traffic to the loopback interface

B.

Drops the traffic

C.

Denies the traffic

D.

Sends the traffic to the default gateway

Buy Now
Exam Name: Network Security Essentials for Locally-Managed Fireboxes
Last Update: Oct 31, 2026
Questions: 60
Network-Security-Essentials pdf

Network-Security-Essentials PDF

$21.25  $84.99
Network-Security-Essentials Engine

Network-Security-Essentials Testing Engine

$25  $99.99
Network-Security-Essentials PDF + Engine

Network-Security-Essentials PDF + Testing Engine

$33.75  $134.99