clapgeek logo
While upgrading App1, the agent identifies 47 issues, including a security vulnerability, and 46 API incompatibilities across different projects.
Which two actions are unsafe to delegate to the agent and require human involvement? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
You need to enable Copilot memory to support the planned changes.
What should you configure?
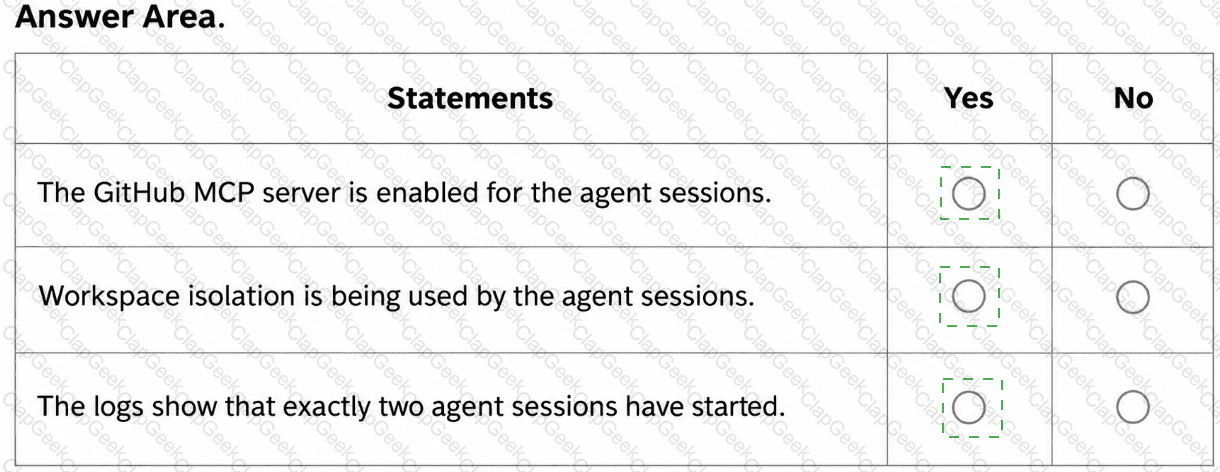
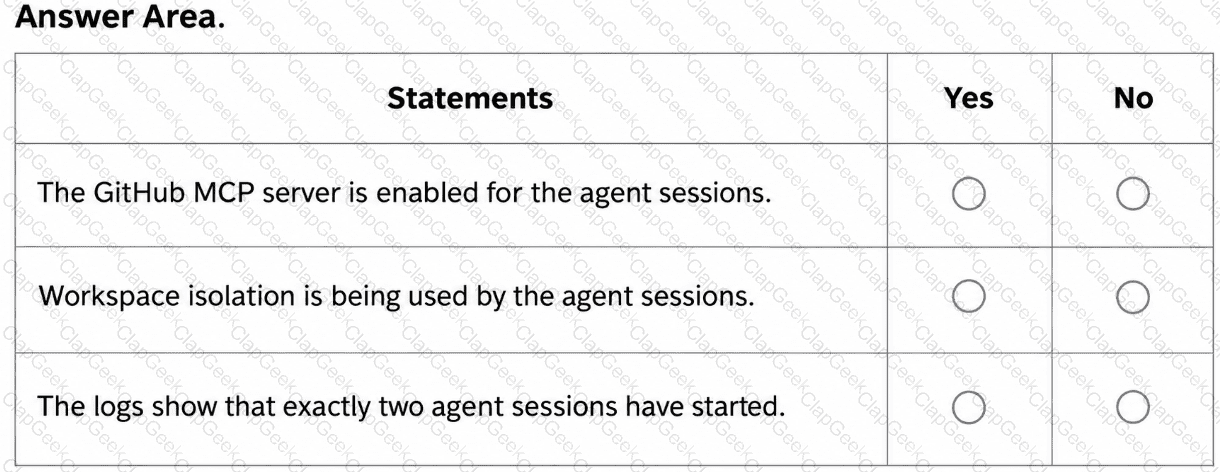
You are evaluating the logs of the multi-agent workflow in repo2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
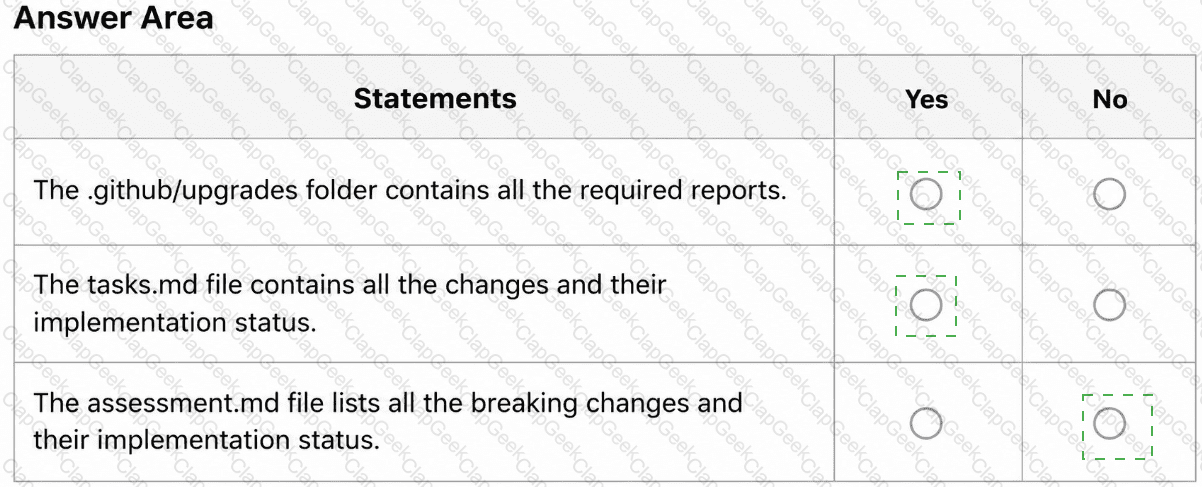
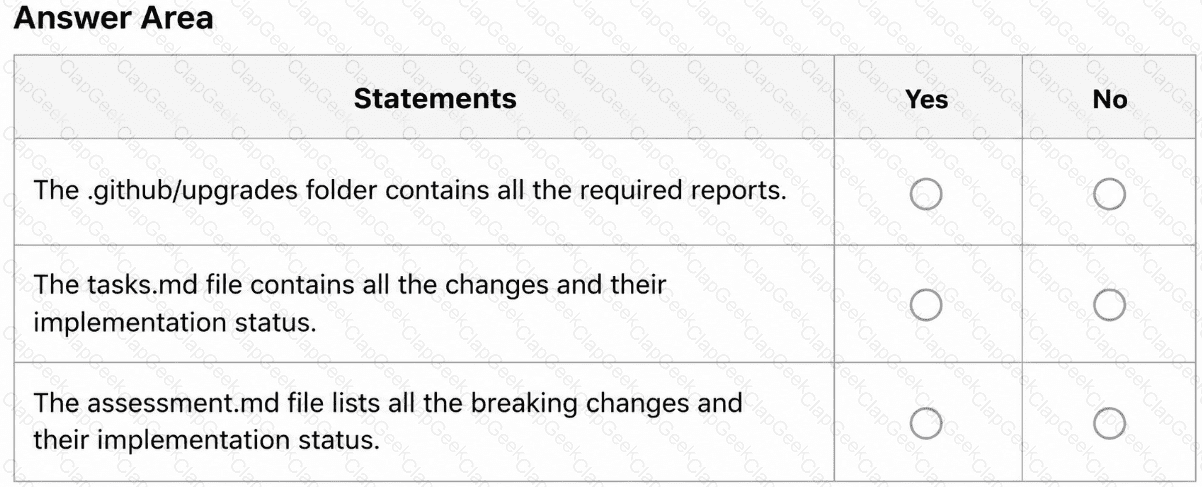
After App1 is upgraded to meet the technical requirements, you need to validate the output.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You need to make changes to repo1 to support the planned changes for the agents.
What should you modify?
You have a private GitHub repository that has Copilot memory enabled.
Several developers who have write access to the repository make changes across multiple branches, including creating some pull requests that are later closed without merging.
Your team needs to understand how GitHub Copilot ensures that only task-relevant, up-to-date information influences code suggestions, even when older memories exist.
How does Copilot manage memories?
You use the GitHub Copilot CLI in a developer terminal.
You plan to use Copilot CLI programmatically to summarize recent commits.
You need to ensure that Copilot performs a low-risk, read-only action without granting Copilot broad write or execution capability.
Which Copilot CLI configuration should you use?
You use the GitHub Copilot CLI in ephemeral dev containers.
You need to provide Copilot with reusable guidance for a specific task only. The guidance must be stored in the repository and invoked only when the task is relevant.
What should you do?
You have a GitHub repository that uses GitHub Actions for CI.
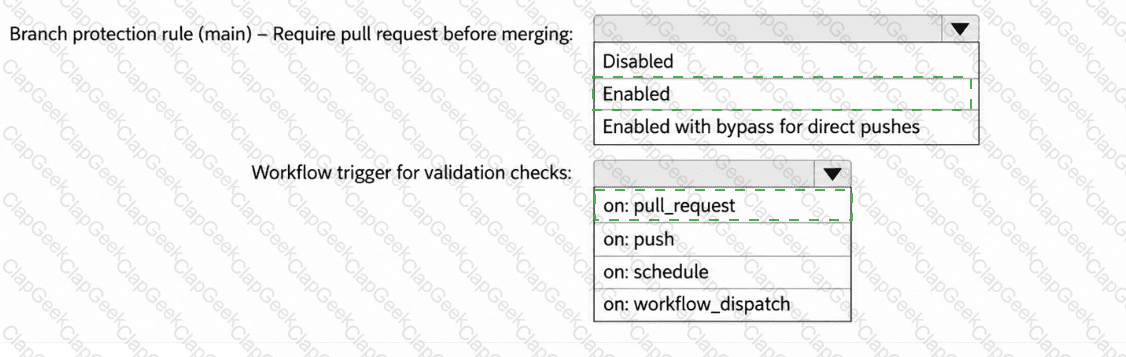
Your team is piloting the GitHub Copilot coding agent to autonomously create branches and open pull requests. The repository follows trunk-based development that uses main as the default branch.
You need to ensure that the agent meets the following requirements:
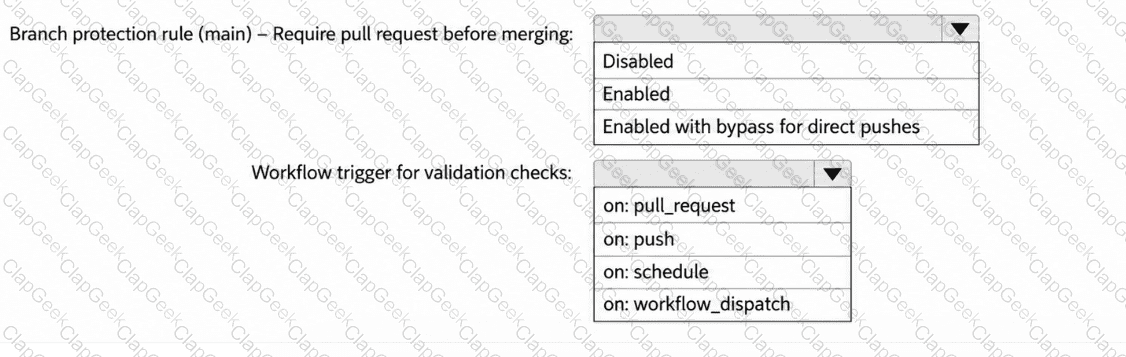
Changes to main can occur only by using pull requests that have at least one approval.
When a pull request is opened, a validation workflow runs.
How should you configure the repository? To answer, select the appropriate options in the answer area.
You assigned an issue to the Copilot coding agent, and it opened a pull request. You want to inspect exactly what code changes were made before merging. Which CLI slash command lets you view the change set directly in the terminal?
You have a GitHub repository that uses the GitHub Copilot coding agent. The repository uses strict branch protections on the main branch.
You maintain a long-lived branch named release/1.4 that has different dependencies and CI checks.
You need the agent to create a hotfix that is implemented and validated against the release/1.4 branch. The solution must prevent the agent from basing its work on main.
What should you do?
You need to provide access to the API key of MCP1. The solution must meet the security requirements.
What should you do?
You need to resolve the issue of the agents generating conflicting output. The solution must meet the implementation guidelines.
What should you do?
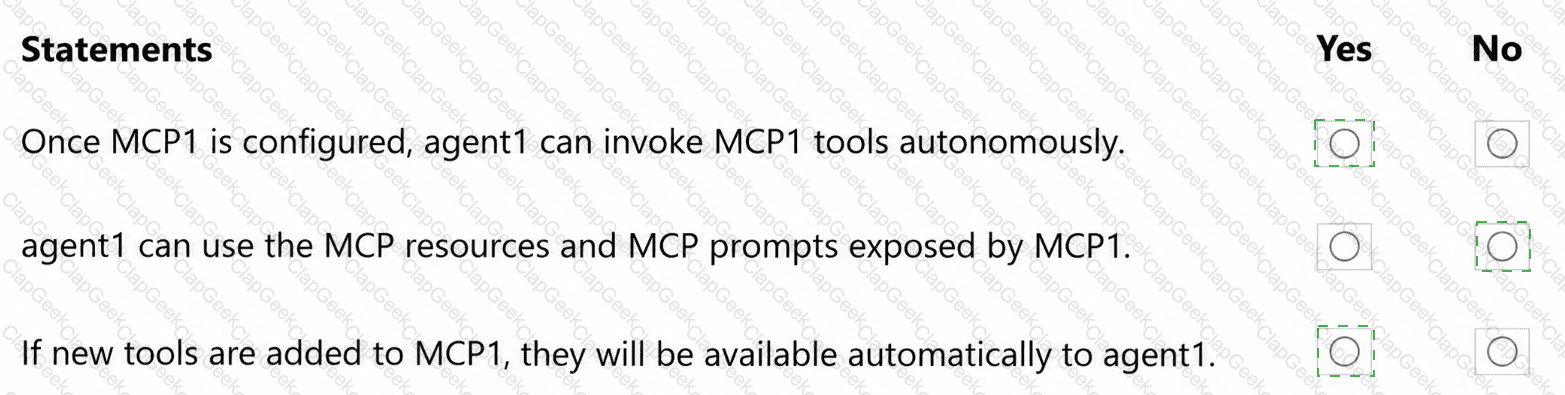
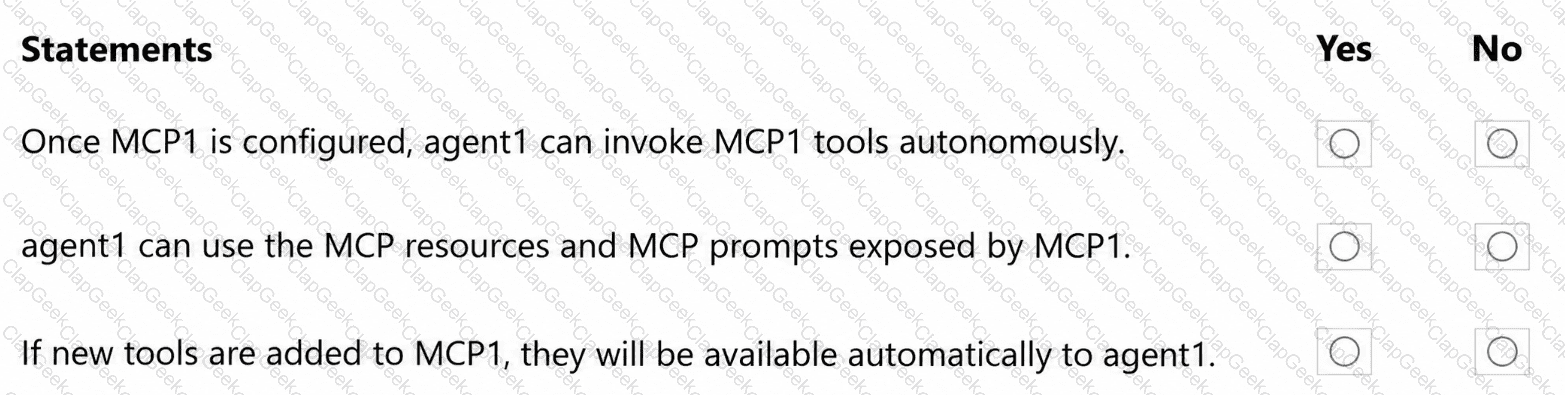
You are evaluating how agent1 will behave after you implement the planned changes.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You need to configure agent1 to support the planned changes.
What should you do?
TESTED 20 Sep 2026