Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save75geek

300-710 Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Questions and Answers

Questions 4

What is a characteristic of bridge groups on a Cisco FTD?

Options:

A.

In routed firewall mode, routing between bridge groups must pass through a routed interface.

B.

In routed firewall mode, routing between bridge groups is supported.

C.

In transparent firewall mode, routing between bridge groups is supported

D.

Routing between bridge groups is achieved only with a router-on-a-stick configuration on a connected router

Buy Now
Questions 5

An engineer must configure a passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:

•Set the interface mode to Passive.

•Configure the MTU.

•Set the speed and duplex. Which action completes the configuration?

Options:

A.

Reset the NGIPS

B.

Reregister the NGIPS.

C.

Enable the bridge virtual interface.

D.

Enable the interface.

Buy Now
Questions 6

An engineer is setting up a new Cisco Secure Firewall Threat Defense appliance to replace the current firewall. The company requests that inline sets be used and that when one interface in

an inline set goes down, the second interface in the inline set goes down. What must the engineer configure to meet the deployment requirements?

Options:

A.

strict TCP enforcement

B.

propagate link state

C.

Snort fail open

D.

inline tap mode

Buy Now
Questions 7

Which action should be taken after editing an object that is used inside an access control policy?

Options:

A.

Delete the existing object in use.

B.

Refresh the Cisco FMC GUI for the access control policy.

C.

Redeploy the updated configuration.

D.

Create another rule using a different object name.

Buy Now
Questions 8

A security analyst is investigating a potential network compromise. The analyst must produce a report of the suspicious activity from Cisco Secure Firewall Management Center. Which two details must be included in the report to assist the investigation? (Choose two.)

Options:

A.

Client applications by user

B.

Intrusion events

C.

Host connections

D.

Number of attacked machines

E.

User connections

Buy Now
Questions 9

A network engineer wants to add a third-party threat feed into the Cisco FMC for enhanced threat detectionWhich action should be taken to accomplish this goal?

Options:

A.

Enable Threat Intelligence Director using STIX and TAXII

B.

Enable Rapid Threat Containment using REST APIs

C.

Enable Threat Intelligence Director using REST APIs

D.

Enable Rapid Threat Containment using STIX and TAXII

Buy Now
Questions 10

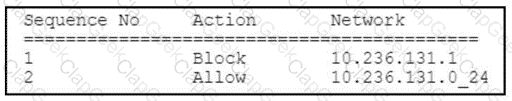
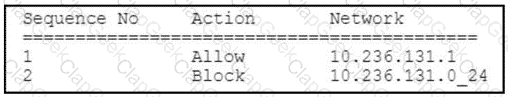
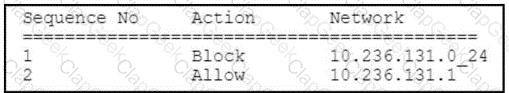
A security engineer must create an access list object in Cisco Secure Firewall Management Center to allow traffic to IP address 10.236.131.1 but block traffic to IP address 10.236.131.0/24. Which access control entries must the engineer create?

A)
B)
C)
D)
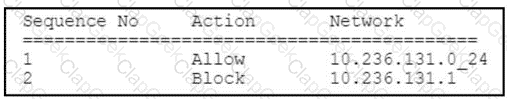
Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Buy Now
Questions 11

An engineer must deny ICMP traffic to the networks of separate departments that use Cisco Secure Firewall Management Center. The engineer must use the same object on the relevant device for each network. What must be configured in Secure Firewall Management Center?

Options:

A.

IP address

B.

IP range

C.

Deny ICMP check box

D.

Allow Overrides check box

Buy Now
Questions 12

A network administrator is configuring an access control policy on a Secure Firewall Threat Defense device. The administrator wants to exclude traffic to a certain banking site from being decrypted. What must the rule include to specify the banking site?

Options:

A.

action of trust, specified protocol for SSL, and below the SSL decryption rule

B.

action of deny and for the HTTP and HTTPS access protocols

C.

action of block, specified protocol for SSL, and above the SSL decryption rule

D.

action of trust and above the SSL decryption rule

Buy Now
Questions 13

An engineer must implement Cisco Secure Firewall transparent mode due to a new server recently being added that must communicate with an existing server that is currently separated by the firewall. Which implementation action must be taken next by the engineer to accomplish the goal?

Options:

A.

Enable both servers to share the same VXLAN segment.

B.

Configure the same default gateway for both servers.

C.

Ensure that both servers are in the same bridge domain.

D.

Assign the same subnet to both servers.

Buy Now
Questions 14

Which two routing options are valid with Cisco Firepower Threat Defense? (Choose two.)

Options:

A.

BGPv6

B.

ECMP with up to three equal cost paths across multiple interfaces

C.

ECMP with up to three equal cost paths across a single interface

D.

BGPv4 in transparent firewall mode

E.

BGPv4 with nonstop forwarding

Buy Now
Questions 15

The network administrator wants to enhance the network security posture by enabling machine learning tor malware detection due to a concern with suspicious Microsoft executable file types that were seen while creating monthly security reports for the CIO. Which feature must be enabled to accomplish this goal?

Options:

A.

Spero

B.

dynamic analysis

C.

static analysis

D.

Ethos

Buy Now
Questions 16

A network administrator must send a daily email report to management detailing changes made during the previous 24 hours in Cisco Secure Firewall Management Center. Which system setting must be enabled to meet this requirement?

Options:

A.

Change Reconciliation

B.

Send Audit Log to HTTP Server

C.

Send Audit Log to Syslog

D.

STIG Compliance

Buy Now
Questions 17

An engineer is using the configure manager add < FMC IP > Cisc402098527 command to add a new Cisco FTD device to the Cisco FMC; however, the device is not being added. Why Is this occurring?

Options:

A.

The NAT ID is required since the Cisco FMC is behind a NAT device.

B.

The IP address used should be that of the Cisco FTD. not the Cisco FMC.

C.

DONOTRESOLVE must be added to the command

D.

The registration key is missing from the command

Buy Now
Questions 18

When packet capture is used on a Cisco Secure Firewall Threat Defense device and the packet flow is wailing on the malware query, which Snort verdict appears?

Options:

A.

retry

B.

replace

C.

block

D.

blocfcflow

Buy Now
Questions 19

An engineer is troubleshooting connectivity to the DNS servers from hosts behind a new Cisco FTD device. The hosts cannot send DNS queries to servers in the DMZ. Which action should the engineer take to troubleshoot this issue using the real DNS packets?

Options:

A.

Use the Connection Events dashboard to check the block reason and adjust the inspection policy as needed.

B.

Use the packet capture tool to check where the traffic is being blocked and adjust the access control or intrusion policy as needed.

C.

Use the packet tracer tool to determine at which hop the packet is being dropped.

D.

Use the show blocks command in the Threat Defense CLI tool and create a policy to allow the blocked traffic.

Buy Now
Questions 20

A security engineer must configure a Cisco Secure Firewall Threat Defense device to inspect only executable files. A lightweight method of detecting whether a file is an executable must be used. Which configuration for Malware Cloud Lookup must be selected in Cisco Secure Firewall Management Center?

Options:

A.

capacity handling

B.

Local Malware Analysis

C.

dynamic analysis

D.

Spero analysis for MSEXE

Buy Now
Questions 21

An engineer is configuring a new dashboard within Cisco Secure Firewall Management Center and is having trouble implementing a custom widget. When a custom analysis widget is configured which option is mandatory for the system to display the information?

Options:

A.

table

B.

filter

C.

title

D.

results

Buy Now
Questions 22

When do you need the file-size command option during troubleshooting with packet capture?

Options:

A.

when capture packets are less than 16 MB

B.

when capture packets are restricted from the secondary memory

C.

when capture packets exceed 10 GB

D.

when capture packets exceed 32 MB

Buy Now
Questions 23

A network engineer implements a new Cisco Firepower device on the network to take advantage of its intrusion detection functionality. There is a requirement to analyze the traffic going across the device, alert on any malicious traffic, and appear as a bump in the wire How should this be implemented?

Options:

A.

Specify the BVl IP address as the default gateway for connected devices.

B.

Enable routing on the Cisco Firepower

C.

Add an IP address to the physical Cisco Firepower interfaces.

D.

Configure a bridge group in transparent mode.

Buy Now
Questions 24

A security engineer must create a Network Operations Center dashboard to display detailed information about the events collected by Secure Firewall Management Center. A Custom Analysis widget must be configured to display how many intrusion events of each type occurred by using the Intrusion Events table, with the data aggregated by Event Count. Which field must be configured to create the widget?

Options:

A.

Time field and data aggregated by Unique Events

B.

Classification field and data aggregated by Event Count

C.

Date field and data aggregated by Unique Events

D.

Device field and data aggregated by Event Count

Buy Now
Questions 25

An engineer configures an access control rule that deploys file policy configurations to security zones or tunnel zones, and it causes the device to restart. What is the reason for the restart?
Options:

A.

Source or destination security zones in the access control rule matches the security zones that are associated with interfaces on the target devices.

B.

The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the destination policy.

C.

Source or destination security zones in the source tunnel zone do not match the security zones that are associated with interfaces on the target devices.

D.

The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the source policy.

Buy Now
Questions 26

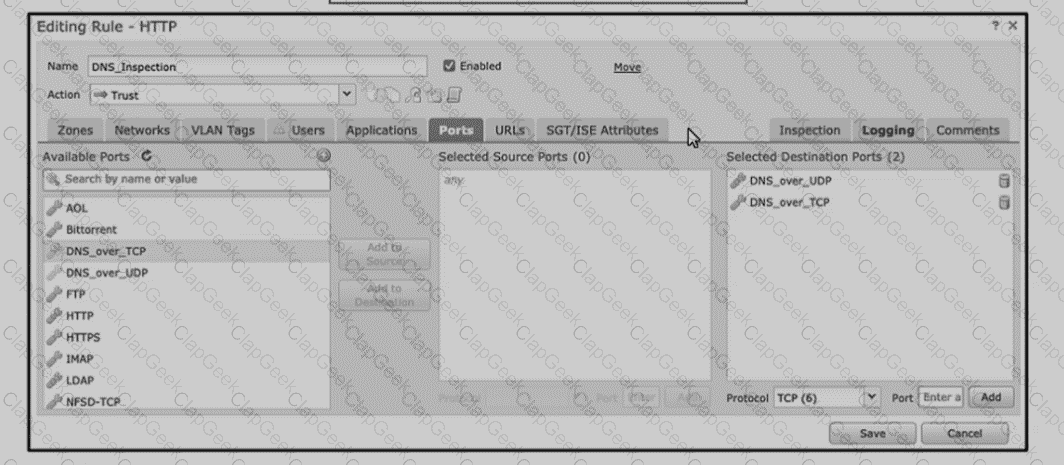
Refer to the exhibit An engineer is modifying an access control pokey to add a rule to inspect all DNS traffic that passes through the firewall After making the change and deploying thepokey they see that DNS traffic is not bang inspected by the Snort engine What is the problem?

Options:

A.

The rule must specify the security zone that originates the traffic

B.

The rule must define the source network for inspection as well as the port

C.

The action of the rule is set to trust instead of allow.

D.

The rule is configured with the wrong setting for the source port

Buy Now
Questions 27

Which license type is required on Cisco ISE to integrate with Cisco FMC pxGrid?

Options:

A.

mobility

B.

plus

C.

base

D.

apex

Buy Now
Questions 28

Network users experience issues when accessing a server on a different network segment. An engineer investigates the issue by performing packet capture on Cisco Secure Firewall Threat Defense. The engineer expects more data and suspects that not all the traffic was collected during a 15-minute can’t captured session. Which action must the engineer take to resolve the issue?

Options:

A.

Forward the captured data lo an FTP server

B.

Increase the amount of RAM allocated for the capture.

C.

Provide a file name to save the data.

D.

Ensure that the allocated memory is sufficient.

Buy Now
Questions 29

What is the result of specifying of QoS rule that has a rate limit that is greater than the maximum throughput of an interface?

Options:

A.

The rate-limiting rule is disabled.

B.

Matching traffic is not rate limited.

C.

The system rate-limits all traffic.

D.

The system repeatedly generates warnings.

Buy Now
Questions 30

A network engineer detects a connectivity issue between Cisco Secure Firewall Management Center and Cisco Secure Firewall Threat Defense. Initial troubleshooting indicates that heartbeats and events are not being received. The engineer re-establishes the secure channels between both peers. Which two commands must the engineer run to resolve the issue? (Choose two.)

Options:

A.

show disk-manager

B.

show history

C.

sudo stats_unified.pl

D.

manage_procs.pl

E.

sudo perfstats -Cq < /var/sf/rna/correlator-stats/now

Buy Now
Questions 31

A network engineer must provide a high-level statistical summary of a Cisco Secure Firewall Threat Defense device. The organization is approaching its peak season, so network downtime must be minimized. Which type of report must the network engineer use?

Options:

A.

Malware

B.

SNMP

C.

Risk

D.

Host

Buy Now
Questions 32

An administrator configures the interfaces of a Cisco Secure Firewall Threat Defence device in an inline IPS deployment. The administrator completes these actions:

* identifies the device and the interfaces

* sets the interface mode to inline

* enables the interlaces

Which configuration step must the administrator take next to complete the implementation?

Options:

A.

Enable spanning-tree PortFast on the interfaces.

B.

Configure an inline set

C.

Set the interface to Transparent mode.

D.

Set the interface to routed mode.

Buy Now
Questions 33

A security engineer needs to configure a network discovery policy on a Cisco FMC appliance and prevent excessive network discovery events from overloading the FMC database? Which action must be taken to accomplish this task?

Options:

A.

Change the network discovery method to TCP/SYN.

B.

Configure NetFlow exporters for monitored networks.

C.

Monitor only the default IPv4 and IPv6 network ranges.

D.

Exclude load balancers and NAT devices in the policy.

Buy Now
Questions 34

When using Cisco Threat Response, which phase of the Intelligence Cycle publishes the results of the investigation?

Options:

A.

direction

B.

dissemination

C.

processing

D.

analysis

Buy Now
Questions 35

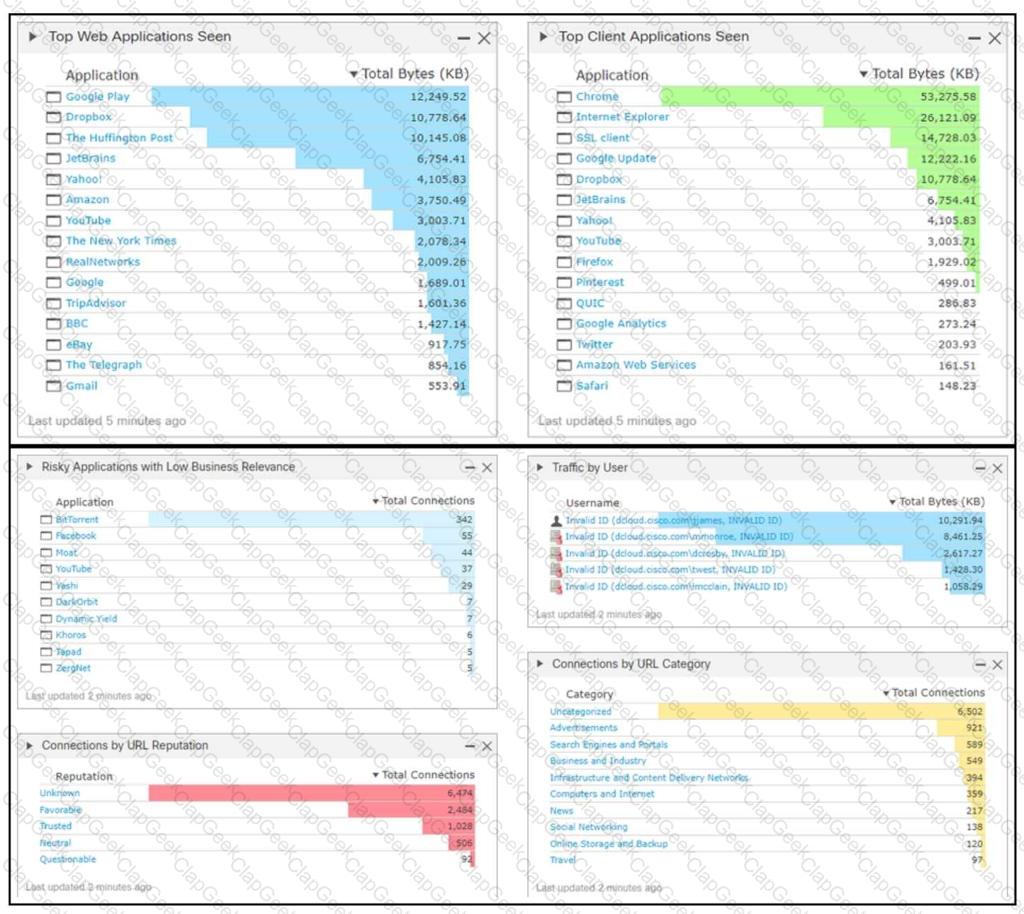
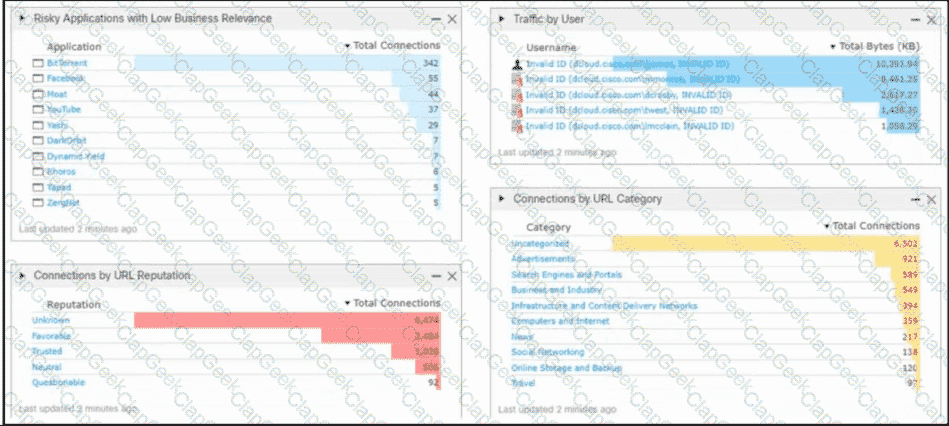
Refer to the exhibit.

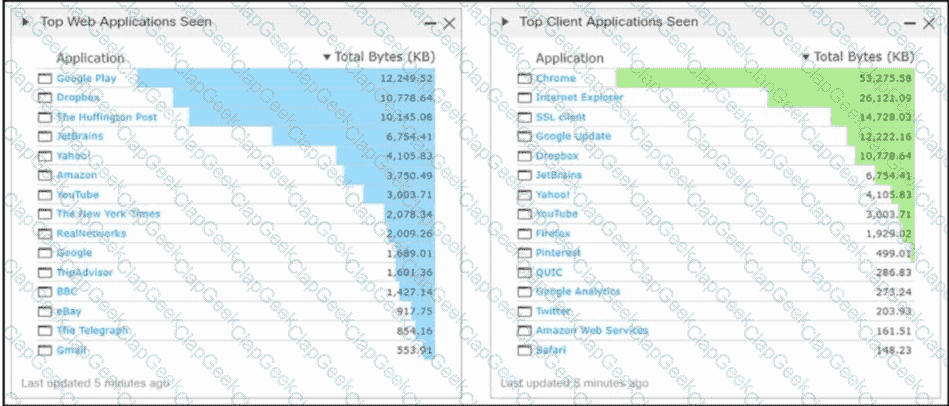
An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must the engineer take to decrease the application usage risk?

Options:

A.

Disable the use of Google Play.

B.

Disable the user account.

C.

Block all the BitTorrent applications.

D.

Patch all the Google Chrome browsers.

Buy Now
Questions 36

A network administrator wants to block traffictoa known malware site athttps://www.badsite.comand all subdomains while ensuring no packets from any internal client are sent to that site. Which type of policy must the network administrator use to accomplish this goal?

Options:

A.

Prefilter policy

B.

SSL policy

C.

DNS policy

D.

Access Control policy with URL filtering

Buy Now
Questions 37

A company has many Cisco FTD devices managed by a Cisco FMC. The security model requires that access control rule logs be collected for analysis. The security engineer is concerned that the Cisco FMC will not be able to process the volume of logging that will be generated. Which configuration addresses this concern?

Options:

A.

Send Cisco FTD connection events and security events directly to SIEM system for storage and analysis.

B.

Send Cisco FTD connection events and security events to a cluster of Cisco FMC devices for storage and analysis.

C.

Send Cisco FTD connection events and security events to Cisco FMC and configure it to forward logs to SIEM for storage and analysis.

D.

Send Cisco FTD connection events directly to a SIEM system and forward security events from Cisco FMC to the SIEM system for storage and analysis.

Buy Now
Questions 38

A network administrator is trying to configure Active Directory authentication for VPN authentication to a Cisco Secure Firewall Threat Defence instance that is registered with Cisco Secure Firewall Management Center. Which system settings must be configured first in Secure Firewall Management Center to accomplish the goal?

Options:

A.

Device, Remote Access VPN

B.

System, Realms

C.

Policies, Authentication

D.

Authentication, Device

Buy Now
Questions 39

A consultant Is working on a project where the customer is upgrading from a single Cisco Firepower 2130 managed by FDM to a pair of Cisco Firepower 2130s managed oy FMC tor nigh availability. The customer wants the configures of the existing device being managed by FDM to be carried over to FMC and then replicated to the additional: device being added to create the high availability pair. Which action must the consultant take to meet this requirement?

Options:

A.

The current FDM configuration must be configured by hand into FMC before the devices are registered.

B.

The current FDM configuration will be converted automatically into FMC when the device registers.

C.

The current FDM configuration must be migrated to FMC using the Secure Firewall Migration Tool.

D.

The FTD configuration must be converted to ASA command format, which can then be migrated to FMC.

Buy Now
Questions 40

A network administrator notices that inspection has been interrupted on all non-managed interfaces of a device. What is the cause of this?

Options:

A.

The value of the highest MTU assigned to any non-management interface was changed.

B.

The value of the highest MSS assigned to any non-management interface was changed.

C.

A passive interface was associated with a security zone.

D.

Multiple inline interface pairs were added to the same inline interface.

Buy Now
Questions 41

What is the advantage of having Cisco Firepower devices send events to Cisco Threat response via the security services exchange portal directly as opposed to using syslog?

Options:

A.

Firepower devices do not need to be connected to the internet.

B.

All types of Firepower devices are supported.

C.

Supports all devices that are running supported versions of Firepower

D.

An on-premises proxy server does not need to set up and maintained

Buy Now
Questions 42

A network administrator must send management a daily email report describing changes made during the previous 24 hours in Cisco Secure Firewall Management Center. Which system setting must be enabled?

Options:

A.

STIG Compliance

B.

Send Audit Log to Syslog

C.

Change Reconciliation

D.

Send Audit Log to HTTP Server

Buy Now
Questions 43

A network administrator cannot select the link to be used for failover when configuring an active/passive HA Cisco FTD pair.

Which configuration must be changed before setting up the high availability pair?

Options:

A.

An IP address in the same subnet must be added to each Cisco FTD on the interface.

B.

The interface name must be removed from the interface on each Cisco FTD.

C.

The name Failover must be configured manually on the interface on each cisco FTD.

D.

The interface must be configured as part of a LACP Active/Active EtherChannel.

Buy Now
Questions 44

An engineer must deploy a high-availability that includes two Cisco Secure Firewall Threat Defense devices configured as cluster. The deployment must have a mechanism that protects synchronization between cluster members Which action must the engineer take to meet the requirements?

Options:

A.

Encrypt the synchronization traffic with SSL.

B.

Configure an SSL VPN tunnel between units.

C.

Clear the commit queue at the time of a sync.

D.

Select the Key Generation method for IPsec.

Buy Now
Questions 45

An engineer must export a packet capture from Cisco Secure Firewall Management Center to assist in troubleshooting an issue an a Secure Firewall Threat Defense device. When the engineer navigates to URL for Secure Firewall Management Center at:

.. < FMC IP > /capture/CAP/pcap/sample.pcap

An engineer receives a 403: Forbidden error instead of being provided with the PCAP file. Which action resolves the issue?

Options:

A.

Disable the HTTPS server and use HTTP.

B.

Enable the proxy setting in the device platform policy.

C.

Enable HTTPS in the device platform policy.

D.

Disable the proxy setting on the client browser.

Buy Now
Questions 46

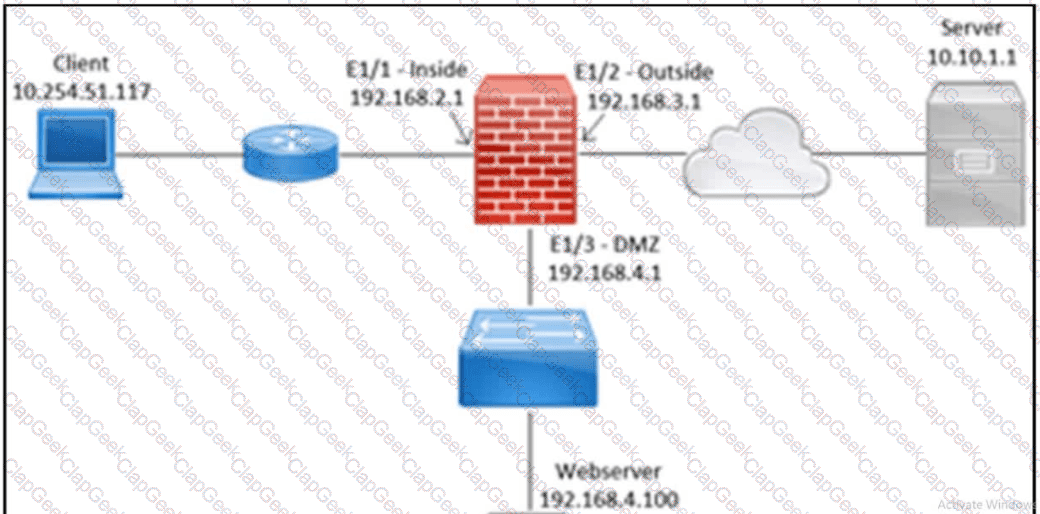
Refer to the exhibit.

A client with IP address 10.254.51.117 connects through a Cisco Secure Firewall Threat Defense device toward a website at 10.10.1.1. The packet capture shows repeated TCP SYN packets from the client without completion of the three-way handshake. Which action must the engineer take to resolve the issue?
Options:

A.

Configure the inside interface to send ACK messages.

B.

Add a firewall rule that allows the web server to communicate with the DMZ.

C.

Add a firewall rule that allows ACK responses from the inside to the outside.

D.

Configure the outside interface to receive SYN-ACK messages.

Buy Now
Questions 47

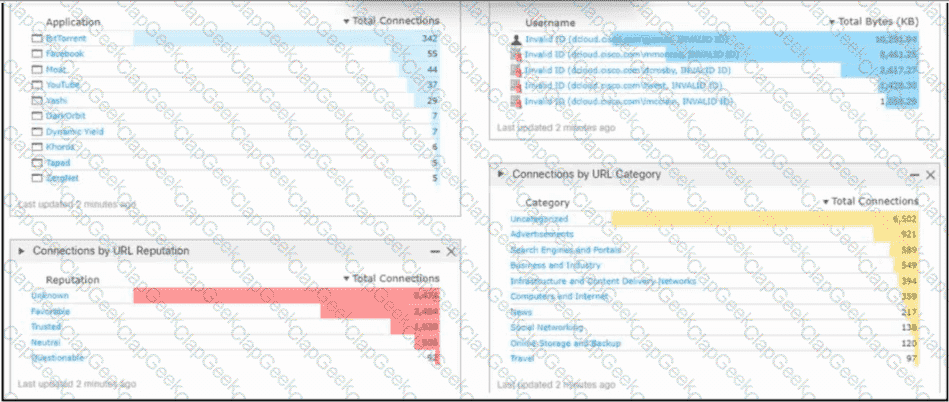
Refer to the exhibit. An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must be taken by the user to decrease the risk of data loss?

Options:

A.

Stop all URLs that have an unknown reputation.

B.

Block the use of Dropbox.

C.

Stop all the URLs that are uncategorized.

D.

Block all the BitTorrent applications.

Buy Now
Questions 48

A network engineer is deploying a pair of Cisco Secure Firewall Threat Defense devices managed by Cisco Secure Firewall Management Center tor High Availability Internet access is a high priority for the business and therefore they have invested in internet circuits from two different ISPs. The requirement from the customer Is that Internet access must do available to their user’s oven if one of the ISPs is down. Which two features must be deployed to achieve this requirement? (Choose two.)

Options:

A.

EtherChannel interfaces

B.

Route Tracking

C.

SLA Monitor

D.

Redundant interfaces

E.

BGP

Buy Now
Questions 49

A network engineer wants to disable the HTTP response page and interactive blocking of the entire access control policy in Cisco Secure Firewall Management Center. What must be

selected in Block Response Page and Interactive Block Response Page?

Options:

A.

Custom

B.

View

C.

System

D.

None

Buy Now
Questions 50

A network administrator is reviewing a monthly advanced malware risk report and notices a host that Is listed as CnC Connected. Where must the administrator look within Cisco FMC to further determine if this host is infected with malware?

Options:

A.

Analysis > Hosts > indications of Compromise

B.

Analysts > Files > Malware Events

C.

Analysis > Hosts > Host Attributes

D.

Analysis > Flies > Network File Trajectory

Buy Now
Questions 51

Which Firepower feature allows users to configure bridges in routed mode and enables devices to perform Layer 2 switching between interfaces?

Options:

A.

FlexConfig

B.

BDI

C.

SGT

D.

IRB

Buy Now
Questions 52

Which Cisco Secure Firewall Threat Defense interface mode must be deployed when implementing an IPS that must receive and retransmit all traffic unless the traffic is explicitly dropped?

Options:

A.

Routed

B.

Inline

C.

Passive

D.

Transparent

Buy Now
Questions 53

An engainermust add DNS-specific rules to me Cisco FTD intrusion policy. The engineer wants to use the rules currently in the Cisco FTD Snort database that are not already enabled but does not want to enable more than are needed. Which action meets these requirements?

Options:

A.

Change the dynamic state of the rule within the policy.

B.

Change the base policy to Security over Connectivity.

C.

Change the rule state within the policy being used.

D.

Change the rules using the Generate and Use Recommendations feature.

Buy Now
Questions 54

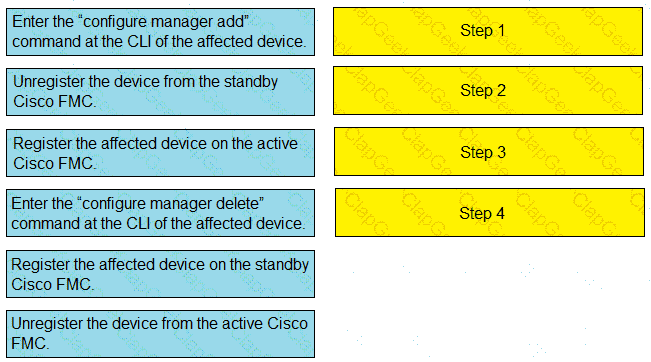
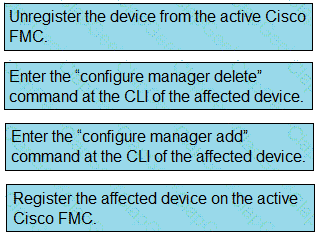
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.

Options:

Buy Now
Questions 55

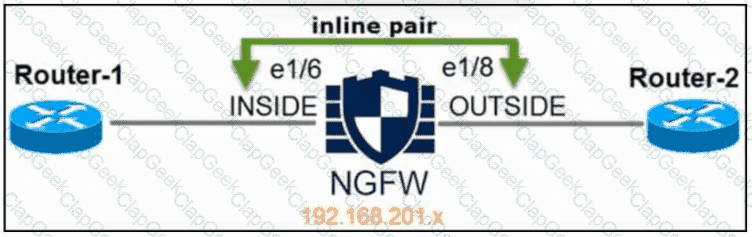
Refer to the exhibit. An engineer is configuring an instance of Cisco Secure Firewall Threat Defense with interfaces in IPS Inline Pair mode. What must be configured on interface e1/6 to accomplish the requirement?

Options:

A.

propagate link state disabled

B.

inline set MTU set to 1500

C.

FailSafe disabled

D.

security zone set to OUTSIDE_ZONE

Buy Now
Questions 56

A security engineer must integrate an external feed containing STIX/TAXII data with Cisco FMC. Which feature must be enabled on the Cisco FMC to support this connection?

Options:

A.

Cisco Success Network

B.

Cisco Secure Endpoint Integration

C.

Threat Intelligence Director

D.

Security Intelligence Feeds

Buy Now
Questions 57

An engineer has been tasked with performing an audit of network projects to determine which objects are duplicated across the various firewall models (Cisco Secure Firewall Threat Defense Cisco Secure firewall ASA, and Meraki MX Series) deployed throughout the company Which tool will assist the engineer in performing that audit?

Options:

A.

Cisco Firepower Device Manager

B.

Cisco SecureX

C.

Cisco Defense Orchestrator

D.

Cisco Secure Firewall Management Center

Buy Now
Questions 58

When creating a report template, how can the results be limited to show only the activity of a specific subnet?

Options:

A.

Create a custom search in Firepower Management Center and select it in each section of the report.

B.

Add an Input Parameter in the Advanced Settings of the report, and set the type to Network/IP.

C.

Add a Table View section to the report with the Search field defined as the network in CIDR format.

D.

Select IP Address as the X-Axis in each section of the report.

Buy Now
Questions 59

An engineer must change the mode of a Cisco Secure Firewall Threat Defense (FTD) firewall in the Cisco Secure Firewall Management Center (FMC) inventory. The engineer must take these actions:

• Register Secure FTD with Secure FMC.

• Change the firewall mode.

• Deregister the Secure FTD device from Secure FMC.

How must the engineer take FTD take the actions?

Options:

A.

Reload the Secure FTD device.

B.

Configure the management IP address.

C.

Access the Secure FTD CLI from the console port.

D.

Erase the Secure FTD configuration

Buy Now
Questions 60

What is the maximum SHA level of filtering that Threat Intelligence Director supports?

Options:

A.

SHA-1024

B.

SHA-4096

C.

SHA-512

D.

SHA-256

Buy Now
Questions 61

Which connector is used to integrate Cisco ISE with Cisco FMC for Rapid Threat Containment?

Options:

A.

pxGrid

B.

FTD RTC

C.

FMC RTC

D.

ISEGrid

Buy Now
Questions 62

Which command-line mode is supported from the Cisco Firepower Management Center CLI?

Options:

A.

privileged

B.

user

C.

configuration

D.

admin

Buy Now
Questions 63

A network administrator notices that SI events are not being updated The Cisco FTD device is unable to load all of the SI event entries and traffic is not being blocked as expected. What must be done to correct this issue?

Options:

A.

Restart the affected devices in order to reset the configurations

B.

Manually update the SI event entries to that the appropriate traffic is blocked

C.

Replace the affected devices with devices that provide more memory

D.

Redeploy configurations to affected devices so that additional memory is allocated to the SI module

Buy Now
Questions 64

Which interface mode on the firewall must be deployed on a Cisco Secure Firewall Threat Defense when implementing an IPS using a SPAN port for traffic monitoring?

Options:

A.

transparent

B.

inline

C.

passive

D.

routed

Buy Now
Questions 65

An administrator is attempting to add a new FTD device to their FMC behind a NAT device with a NAT ID of NAT001 and a password of Cisco0420l06525. The private IP address of the FMC server is 192.168.45.45. which is being translated to the public IP address of 209.165.200.225/27. Which command set must be used in order to accomplish this task?

Options:

A.

configure manager add 209.165.200.225 < reg_key > < nat_id >

B.

configure manager add 192.168.45,45 < reg_key > < nat_id >

C.

configure manager add 209.165.200.225 255.255.255.224 < reg_key > < nat_id >

D.

configure manager add 209.165.200.225/27 < reg_key > < nat_id >

Buy Now
Questions 66

An engineer is configuring two new Cisco FTD devices to replace the existing high availability firewall pair in a highly secure environment. The information exchanged between the FTD devices over the failover link must be encrypted. Which protocol supports this on the Cisco FTD?

Options:

A.

IPsec

B.

SSH

C.

SSL

D.

MACsec

Buy Now
Questions 67

A network administrator is trying to configure a previously created file policy on a new access policy. Which action must the administrator take before applying the file policy?

Options:

A.

Set up an inspection policy.

B.

Create a new access control rule.

C.

Assign the file policy to the default action.

D.

Apply an application to an access control rule.

Buy Now
Questions 68

An engineer is configuring a custom intrusion rule on Cisco FMC. The engineer needs the rule to search the payload or stream for the string " |45 5* 26 27 4 0A|*. Which Keyword must the engineer use with this stung lo create an argument for packed inspection?

Options:

A.

metadata

B.

Content

C.

Protected _ content

D.

data

Buy Now
Questions 69

When a Cisco FTD device is configured in transparent firewall mode, on which two interface types can an IP address be configured? (Choose two.)

Options:

A.

Diagnostic

B.

EtherChannel

C.

BVI

D.

Physical

E.

Subinterface

Buy Now
Questions 70

An engineer defines a new rule while configuring an Access Control Policy. After deploying the policy, the rule is not working as expected and the hit counters associated with the rule are showing zero. What is causing this error?

Options:

A.

Logging is not enabled for the rule.

B.

The rule was not enabled after being created.

C.

The wrong source interface for Snort was selected in the rule.

D.

An incorrect application signature was used in the rule.

Buy Now
Questions 71

In a Cisco AMP for Networks deployment, which disposition is returned if the cloud cannot be reached?

Options:

A.

unavailable

B.

unknown

C.

clean

D.

disconnected

Buy Now
Questions 72

Which command should be used on the Cisco FTD CLI to capture all the packets that hit an interface?

Options:

A.

configure coredump packet-engine enable

B.

capture-traffic

C.

capture

D.

capture WORD

Buy Now
Questions 73

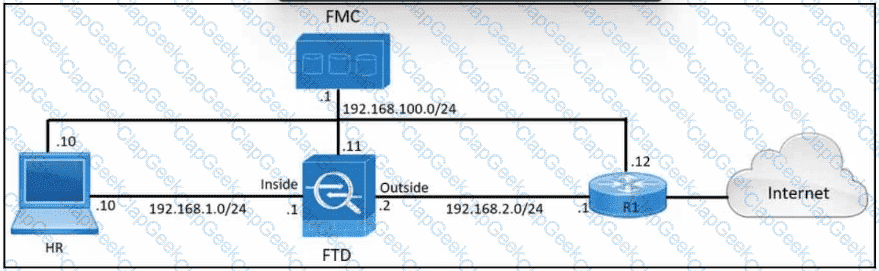
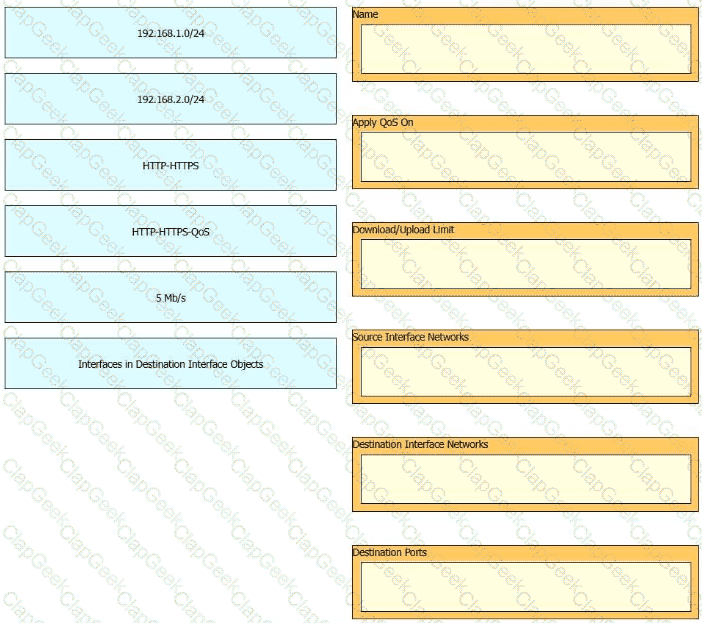
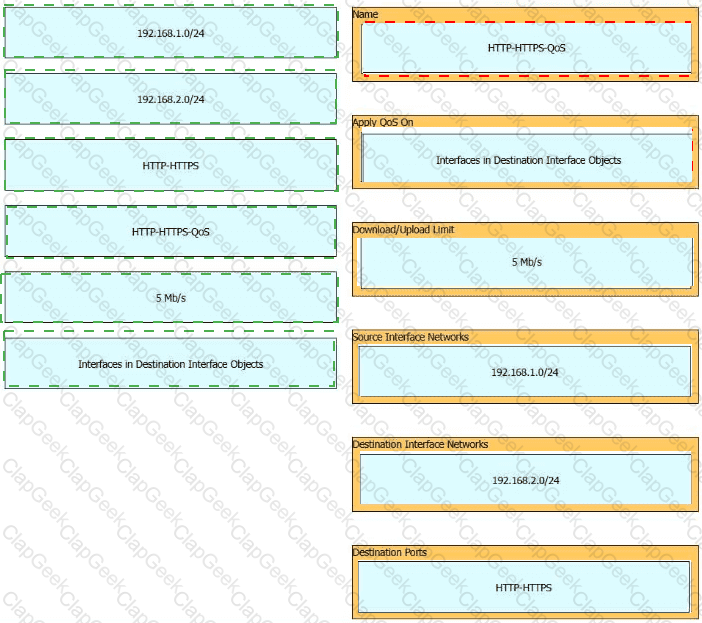
Refer to the exhibit.

An engineer must create a QoS policy in Cisco Secure Firewall Management Center to limit HTTP and HTTPS traffic originating from users in the HR department. The download and upload limits for HTTP and HTTPS traffic must both be set to 5 Mb/s. Drag and drop the values onto the corresponding QoS rule settings.

Options:

Buy Now
Questions 74

An engineer integrates Cisco FMC and Cisco ISE using pxGrid. Which role is assigned for Cisco FMC?

Options:

A.

controller

B.

publisher

C.

client

D.

server

Buy Now
Questions 75

A security engineer found a suspicious file from an employee email address and is trying to upload it for analysis, however the upload is failing. The last registration status is still active. What is the cause for this issue?

Options:

A.

Cisco AMP for Networks is unable to contact Cisco Threat Grid on premise.

B.

Cisco AMP for Networks is unable to contact Cisco Threat Grid Cloud.

C.

There is a host limit set.

D.

The user agent status is set to monitor.

Buy Now
Questions 76

An administrator must use Cisco FMC to install a backup route within the Cisco FTD to route traffic in case of a routing failure with the primary route. Which action accomplishes this task?

Options:

A.

Install the static backup route and modify the metric to be less than the primary route.

B.

Configure EIGRP routing on the FMC to ensure that dynamic routes are always updated.

C.

Use a default route on the FMC instead of having multiple routes contending for priority.

D.

Create the backup route and use route tracking on both routes to a destination IP address in the network.

Buy Now
Questions 77

A network administrator is troubleshooting access to a website hosted behind a Cisco FTD device External clients cannot access the web server via HTTPS The IP address configured on the web server is 192 168 7.46 The administrator is running the command capture CAP interface outside match ip any 192.168.7.46 255.255.255.255 but cannot see any traffic in the capture Why is this occurring?

Options:

A.

The capture must use the public IP address of the web server.

B.

The FTD has no route to the web server.

C.

Theaccess policy is blocking the traffic.

D.

The packet capture shows only blocked traffic

Buy Now
Questions 78

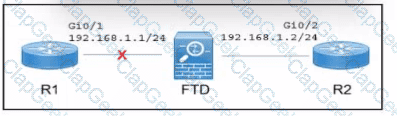
Refer to the exhibit.

A Cisco Secure Firewall Threat Defense (FTD) device is deployed in inline mode with an inline set. The network engineer wants router R2 to remove the directly connected route M 68.1.0/24 from its routing table when the cable between routed R1 and the Secure FTD device Is disconnected. Which action must the engineer take?

1

Options:

A.

Implement the Propagate Link Stale option on the Secure FTD device

B.

Establish a routing protocol between R1 and R2.

C.

Disable hardware bypass on the Secure FTD device.

D.

Implement autostate functionality on the Gi0/2 interface of R2

Buy Now
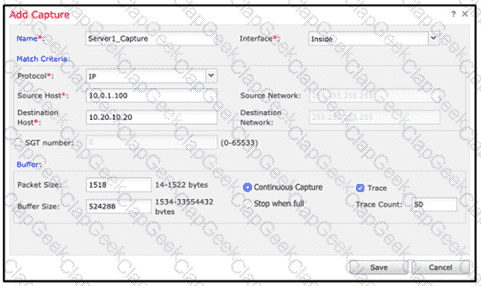
Questions 79

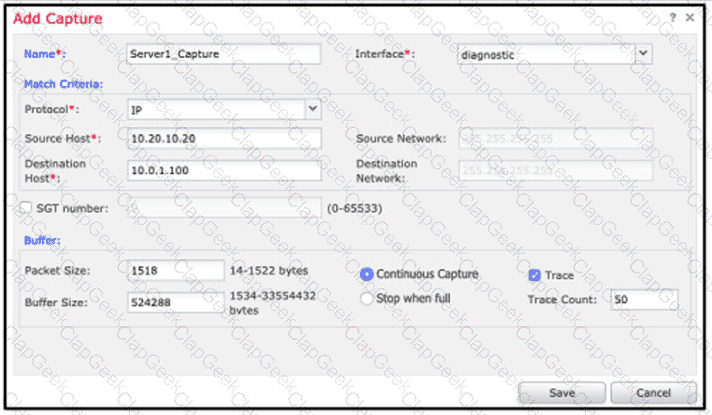
An engineer is troubleshooting a device that cannot connect to a web server. The connection is initiated from the Cisco FTD inside interface and attempting to reach 10.0.1.100 over the non-standard port of 9443 The host the engineer is attempting the connection from is at the IP address of 10.20.10.20. In order to determine what is happening to the packets on the network, the engineer decides to use the FTD packet capture tool Which capture configuration should be used to gather the information needed to troubleshoot this issue?

A)

B)

C)

D)

Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Buy Now
Questions 80

A network administrator is configuring a Cisco AMP public cloud instance and wants to capture infections and polymorphic variants of a threat to help detect families of malware. Which detection engine meets this requirement?

Options:

A.

RBAC

B.

Tetra

C.

Ethos

D.

Spero

Buy Now
Questions 81

What is the purpose of the IRB feature in next-generation firewall?

Options:

A.

To allow multiple physical interfaces to be part of the same VLAN

B.

To enable transparent bridging between two Layer 2 interfaces

C.

To block routing between two Layer 3 interfaces

D.

To configure NAT in transparent mode

Buy Now
Questions 82

A network engineer is planning on replacing an Active/Standby pair of physical Cisco Secure Firewall ASAs with a pair of Cisco Secure Firewall Threat Defense Virtual appliances. Which two virtual environments support the current High Availability configuration? (Choose two.)

Options:

A.

KVM

B.

Azure

C.

ESXi

D.

AWS

E.

Openstack

Buy Now
Questions 83

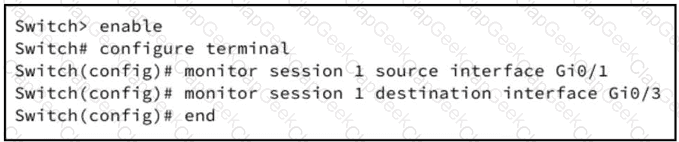
An engineer must configure a SPAN session to monitor traffic by using a Cisco Secure IPS device in passive mode. Cisco Secure IPS interface Gi0/1 is connected to Cisco Catalyst switch interface Gi0/3. Which SPAN configuration meets the requirement?

Options:

A.

Switch(config)# monitor source interface Gi0/1Switch(config)# monitor destination interface Gi0/3

B.

Switch(config)# monitor session 1 source interface Gi0/3Switch(config)# monitor session 1 destination interface Gi0/3

C.

Switch(config)# monitor session 1 source interface Gi0/1Switch(config)# monitor session 1 destination interface Gi0/3

D.

Switch(config)# monitor source interface Gi0/1Switch(config)# monitor destination interface Gi0/3

Buy Now
Questions 84

A network engineer is configuring URL Filtering on Firepower Threat Defense. Which two port requirements on the Firepower Management Center must be validated to allow communication with the cloud service? (Choose two.)

Options:

A.

outbound port TCP/443

B.

inbound port TCP/80

C.

outbound port TCP/8080

D.

inbound port TCP/443

E.

outbound port TCP/80

Buy Now
Questions 85

Which two conditions must be met to enable high availability between two Cisco FTD devices? (Choose two.)

Options:

A.

same flash memory size

B.

same NTP configuration

C.

same DHCP/PPoE configuration

D.

same host name

E.

same number of interfaces

Buy Now
Questions 86

An engineer must perform a packet capture on a Cisco Secure Firewall Threat Defense device to confirm the MAC address of the host using IP address 192.168.100.100 while troubleshooting an ARP issue. What is the correct tcpdump command syntax to ensure that the MAC address appears in the packet capture output?

Options:

A.

-w capture.pcap -s 1518 host 192.168.100.100 mac

B.

-nm src 192.168.100.100

C.

-w capture.pcap -s 1518 host 192.168.100.100 ether

D.

-ne src 192.168.100.100

Buy Now
Questions 87

An engineer wants to connect a single IP subnet through a Cisco FTD firewall and enforce policy. There is a requirement to present the internal IP subnet to the outside as a different IP address. What must be configured to meet these requirements?

Options:

A.

Configure the downstream router to perform NAT.

B.

Configure the upstream router to perform NAT.

C.

Configure the Cisco FTD firewall in routed mode with NAT enabled.

D.

Configure the Cisco FTD firewall in transparent mode with NAT enabled.

Buy Now
Questions 88

A network engineer is logged into the Cisco AMP for Endpoints console and sees a malicious verdict for an identified SHA-256 hash. Which configuration is needed to mitigate this threat?

Options:

A.

Add the hash to the simple custom deletion list.

B.

Use regular expressions to block the malicious file.

C.

Enable a personal firewall in the infected endpoint.

D.

Add the hash from the infected endpoint to the network block list.

Buy Now
Questions 89

Due to an Increase in malicious events, a security engineer must generate a threat report to include intrusion in events, malware events, and security intelligence events. How Is this information collected in a single report?

Options:

A.

Run the default Firepower report.

B.

Export the Attacks Risk report.

C.

Generate a malware report.

D.

Create a Custom report.

Buy Now
Questions 90

Which language searches and analyzes data within Splunk for threat detection?

Options:

A.

SQL

B.

XML

C.

SPL

D.

JSON

Buy Now
Questions 91

A network administrator is configuring a site-to-site IPsec VPN to a router sitting behind a Cisco FTD. The administrator has configured an access policy to allow traffic to this device on UDP 500, 4500, and ESP VPN traffic is not working. Which action resolves this issue?

Options:

A.

Set the allow action in the access policy to trust.

B.

Enable IPsec inspection on the access policy.

C.

Modify the NAT policy to use the interface PAT.

D.

Change the access policy to allow all ports.

Buy Now
Questions 92

Which Cisco Firepower Threat Defense, which two interface settings are required when configuring a routed interface? (Choose two.)

Options:

A.

Redundant Interface

B.

EtherChannel

C.

Speed

D.

Media Type

E.

Duplex

Buy Now
Questions 93

An engineer wants to perform a packet capture on the Cisco FTD to confirm that the host using IP address 192 168.100.100 has the MAC address of 0042 7734.103 to help troubleshoot aconnectivity issue What is the correct tcpdump command syntax to ensure that the MAC address appears in the packet capture output?

Options:

A.

-nm src 192.168.100.100

B.

-ne src 192.168.100.100

C.

-w capture.pcap -s 1518 host 192.168.100.100 mac

D.

-w capture.pcap -s 1518 host 192.168.100.100 ether

Buy Now
Questions 94

A security engineer is configuring a remote Cisco FTD that has limited resources and internet bandwidth. Which malware action and protection option should be configured to reduce the requirement for cloud lookups?

Options:

A.

Malware Cloud Lookup and dynamic analysis

B.

Block Malware action and dynamic analysis

C.

Block Malware action and local malware analysis

D.

Block File action and local malware analysis

Buy Now
Questions 95

A company is deploying intrusion protection on multiple Cisco FTD appliances managed by Cisco FMC. Which system-provided policy must be selected if speed and detection are priorities?

Options:

A.

Connectivity Over Security

B.

Security Over Connectivity

C.

Maximum Detection

D.

Balanced Security and Connectivity

Buy Now
Questions 96

An engineer is setting up a remote access VPN on a Cisco FTD device and wants to define which traffic gets sent over the VPN tunnel. Which named object type in Cisco FMC must be used to accomplish this task?

Options:

A.

split tunnel

B.

crypto map

C.

access list

D.

route map

Buy Now
Questions 97

An organization is configuring a new Cisco Firepower High Availability deployment. Which actionmust be taken to ensure that failover is as seamless as possible to end users?

Options:

A.

Set up a virtual failover MAC address between chassis.

B.

Use a dedicated stateful link between chassis.

C.

Load the same software version on both chassis.

D.

Set the same FQDN for both chassis.

Buy Now
Questions 98

How should a high-availability pair of Cisco Secure Firewall Threat Defense Virtual appliances be deployed to Cisco Secure Firewall Management Center?

Options:

A.

Configure high availability first, then add only the primary Cisco Secure Firewall Threat Defense Virtual appliance to Cisco Secure Firewall Management Center.

B.

Add the primary and secondary Cisco Secure Firewall Threat Defense Virtual appliances to Cisco Secure Firewall Management Center first, then configure high availability.

C.

Add the primary appliance to Cisco Secure Firewall Management Center first, then configure high availability.

D.

Configure high availability first, then add the primary and secondary appliances to Cisco Secure Firewall Management Center.

Buy Now
Questions 99

An organization is using a Cisco FTD and Cisco ISE to perform identity-based access controls. A network administrator is analyzing the Cisco FTD events and notices that unknown user traffic is being allowed through the firewall. How should this be addressed to block the traffic while allowing legitimate user traffic?

Options:

A.

Modify the Cisco ISE authorization policy to deny this access to the user.

B.

Modify Cisco ISE to send only legitimate usernames to the Cisco FTD.

C.

Add the unknown user in the Access Control Policy in Cisco FTD.

D.

Add the unknown user in the Malware & File Policy in Cisco FTD.

Buy Now
Questions 100

What is the role of realms in the Cisco ISE and Cisco FMC integration?

Options:

A.

AD definition

B.

TACACS+ database

C.

Cisco ISE context

D.

Cisco Secure Firewall VDC

Buy Now
Questions 101

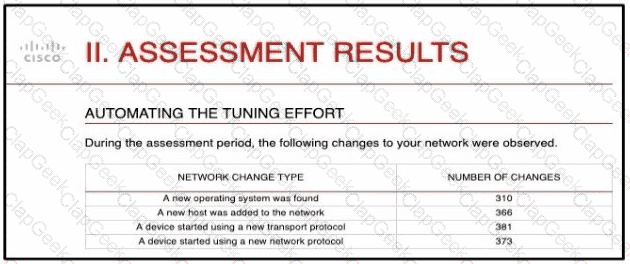
Refer to the exhibit.

And engineer is analyzing the Attacks Risk Report and finds that there are over 300 instances of new operating systems being seen on the network How is the Firepower configuration updated to protect these new operating systems?

Options:

A.

Cisco Firepower automatically updates the policies.

B.

The administrator requests a Remediation Recommendation Report from Cisco Firepower

C.

Cisco Firepower gives recommendations to update the policies.

D.

The administrator manually updates the policies.

Buy Now
Questions 102

Which limitation applies to Cisco Firepower Management Center dashboards in a multidomain environment?

Options:

A.

Child domains can view but not edit dashboards that originate from an ancestor domain.

B.

Child domains have access to only a limited set of widgets from ancestor domains.

C.

Only the administrator of the top ancestor domain can view dashboards.

D.

Child domains cannot view dashboards that originate from an ancestor domain.

Buy Now
Questions 103

An engineer must deploy a high-availability pair that includes two Cisco Secure Firewall Threat Defense devices. The deployment must provide a mechanism that protects synchronization traffic between the members. Which action must the engineer take?

Options:

A.

Configure an SSL VPN tunnel between the units.

B.

Select the Key Generation method for IPsec encryption.

C.

Encrypt the synchronization traffic with SSL.

D.

Clear the commit queue when synchronization begins.

Buy Now
Questions 104

How does Cisco Secure Cloud Analytics handle information about network traffic?

Options:

A.

It forwards the information to other devices without storing it.

B.

It performs behavioral analysis on events and network-flow data.

C.

It performs heuristic analysis on events and network-flow data.

D.

It stores the information in a database without performing any analysis.

Buy Now
Questions 105

A network engineer must provide redundancy between two Cisco FTD devices. The redundancy configuration must include automatic configuration, translation, and connection updates. After the initial configuration of the two appliances, which two steps must be taken to proceed with the redundancy configuration? (Choose two.)

Options:

A.

Configure the virtual MAC address on the failover link.

B.

Disable hellos on the inside interface.

C.

Configure the standby IP addresses.

D.

Ensure the high availability license is enabled.

E.

Configure the failover link with stateful properties.

Buy Now
Questions 106

A security engineer must configure a Cisco FTD appliance to inspect traffic coming from the internet. The Internet traffic will be mirrored from the Cisco Catalyst 9300 Switch. Which configuration accomplishes the task?

Options:

A.

Set interface configuration mode to none.

B.

Set the firewall mode to transparent.

C.

Set the firewall mode to routed.

D.

Set interface configuration mode to passive.

Buy Now
Questions 107

Which interface type allows packets to be dropped?

Options:

A.

passive

B.

inline

C.

ERSPAN

D.

TAP

Buy Now
Questions 108

Which command must be run to generate troubleshooting files on an FTD?

Options:

A.

system support view-files

B.

sudo sf_troubleshoot.pl

C.

system generate-troubleshoot all

D.

show tech-support

Buy Now
Questions 109

An engineer must investigate a connectivity issue by using Cisco Secure Firewall Management Center to access the Packet Capture feature on a Cisco Secure Firewall Threat Defense

device. The engineer must see a real packet going through the Secure Firewall Threat Defense device and the Snort detection actions. While reviewing the packet capture, the engineer

discovers that the Snort detection actions are missing. Which action must the engineer take to resolve the issue?
Options:

A.

Specify the packet size.

B.

Specify the buffer size.

C.

Enable the Continuous Capture option.

D.

Enable the Trace option.

Buy Now
Questions 110

What is the RTC workflow when the infected endpoint is identified?

Options:

A.

Cisco ISE instructs Cisco AMP to contain the infected endpoint.

B.

Cisco ISE instructs Cisco FMC to contain the infected endpoint.

C.

Cisco AMP instructs Cisco FMC to contain the infected endpoint.

D.

Cisco FMC instructs Cisco ISE to contain the infected endpoint.

Buy Now
Questions 111

A network administrator needs to create a policy on Cisco Firepower to fast-path traffic to avoid Layer 7 inspection. The rate at which traffic is inspected must be optimized. What must be done to achieve this goal?

Options:

A.

Enable lhe FXOS for multi-instance.

B.

Configure a prefilter policy.

C.

Configure modular policy framework.

D.

Disable TCP inspection.

Buy Now
Questions 112

A security engineer is deploying a Cisco Secure Firewall Threat Defense device through Cisco Secure Firewall Management Center. The Threat license is installed, the Encrypted Visibility Engine is enabled in the access control policy Decryption policy is configured with the Decrypt - Resign action to inspect outbound TLS/SSL traffic. Users report that a banking applications repeatedly fails to load. The engineer confirms the endpoint performs certificate pinning to validate the server certificate. Engineer must allow the traffic to pass while all other outbound traffic continues to be inspected. The engineer created a rule that matches banking category and placed the rule above Decrypt - Resign policy. Which decryption rule action must be configured to meet the requirement?

Options:

A.

Decrypt - Known Key

B.

Do Not Decrypt

C.

Trust

D.

Block

Buy Now
Questions 113

An engineer must implement static route tracking on a Cisco Secure Firewall Threat Defense appliance. Static route and IP SLA operation has already been configured. Static route must be removed from the routing table if the tracked object is unreachable. Which action must the engineer take next to meet the requirement?

Options:

A.

Implement a secondary route that has a higher precedence.

B.

Enable the IP SLA Responder on the backup path interface.

C.

Assign a tracking object to the static route and the IP SLA operation.

D.

Enable an ICMP redirect message on the interface connected to the backup path.

Buy Now
Questions 114

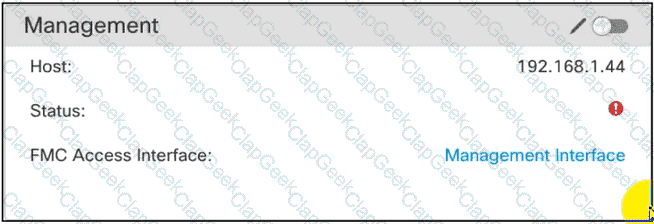
Refer to the exhibit.

What is the effect of the existing Cisco FMC configuration?

Options:

A.

The remote management port for communication between the Cisco FMC and the managed device changes to port 8443.

B.

The managed device is deleted from the Cisco FMC.

C.

The SSL-encrypted communication channel between the Cisco FMC and the managed device becomes plain-text communication channel.

D.

The management connection between the Cisco FMC and the Cisco FTD is disabled.

Buy Now
Questions 115

An engineer is troubleshooting an intermittent connectivity issue on a Cisco Secure Firewall Threat Defense appliance and must collect 24 hours ' worth of data. The engineer started a packet capture. Whenever it stopsprematurely during this time period. The engineer notices that the packet capture butter size is set to the default of 32 MB Which butter S170 is the maximum that the engineer must sot to able the packet capture to run successfully?

Options:

A.

64 MB

B.

1 GB

C.

10 GB

D.

100 GB

Buy Now
Questions 116

A company is deploying Cisco Secure Endpoint private cloud. The Secure Endpoint private cloud instance has already been deployed by the server administrator. The server administrator provided the hostname of the private cloud instance to the network engineer via email. What additional information does the network engineer require from the server administrator to be able to make the connection to Secure Endpoint private cloud in Cisco Secure Firewall Management Centre?

Options:

A.

SSL certificate for the Secure Endpoint ornate cloud instance

B.

Internet access for the Secure End point private cloud to reach the Secure Endpoint public cloud

C.

Username and password to the Secure Endpoint private cloud instance

D.

IP address and port number for the connection proxy

Buy Now
Questions 117

An engineer has been tasked with providing disaster recovery for an organization ' s primary Cisco FMC. What must be done on the primary and secondary Cisco FMCs to ensure that a copy of the original corporate policy is available if the primary Cisco FMC fails?

Options:

A.

Configure high-availability in both the primary and secondary Cisco FMCs

B.

Connect the primary and secondary Cisco FMC devices with Category 6 cables of not more than 10 meters in length.

C.

Place the active Cisco FMC device on the same trusted management network as the standby device

D.

Restore the primary Cisco FMC backup configuration to the secondary Cisco FMC device when the primary device fails

Buy Now
Questions 118

Which firewall mode is Cisco Secure Firewall Threat Defense in when two physical interfaces are assigned to a named BVI?

Options:

A.

Routed

B.

Transparent

C.

In-line

D.

IPS only

Buy Now
Questions 119

An engineer is troubleshooting application failures through a FTD deployment. While using the FMC CLI. it has been determined that the traffic in question is not matching the desired policy. What should be done to correct this?

Options:

A.

Use the system support firewall-engine-debug command to determine which rules the traffic matchingand modify the rule accordingly

B.

Use the system support application-identification-debug command to determine which rules the traffic matching and modify the rule accordingly

C.

Use the system support firewall-engine-dump-user-f density-data command to change the policy and allow the application through the firewall.

D.

Use the system support network-options command to fine tune the policy.

Buy Now
Questions 120

In which two ways do access control policies operate on a Cisco Firepower system? (Choose two.)

Options:

A.

Traffic inspection can be interrupted temporarily when configuration changes are deployed.

B.

The system performs intrusion inspection followed by file inspection.

C.

They can block traffic based on Security Intelligence data.

D.

File policies use an associated variable set to perform intrusion prevention.

E.

The system performs a preliminary inspection on trusted traffic to validate that it matches the trusted parameters.

Buy Now
Questions 121

What are two application layer preprocessors? (Choose two.)

Options:

A.

CIFS

B.

IMAP

C.

SSL

D.

DNP3

E.

ICMP

Buy Now
Questions 122

With a recent summer time change, system logs are showing activity that occurred to be an hour behind real time Which action should be taken to resolve this issue?

Options:

A.

Manually adjust the time to the correct hour on all managed devices

B.

Configure the system clock settings to use NTP with Daylight Savings checked

C.

Manually adjust the time to the correct hour on the Cisco FMC.

D.

Configure the system clock settings to use NTP

Buy Now
Questions 123

An engineer must configure a SPAN to monitor traffic by using a Cisco Secure IPS device in passive mode. The Cisco Secure IPS interface Gi0/1 is connected to Cisco Catalyst Switch interface Gi0/3. Which SPAN configuration meets the requirement?

A)
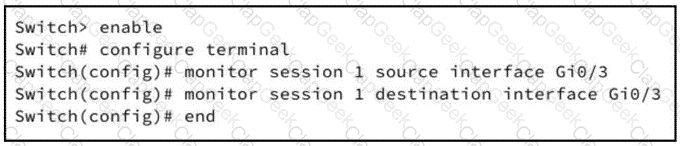
B)
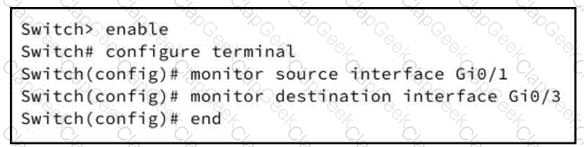
C)
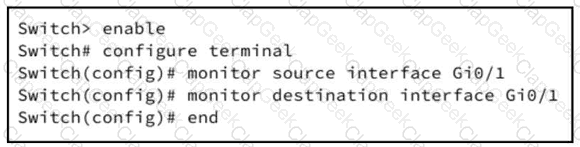
D)
Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Buy Now
Questions 124

Which two actions can be used in an access control policy rule? (Choose two.)

Options:

A.

Block with Reset

B.

Monitor

C.

Analyze

D.

Discover

E.

Block ALL

Buy Now
Questions 125

An engineer must configure a new identity policy in Cisco Firepower Management Center. Active authentication must be configured by using a Kerberos connection. Which two realms must be configured? (Choose two.)

Options:

A.

Directory password

B.

Active directory join password

C.

Active directory primary domain

D.

Active directory join username

E.

Directory username

Buy Now
Questions 126

An engineer is configuring two new Cisco Secure Firewall Threat Defense devices to replace the existing firewalls. Network traffic must be analyzed for intrusion events without impacting the traffic. What must the engineer implement next to accomplish the goal?

Options:

A.

Passive mode

B.

Inline Pair in Tap mode

C.

ERSPAN Passive mode

D.

Inline Pair mode

Buy Now
Questions 127

Network traffic coining from an organization ' s CEO must never be denied. Which access control policy configuration option should be used if the deployment engineer is not permitted to create a rule to allow all traffic?

Options:

A.

Configure firewall bypass.

B.

Change the intrusion policy from security to balance.

C.

Configure a trust policy for the CEO.

D.

Create a NAT policy just for the CEO.

Buy Now
Questions 128

An engineer Is configuring a Cisco FTD device to place on the Finance VLAN to provide additional protection tor company financial data. The device must be deployed without requiring any changes on the end user workstations, which currently use DHCP lo obtain an IP address. How must the engineer deploy the device to meet this requirement?

Options:

A.

Deploy the device in routed mode and allow DHCP traffic in the access control policies.

B.

Deploy the device in routed made aid enable the DHCP Relay feature.

C.

Deploy the device in transparent mode and allow DHCP traffic in the access control policies

D.

Deploy the device in transparent mode and enable the DHCP Server feature.

Buy Now
Questions 129

Which two types of objects are reusable and supported by Cisco FMC? (Choose two.)

Options:

A.

dynamic key mapping objects that help link HTTP and HTTPS GET requests to Layer 7 application protocols.

B.

reputation-based objects that represent Security Intelligence feeds and lists, application filters based on category and reputation, and file lists

C.

network-based objects that represent IP address and networks, port/protocols pairs, VLAN tags, security zones, and origin/destination country

D.

network-based objects that represent FQDN mappings and networks, port/protocol pairs, VXLAN tags, security zones and origin/destination country

E.

reputation-based objects, such as URL categories

Buy Now
Questions 130

An engineer must build redundancy into the network and traffic must continuously flow if a redundant switch in front of the firewall goes down. What must be configured to accomplish this task?

Options:

A.

redundant interfaces on the firewall cluster mode and switches

B.

redundant interfaces on the firewall noncluster mode and switches

C.

vPC on the switches to the interface mode on the firewall duster

D.

vPC on the switches to the span EtherChannel on the firewall cluster

Buy Now
Questions 131

An organization has a compliancy requirement to protect servers from clients, however, the clients and servers all reside on the same Layer 3 network Without readdressing IP subnets for clients or servers, how is segmentation achieved?

Options:

A.

Deploy a firewall in transparent mode between the clients and servers.

B.

Change the IP addresses of the clients, while remaining on the same subnet.

C.

Deploy a firewall in routed mode between the clients and servers

D.

Change the IP addresses of the servers, while remaining on the same subnet

Buy Now
Questions 132

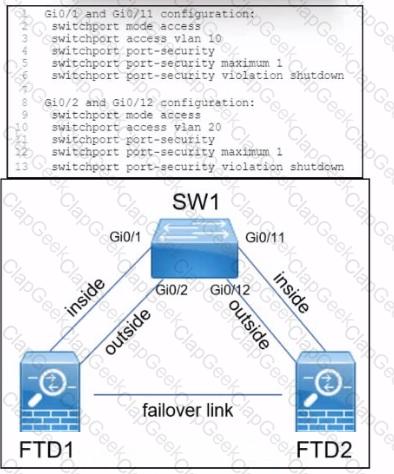
Refer to the exhibit.

A company is deploying a pair of Cisco Secure Firewall Threat defence devices named FTD1 and FTD2. FTD1 and FTD2 have been configured as an active/standby pair with a failover link but without a stateful link. What must be implemented next to ensure that users on the internal network still communicate with outside devices if FTD1 fails?

Options:

A.

Disable port security on the switch interfaces connected to FTD1 and FTD2.

B.

Set maximum secured addresses to two on the switch interfaces on FTD1 and FTD2.

C.

Connect and configure a stateful link and thon deploy the changes.

D.

Configure the spanning-tree PortFasI feature on SW1 and FTD2

Buy Now
Questions 133

A security engineer must configure policies tor a recently deployed Cisco FTD. The security policy for the company dictates that when five or more connections from external sources are initiated within 2 minutes, there is cause for concern. Which type of policy must be configured in Cisco FMC \z generate an alert when this condition is triggered?
Options:

A.

application detector

B.

access control

C.

intrusion

D.

correlation

Buy Now
Exam Code: 300-710
Exam Name: Securing Networks with Cisco Firepower (300-710 SNCF) v1.2
Last Update: Oct 4, 2026
Questions: 444
300-710 pdf

300-710 PDF

$23.75  $94.99
300-710 Engine

300-710 Testing Engine

$27.5  $109.99
300-710 PDF + Engine

300-710 PDF + Testing Engine

$36.25  $144.99