clapgeek logo
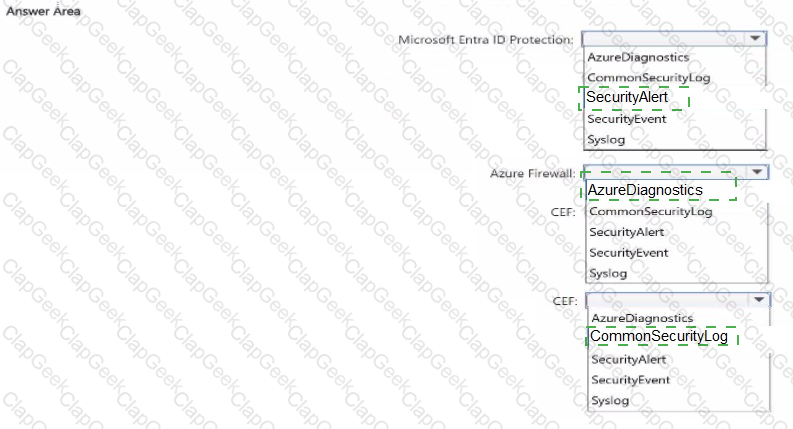
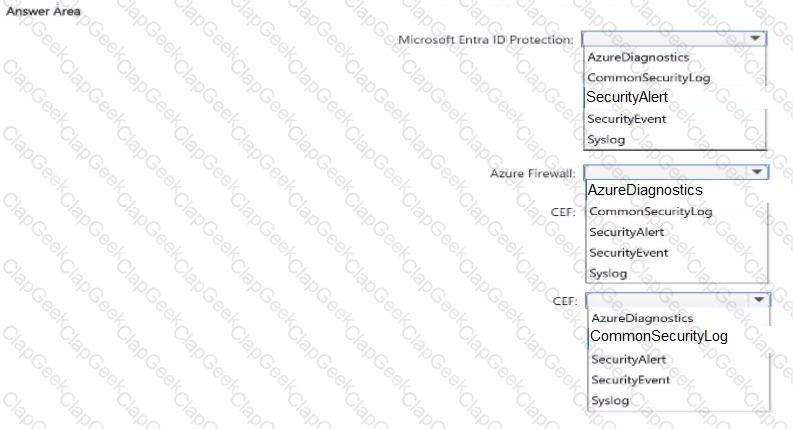
You have a Microsoft Sentinel workspace that has the following data connectors:
• Microsoft Entra ID Protection
• Azure Firewall
• Common Event Formal (CEF)
You need to ensure that data is being ingested from each connector.
From the Logs query window, which table should you query for each connector? To answer, select the appropriate options in the answer area.
You have an Azure Subscription that contains the Azure App Service web apps shown in the following table.
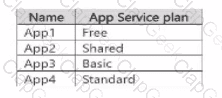
You purchase custom SSL certificates from a trusted third-party authority. To which apps can you assign the custom SSL certificates?
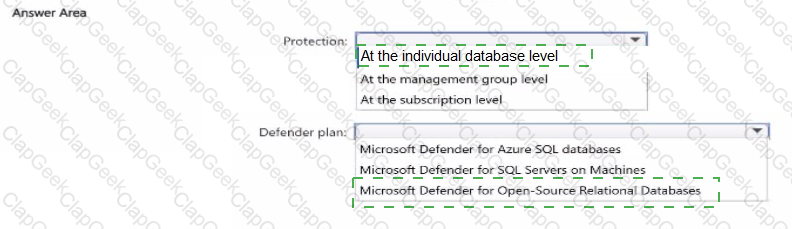
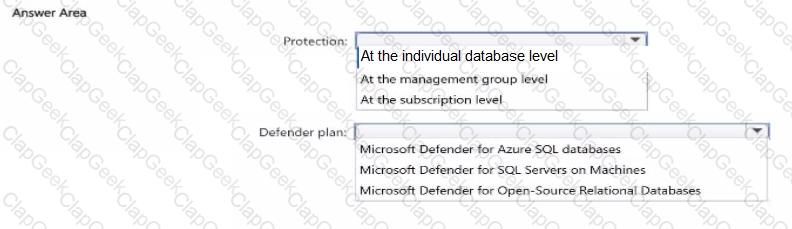
You have an Azure subscription that contains an Azure Database for PostgreSQL instance named 081.
You plan to protect OBI by using Microsoft Defender for Cloud.
You need to configure Defender for Cloud to detect anomalous activities and database exploitations for 061. The solution must NOT affect any other databases.
What should you enable? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have Microsoft Security Copilot agents that authenticate by using Microsoft Entra service principals.
You receive a Microsoft Defender alert triggered by the anomalous OAuth authentication of an agent ' s Microsoft Entra service principal.
You need to assess the impact of the agent identity and identify which resources are affected if the identity is abused for lateral movement The solution must minimize administrative effort.
What should you do?
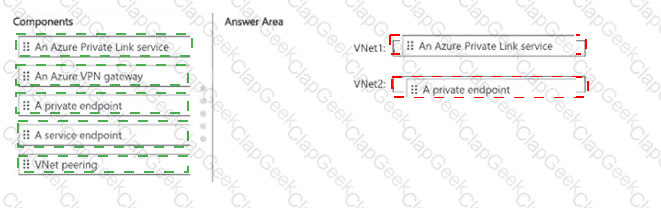
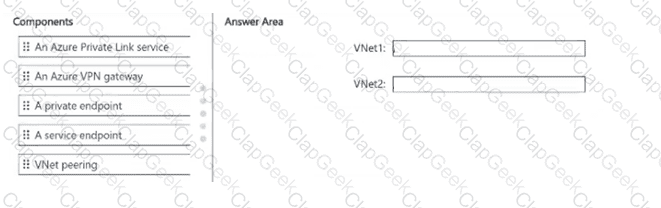
You have an Azure subscription named Sub1 that contains a virtual network named VNet1.
VNet1 contains multiple virtual machines, including two virtual machines named VM1 and VM2.
Sub1 is linked to a Microsoft Entra tenant named contoso.com.
A partner company has an Azure subscription named Sub2 that contains a virtual network named VNet2. VNet2 contains a virtual machine named VM3.
Sub2 is linked to a Microsoft Entra tenant named fabrikam.com.
VM1 and VM2 contain data used by an application that runs on VM3.
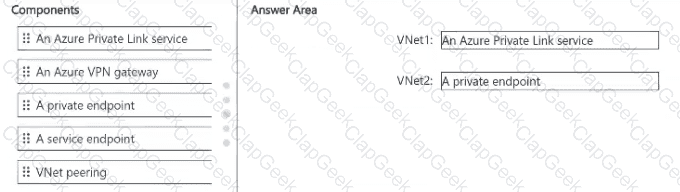
You need to ensure that VM3 can access VM1 and VM2. The solution must deny VM3 access to any other resources in Sub1.
What should you configure on each virtual network? To answer, drag the components to the correct virtual networks. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You are configuring a new Microsoft Sentinel workspace named Workspace1.
You have an external IT Service Management (ITSM) system that is NOT supported by any Microsoft Sentinel solutions in Azure Marketplace.
You need to ensure that Workspace1 creates service tickets in the ITSM system for all new security incidents.
What should you create?
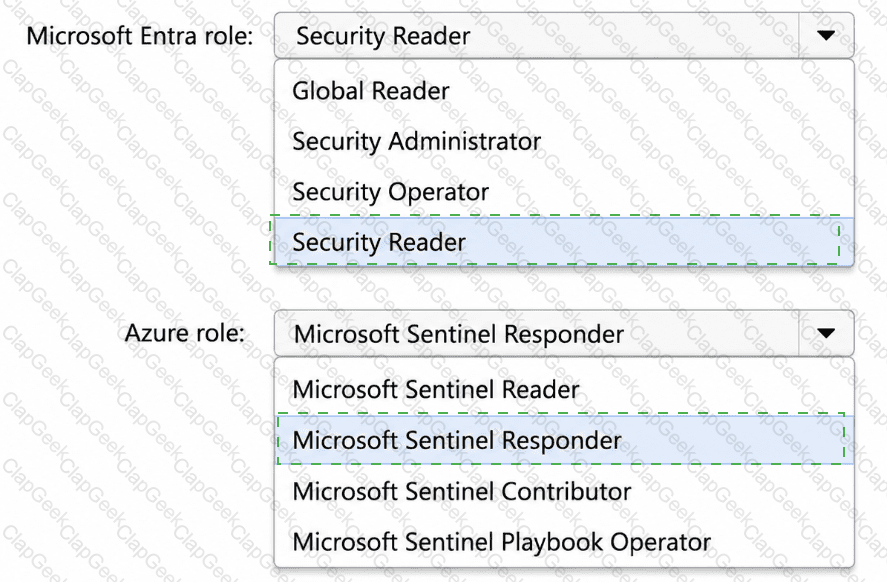
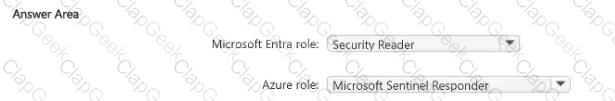
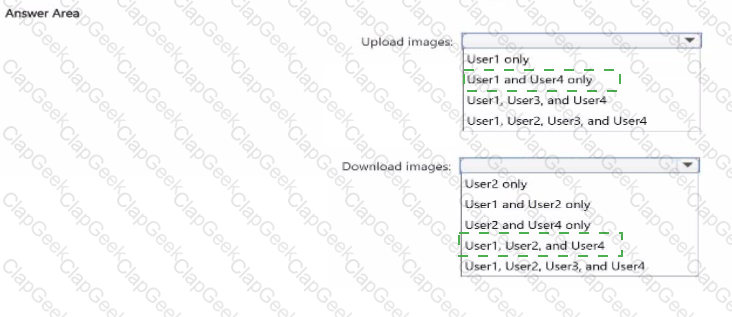
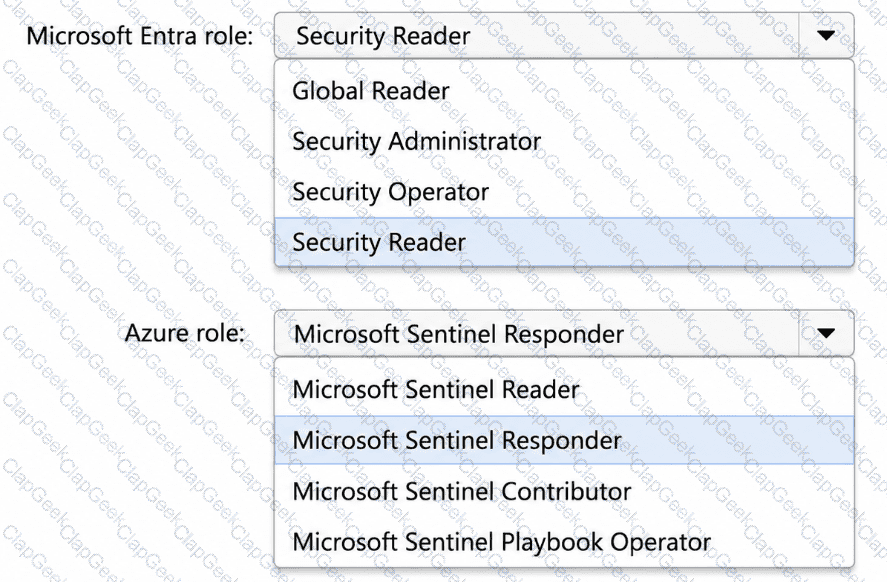
You have a Microsoft Sentinel workspace named Workspace1.
You hire a security consultant. You provide the consultant with a guest account named User1 in your Microsoft Entra tenant
You need to enable User1 to assign incidents in Workspace1.
Which roles should you assign to User1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You plan to deploy Microsoft 365 Copilot.
You discover that Copilot can access sensitive information in your Microsoft SharePoint Online libraries.
You need to automatically identify which SharePoint Online content has been shared between all internal users.
What should you create?
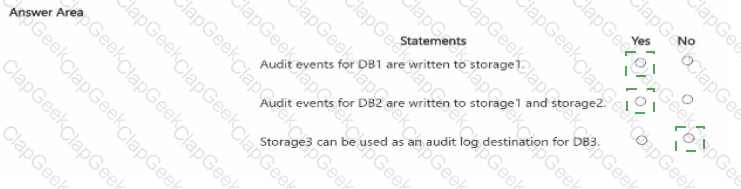
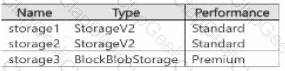
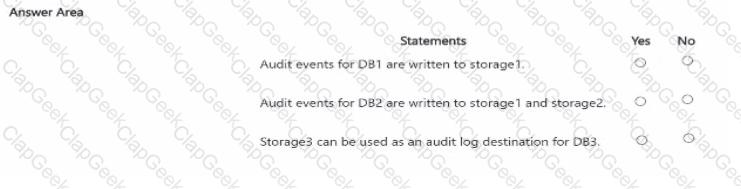
You have an Azure subscription that contains three storage accounts, an Azure SQL managed instance named SQL1, and three Azure SQL databases.
The storage accounts are configured as shown in the following table.
You use Microsoft Security Copilot.
Users are assigned either the Security Copilot Contributor role or the Security Copilot Owner role.
A contributor enables a custom plugin that is NOT approved, and some Security Copilot features in embedded experiences no longer function.
You need to ensure that plugins affecting all users can only be added by owners.
What should you do in the Plugin settings?
An application run2 on VM1 and VM2. The application is being migrated from storage account key authentication to Microsoft Entra authentication.
You review the current configuration and identify the following:
• VM1 and VM2 each have a system-assigned managed identity.
• Each application instance requests tokens by using only the local system-assigned managed identity.
• Network access to storage 1 from VMI and VM2 is allowed.
• No Azure RBAC data roles are assigned to the managed identities on storage1.
You need to enable the application on VM1 and VM2 to read and write blob data in storage1 by using Microsoft Entra authentication without changing how the application requests tokens.
Solution: You create a private endpoint for the blob service of storage1.
Does this meet the goal?
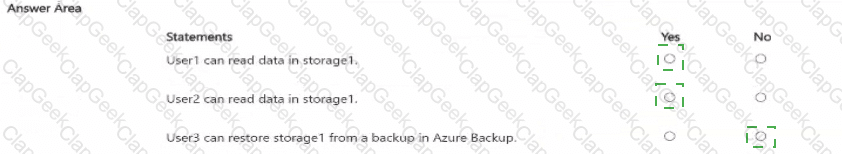
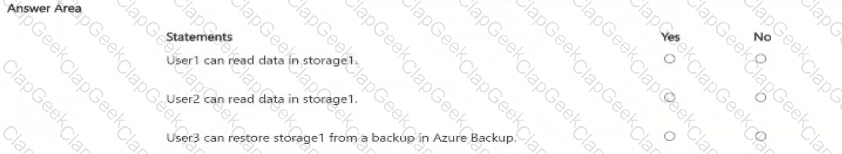
You have an Azure subscription that contains a resource group named RG1. RG1 contains a storage account named storage1. You have two custom Azure roles named Role1 and Role2 that are scoped to RG1. The permissions for Role1 are shown in the following JSON code.

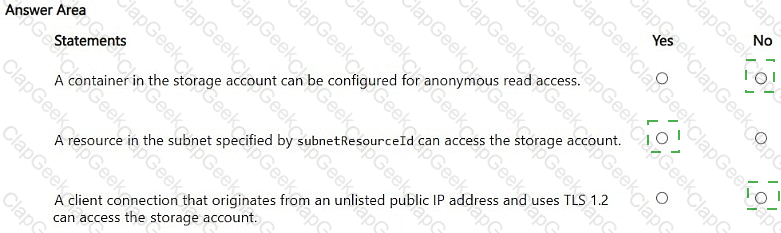
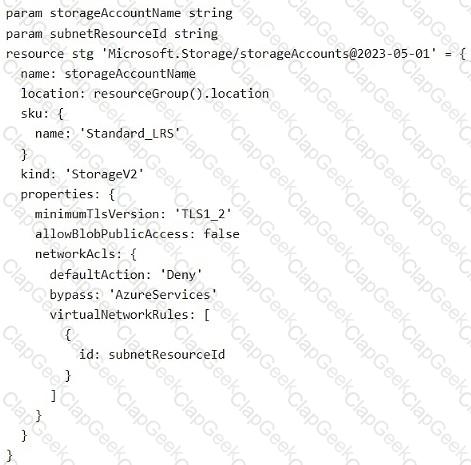
You are implementing security controls for an Azure Storage account by using infrastructure as code (IaC).
You deploy the following Bicep code.
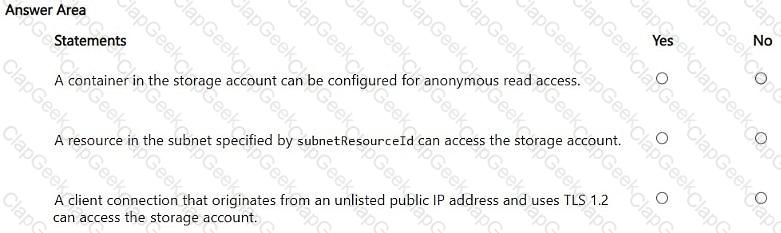
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
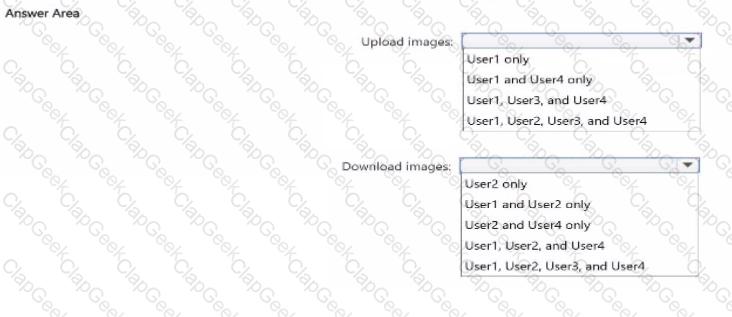
You have an Azure Container Registry named Registry1-
You add role assignments for Registry! as shown in the following table.
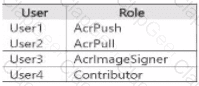
You have a Microsoft 365 subscription.
You use Microsoft Entra Agent ID to manage an agent identity.
You manage AI agents from the Microsoft 365 admin center.
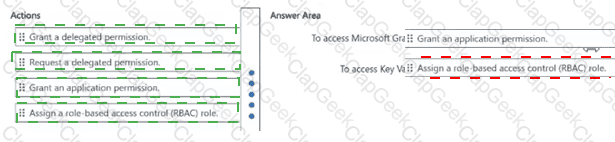
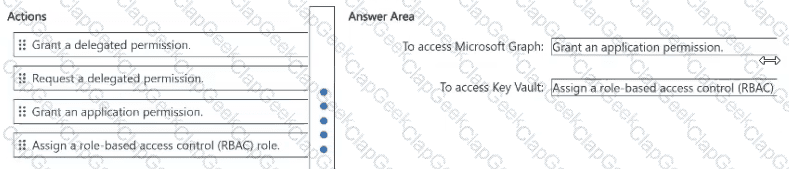
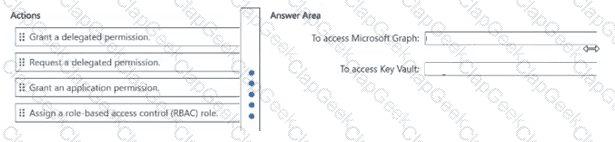
An autonomous agent named Agent1 runs without a signed-in user. The agent must access Microsoft Graph and read secrets from a single Azure key vault.
You need to grant Agent 1 access to Microsoft Graph and Key Vault without requiring user interaction or consent at runtime.
What should you do for the agent identity? To answer, drag the appropriate actions to the correct services. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
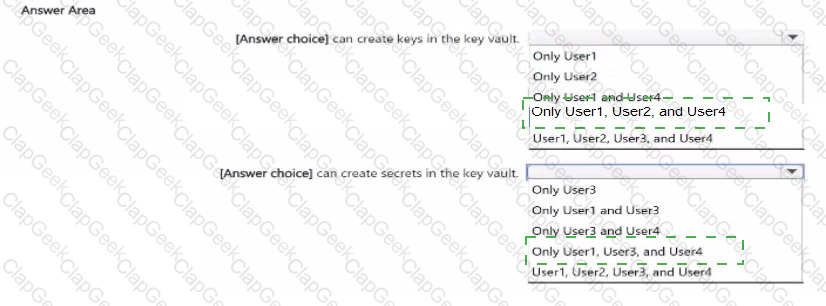
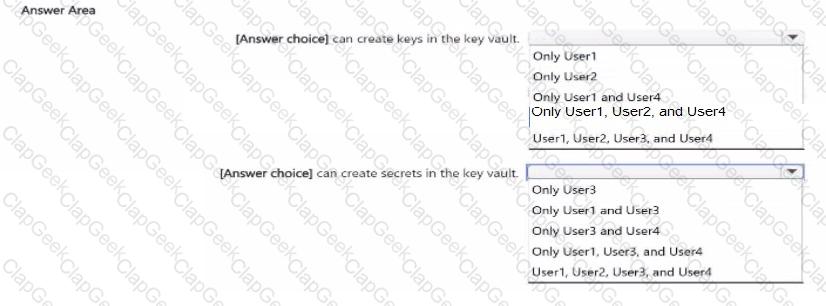
You have an Azure subscription that contains an Azure Key vault. The role assignments for the vault are shown in the following.
You have an Azure subscription named Sub1. Sub1 contains 20 virtual machines that run Windows Server.
Sub1 has the Microsoft Defender for Cloud Defender Cloud Security Posture Management (CSPM) plan enabled.
You need to ensure that all the virtual machines are scanned automatically for known security flaws and misconfigurations.
What should you use?
You have an Azure subscription named Sub1 that contains a resource group named RG1.
RG1 contains a virtual network named VNet1 and a storage account named storage1. Several engineers are assigned the Owner role for Sub1.
You need to prevent updates to and deletions from VNet1. The solution must ensure that engineers can continue updating other resources in RG1.
Which lock should you apply?
You have a Microsoft Entra tenant that contains a group named Group1.
You plan to target Group1 to use the Microsoft Authenticator authentication method.
You need to ensure that the members in Group1 can use the Authenticator app as their primary authentication method.
What should you do?
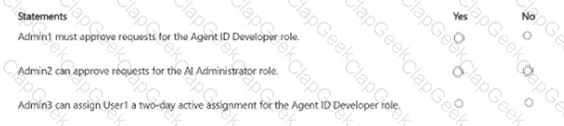
For each of the following statements, select Yes if the statement is true Otherwise, select No.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage1. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You add each virtual machine to a role on storage1.
Does this meet the goal?
You need to protect the applications hosted on AKS1. The solution must meet the technical requirements.
Which Defender for Cloud plan should you enable?
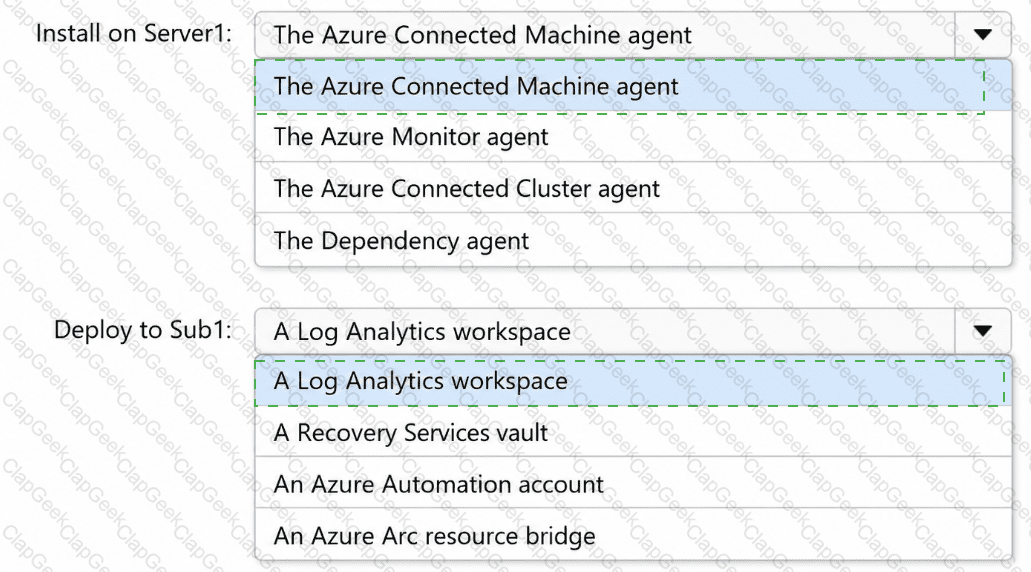
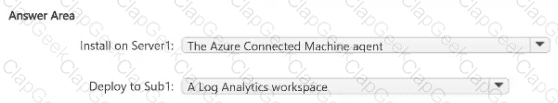
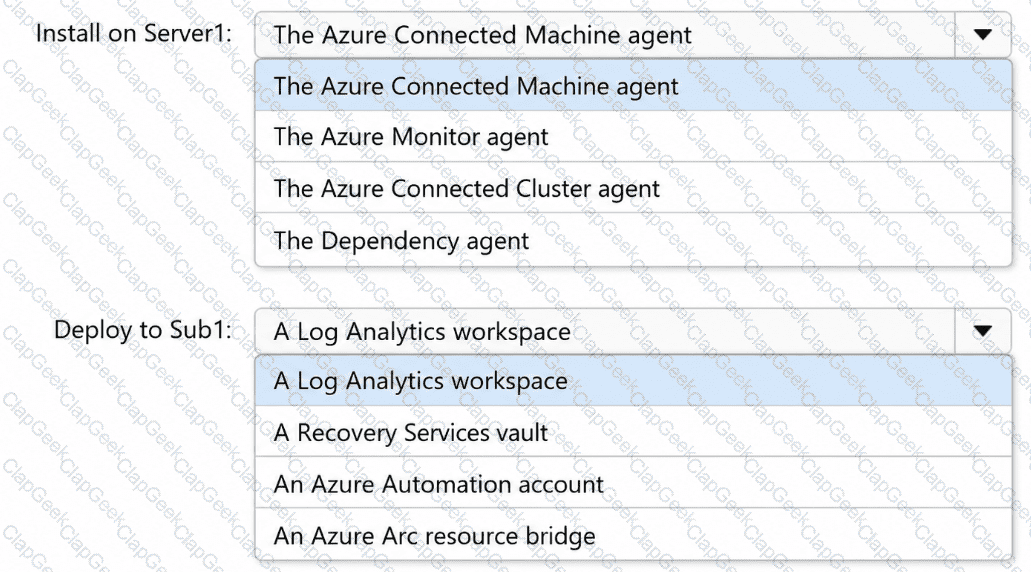
You need to configure Server1 to meet the technical requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You create a private endpoint on storage1.
Does this meet the goal?
You need to implement the planned change for SQLdb1
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution: You create a playbook
Does this meet the goal?
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage1. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You add each virtual machine to a security group, and then add the security group to a role on storage1.
Does this meet the goal?
You need to implement the planned change for the AKS1 integration.
What should you configure for AKS1?
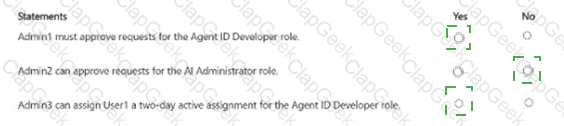
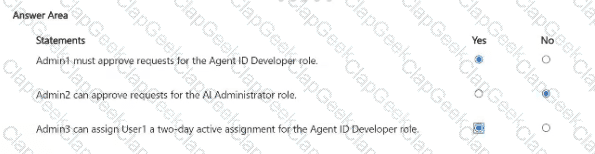
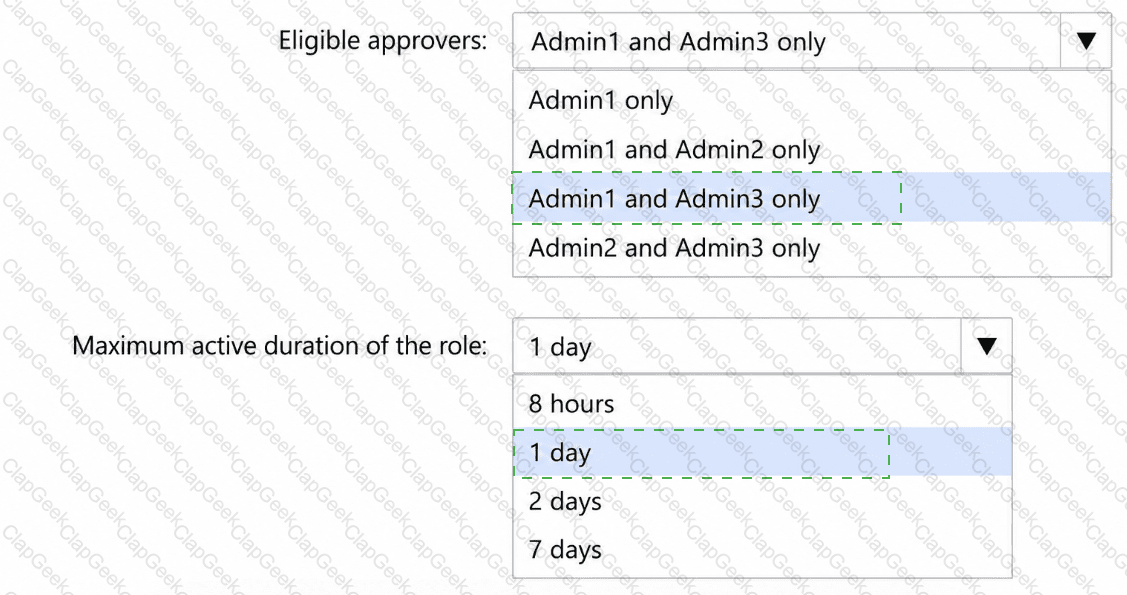
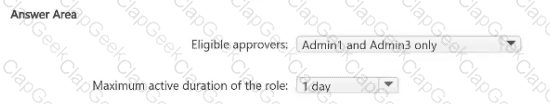
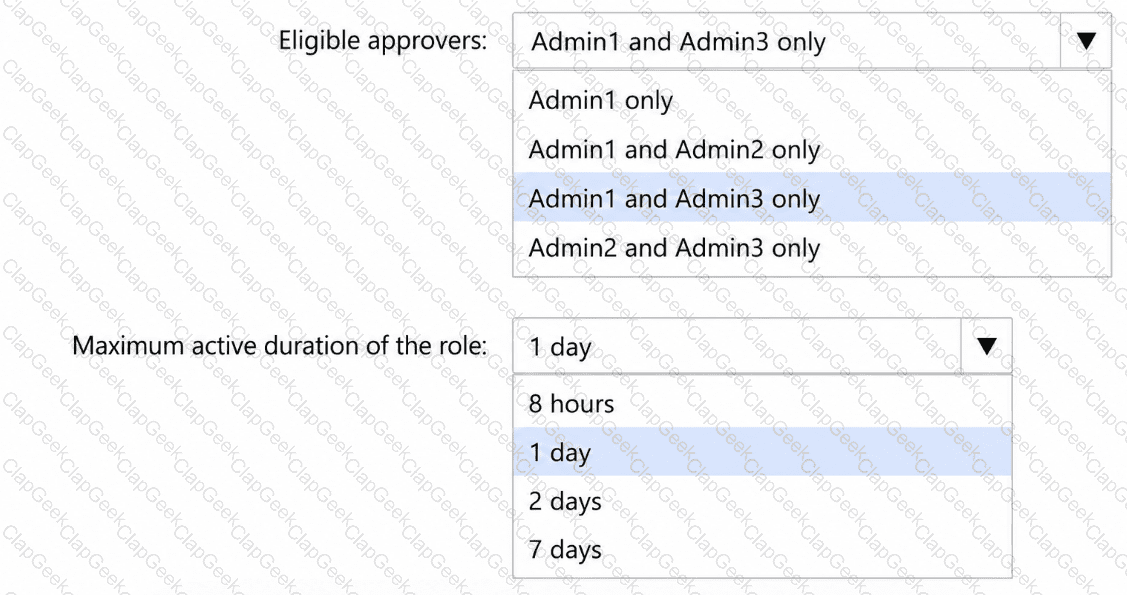
User1 has requested to use the AI Administrator role.
Which approvers can approve the request, and how long will User1 be an AI administrator after the role is approved? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution: You create an analytics rule.
Does this meet the goal?
You need to configure Microsoft Sentinel to meet the technical requirements.
To what should you set Analytics retention for DnsEvents?
You need to implement the planned change for storage2 The solution must meet the technical requirements for storage encryption.
What should you do?
You need to implement the function apps to meet the technical requirements.
Which apps should you include in the implementation?
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage1. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You create a user-assigned managed identity, assign the identity to each virtual machine, and then add each managed identity to a role on storage1.
Does this meet the goal?
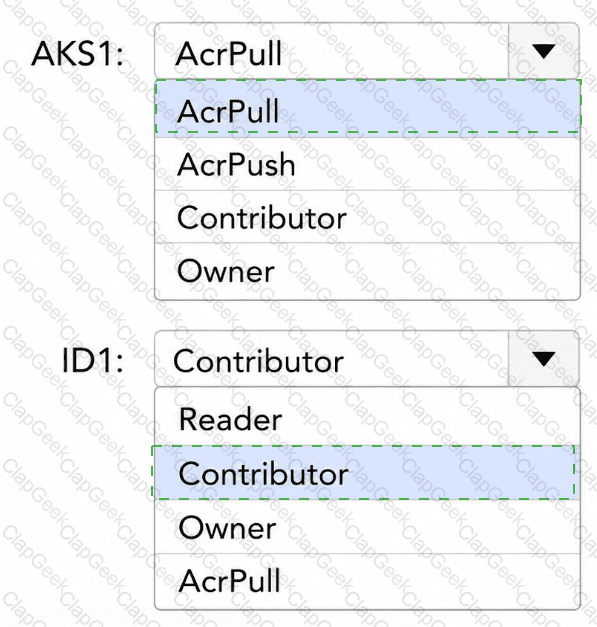
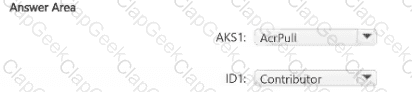
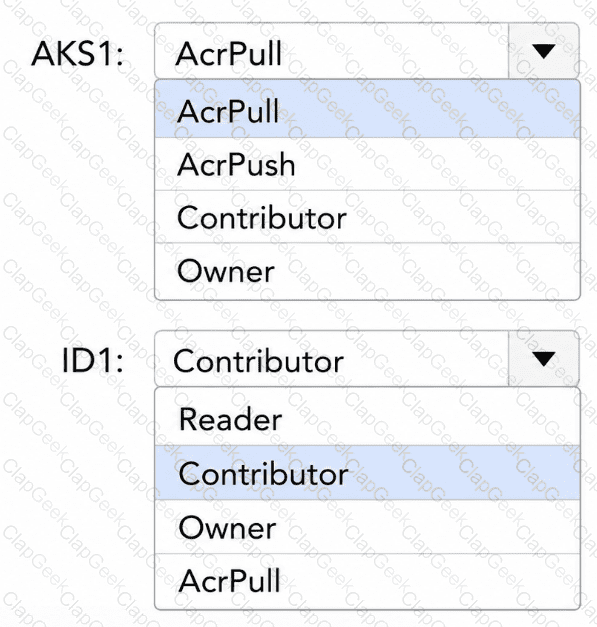
You need to configure the AKS1 and ID 1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Note. This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem
After you answer a question in this section, you will NOT be able to return. As a result these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution You create a hunting query.
Does this meet the goal’
TESTED 20 Sep 2026